Statistics

52.40.42.113

IP address · suspicious phishing activity

URLs
3
Brands targeted
2
TLS issuers
2
Country
United StatesUnited States
ASN
AS16509
Network
AWS EC2 us-west-2 · rentable hosting · 52.40.0.0/14
Official provider IP range of this IP. Context only, not a verdict.

A single IP address can host many unrelated websites at once, especially behind shared hosting or a CDN. Several detections on one address often mean a shared server or reverse proxy is being abused, not that every site behind it is malicious.

Suspicious sites — confidence is not always 100%. Use for Threat Hunting or watchlists.
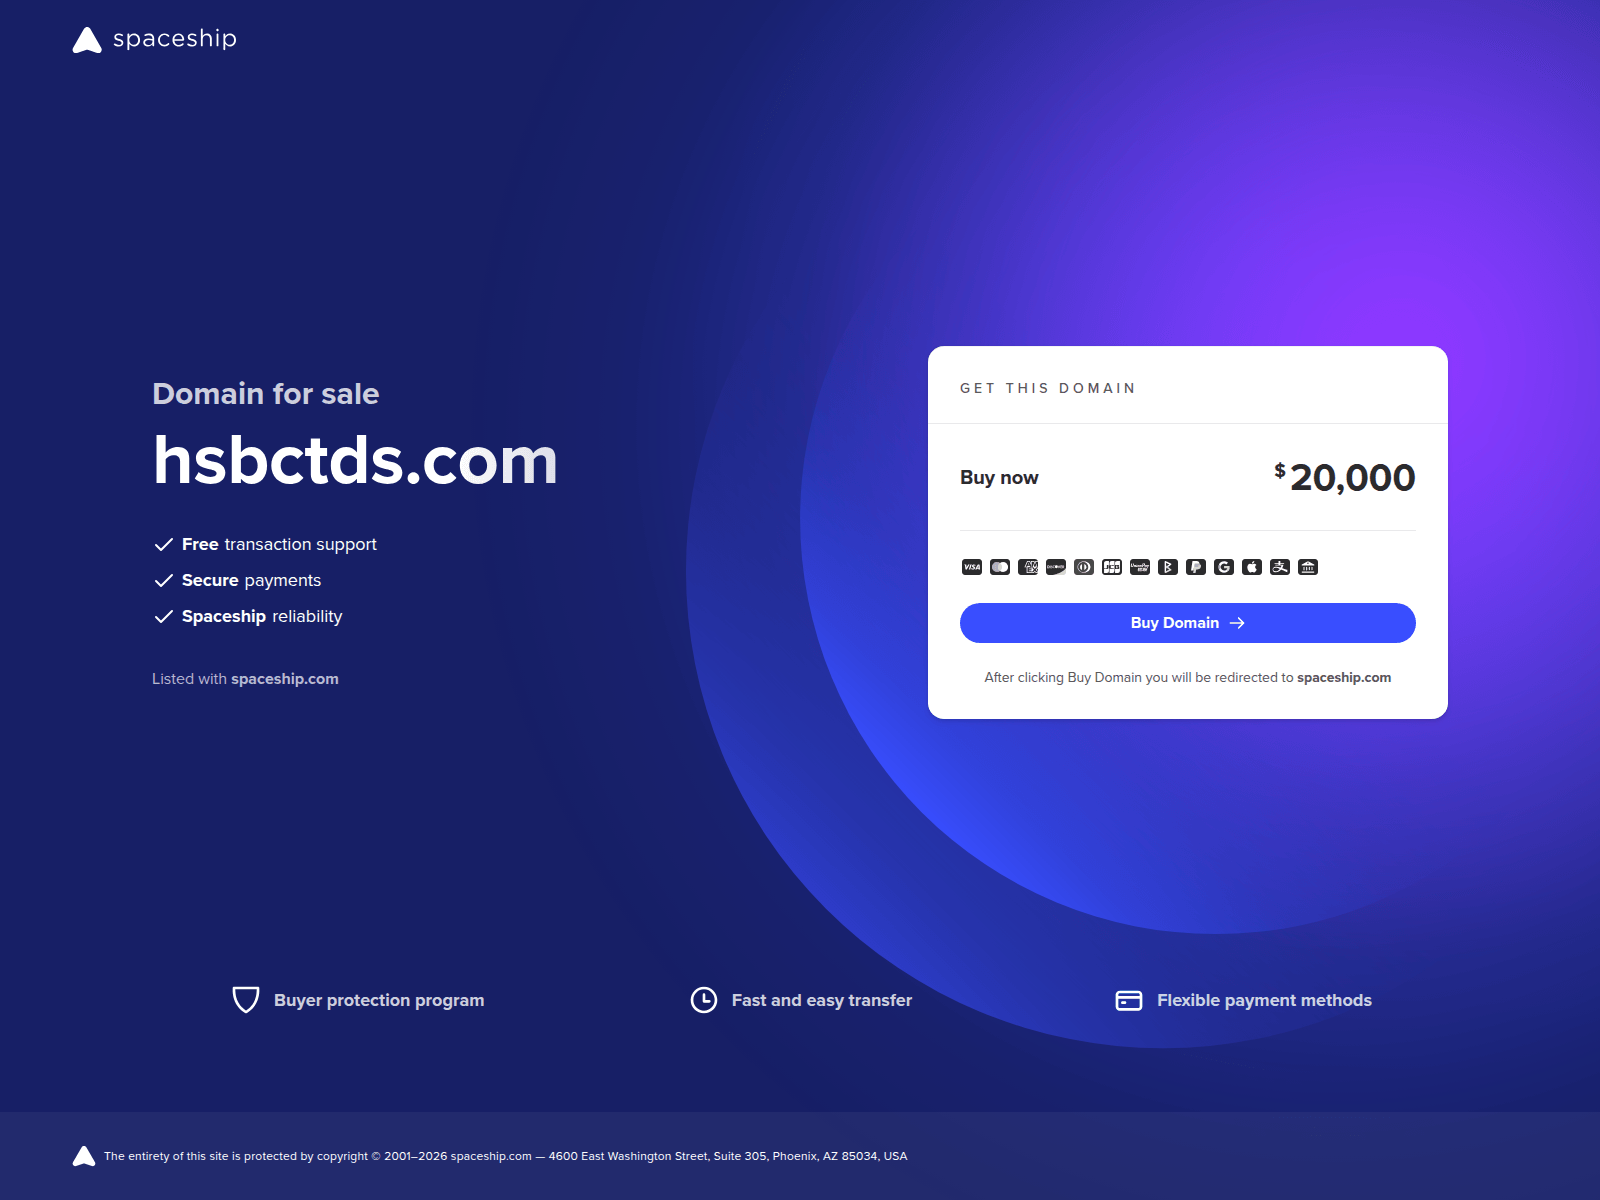
Last check (UTC) First seen (UTC) ▾ URL Screenshot Flags Details
2026-10-10 17:30 2026-09-16 17:25
https://hsbctds.com
Screenshot of hsbctds.com GSB Details
2026-10-10 17:30 2026-06-09 15:34
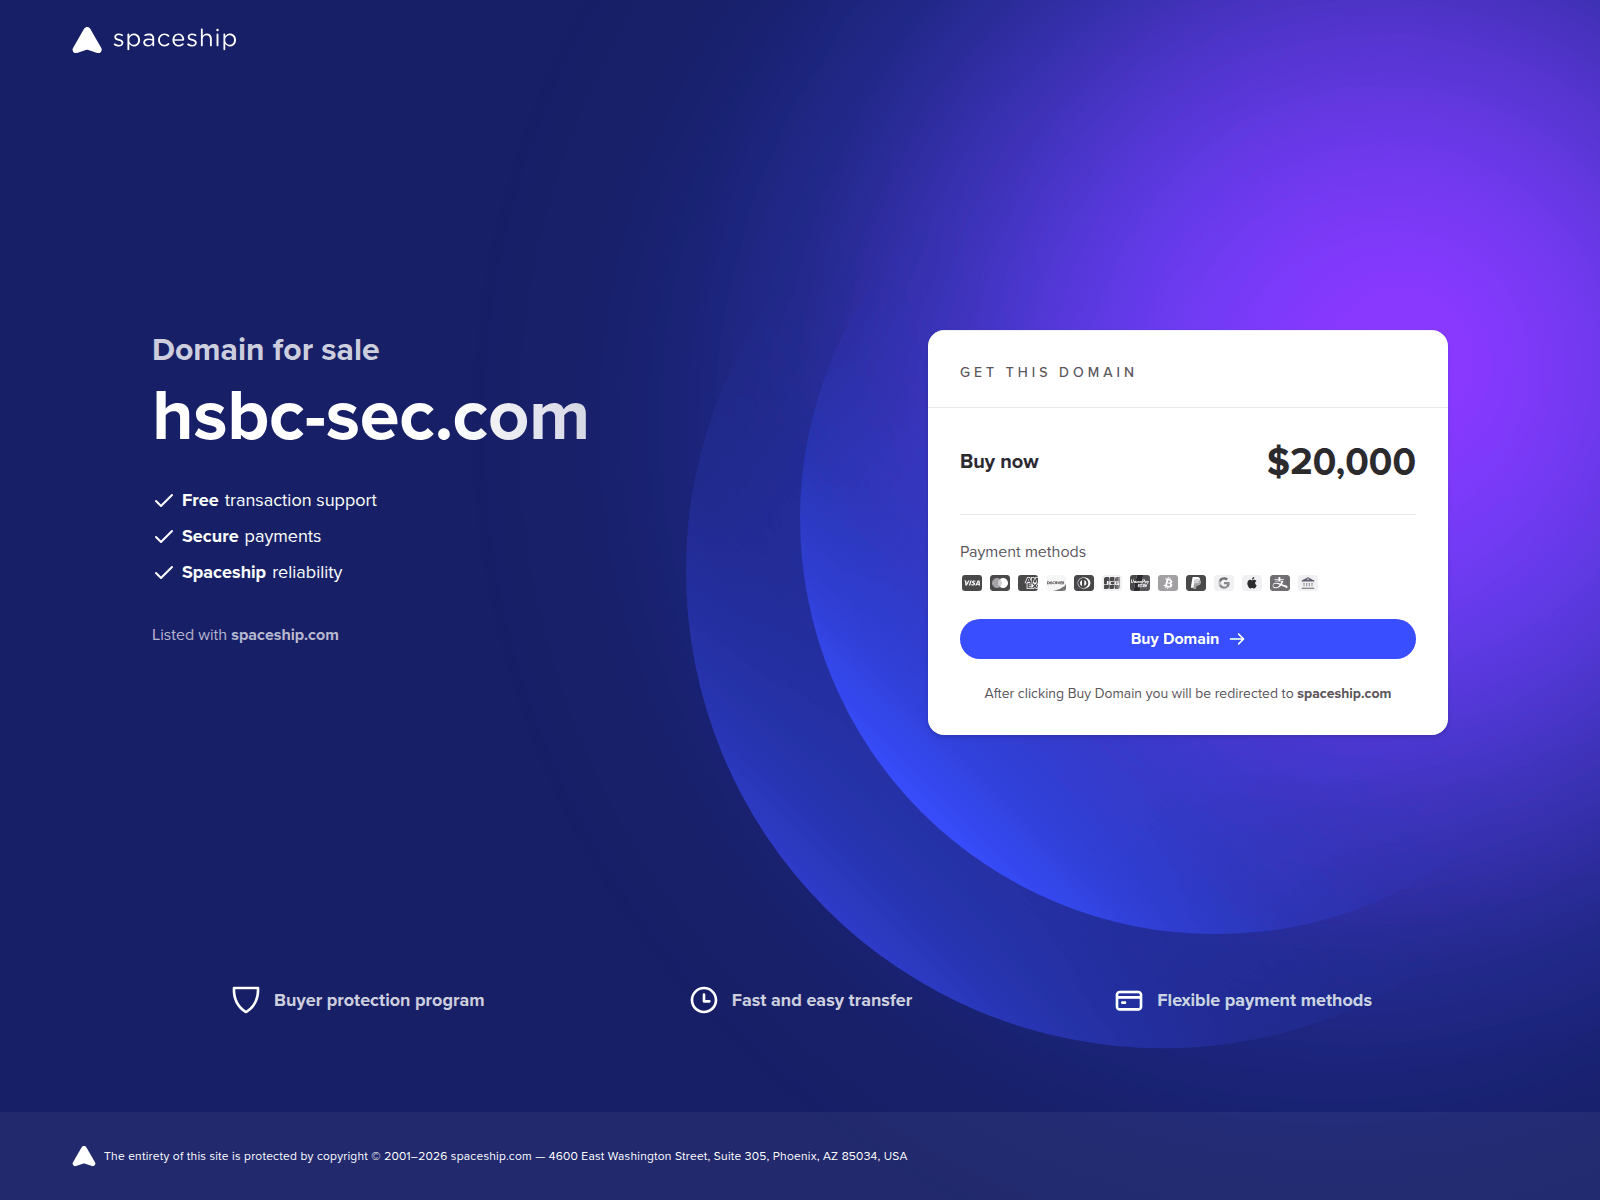
https://hsbc-sec.com
Screenshot of hsbc-sec.com urlscan Details
2026-10-10 17:30 2026-04-11 23:42
https://metamaskrewards.com
Screenshot of metamaskrewards.com urlscan Details

Info


Analyze IP

URLScan logo urlscan.io VirusTotal logo VirusTotal ipinfo logo ipinfo

Greynoise logo Greynoise

Suspicious sites — confidence is not always 100%. Use for Threat Hunting or watchlists.
URL Screenshot Flags Details
https://hsbctds.com Screenshot of hsbctds.com GSB Details
https://hsbc-sec.com Screenshot of hsbc-sec.com urlscan Details
https://metamaskrewards.com Screenshot of metamaskrewards.com urlscan Details
