R12
What is R12?
Free automated DV TLS via ACME. Rotated alongside its R1x siblings.
Suspicious sites — confidence is not always 100%. Use for Threat Hunting or watchlists.
| Last check (UTC) | First seen (UTC) ▾ | URL | Screenshot | Flags | Details |
|---|---|---|---|---|---|
| 2026-10-03 03:30 | 2026-06-17 01:06 |  |
OpenPhish | Details | |
| 2026-10-03 03:30 | 2026-06-14 13:01 |  |
OpenPhish | Details | |
| 2026-10-03 03:30 | 2026-06-13 13:01 | 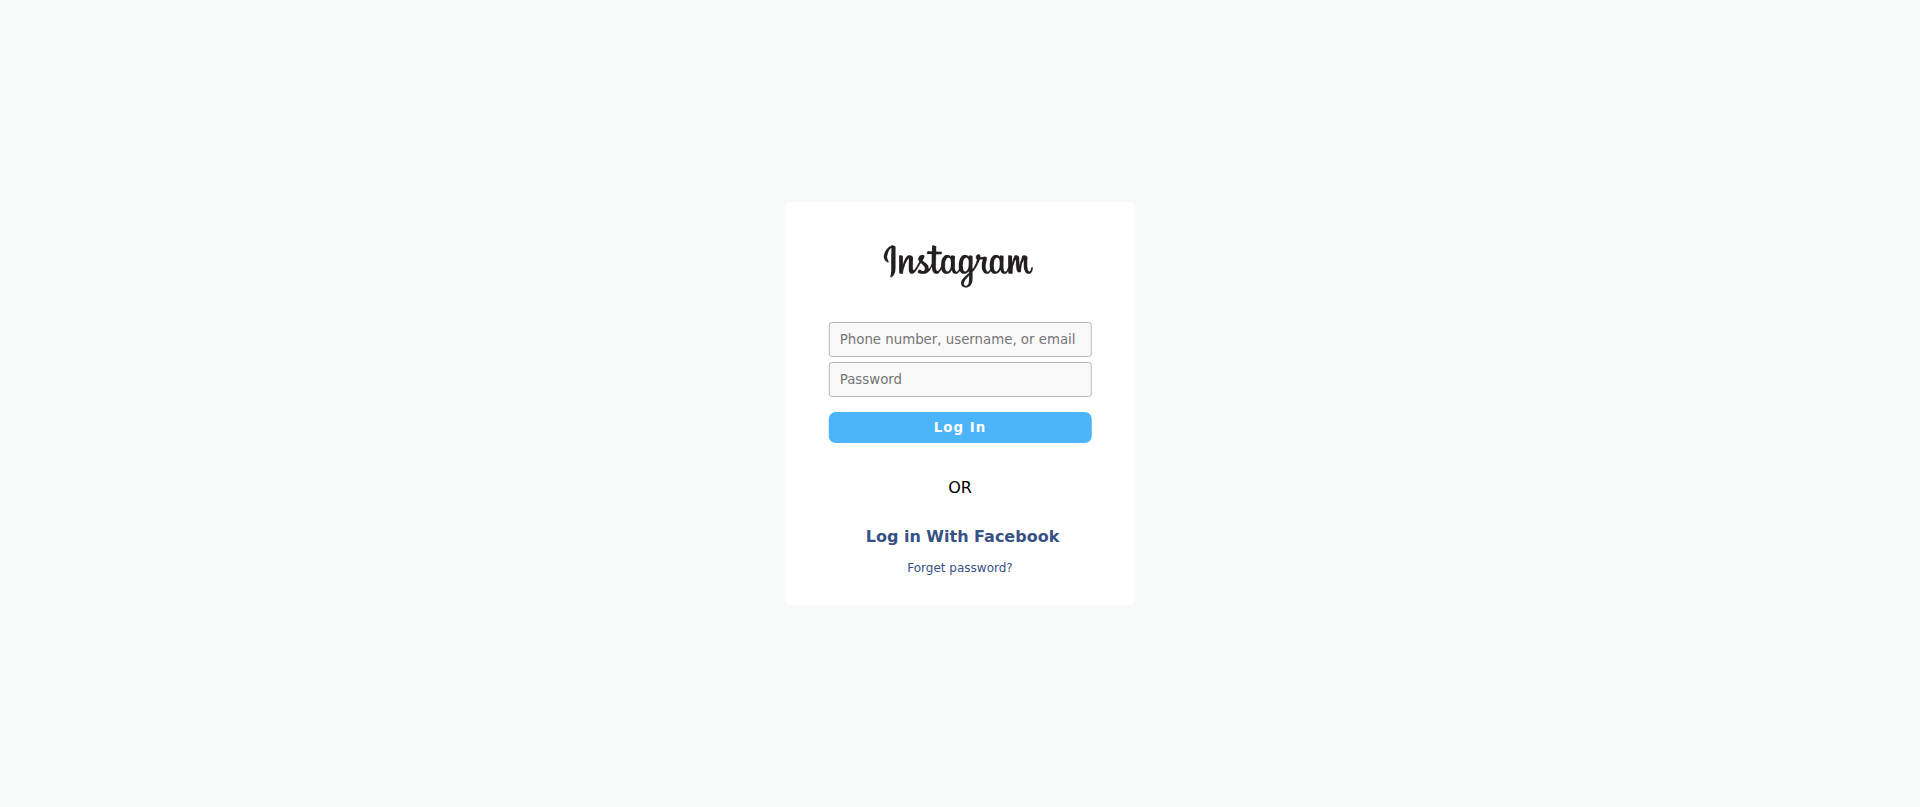 |
GSB OpenPhish urlscan | Details | |
| 2026-10-03 03:30 | 2026-06-05 01:00 | 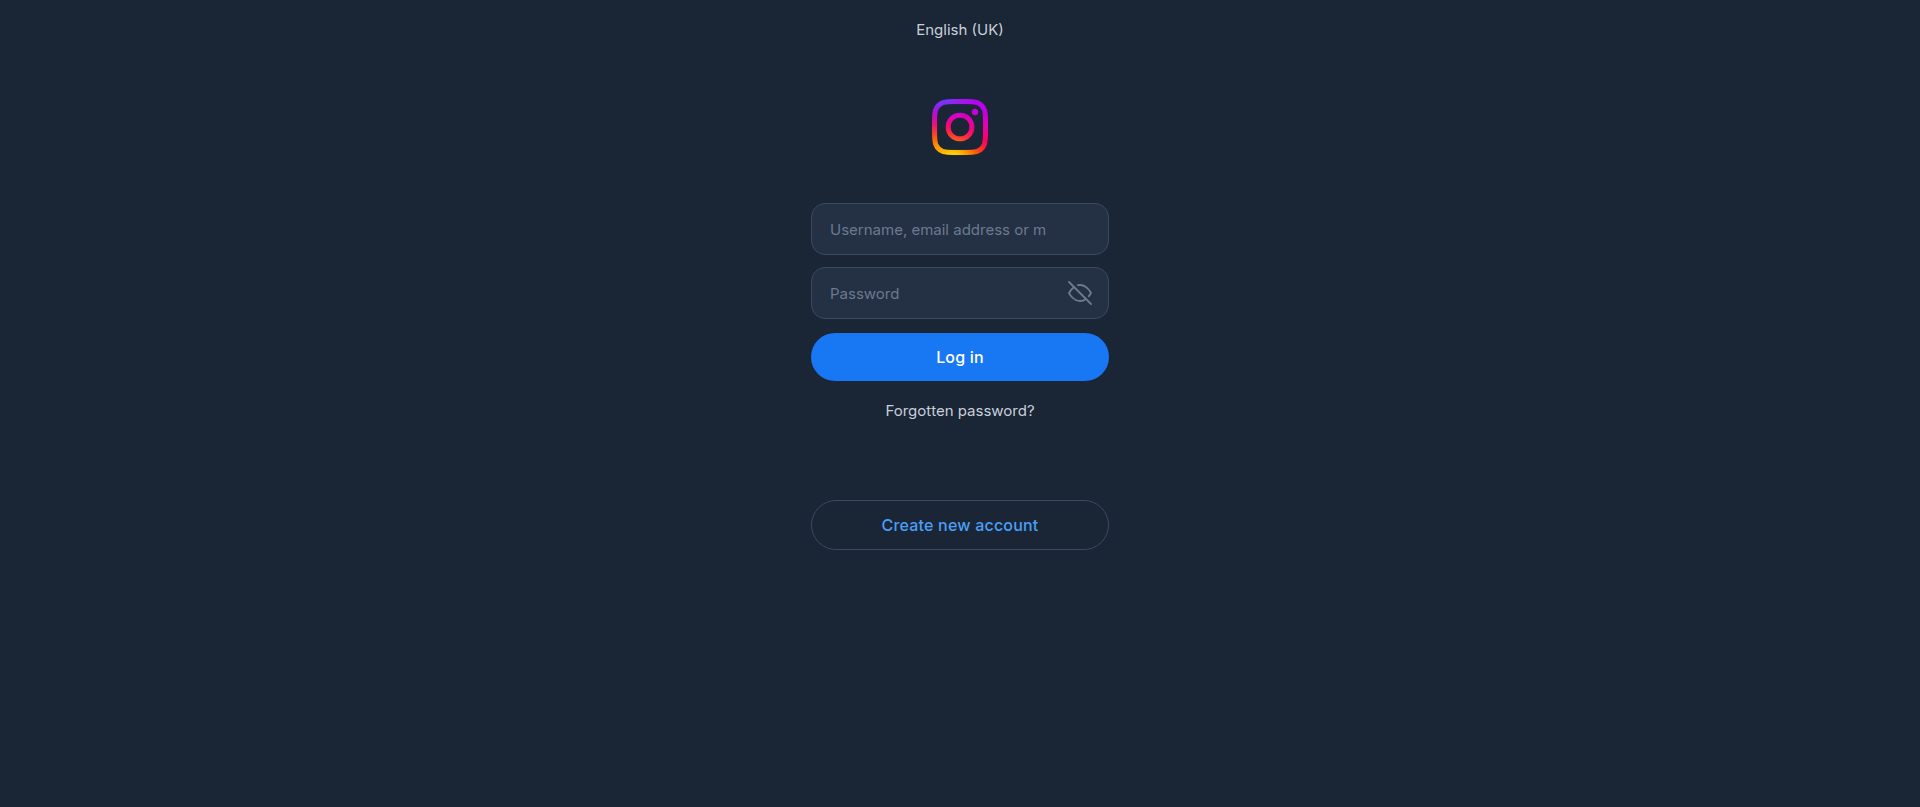 |
OpenPhish | Details | |
| 2026-10-03 03:30 | 2026-06-04 01:01 |  |
GSB OpenPhish urlscan | Details | |
| 2026-10-03 03:30 | 2026-04-15 01:01 |  |
OpenPhish | Details |
Suspicious sites — confidence is not always 100%. Use for Threat Hunting or watchlists.
| URL | Screenshot | Flags | Details |
|---|---|---|---|
| https://office365.rricrosoft-… | |
OpenPhish | Details |
| https://ruddycruzc.github.io/… | |
OpenPhish | Details |
| http://support-instagram.gith… | |
GSB OpenPhish urlscan | Details |
| https://instagramlogin-accoun… | |
OpenPhish | Details |
| https://instagram-cyber.githu… | |
GSB OpenPhish urlscan | Details |
| http://facebook-faq.se | |
OpenPhish | Details |
Brands most often impersonated with R12
Among the active sites currently using a R12 certificate, these are the brands attackers are mimicking most:
Frequently asked questions about R12
What is R12?
R12 is a publicly trusted intermediate certificate authority operated by Internet Security Research Group (ISRG) and chained to ISRG Root X1. It is recognized by all mainstream browsers and operating system trust stores, so the certificate itself is not a phishing indicator - the same intermediate signs millions of legitimate sites. phishunt only flags the specific domains listed below as suspicious; R12 as a CA is fine.
Is R12 a legitimate certificate authority?
Yes. R12 is a publicly trusted intermediate CA operated by Internet Security Research Group (ISRG), included in the Microsoft, Apple, Google and Mozilla root trust stores. Every mainstream browser automatically accepts certificates it signs. The intermediate itself is not a phishing signal — what matters is the specific domain. phishunt flags only the suspicious domains listed below; R12 keeps signing millions of legitimate sites.
Who runs the R12 certificate authority?
R12 is operated by Internet Security Research Group (ISRG). It is a RSA intermediate that chains up to the ISRG Root X1 root, which Internet Security Research Group (ISRG) also owns. Anyone can look up the chain in the public Certificate Transparency logs; the same operator publishes a Certificate Policy / Certification Practice Statement (CP/CPS) describing how issuance and revocation work.
What does R12 mean when my browser shows it as the issuer?
When a browser shows R12 as the certificate issuer for a site, it means TLS was validated through Internet Security Research Group (ISRG)'s RSA chain ending at ISRG Root X1. That is normal for tens of millions of legitimate sites that use Internet Security Research Group (ISRG)'s automated DV TLS. The certificate proves the connection is encrypted and that the certificate matches the hostname — it does not prove the site behind it is trustworthy. Always verify the domain name itself.
Why does R12 show up on phishing sites?
Internet Security Research Group (ISRG) issues RSA domain-validated certificates automatically and at no cost (or very low cost), which is the exact workflow scammers need to put HTTPS on a throwaway domain. Domain validation only proves that the requester controls the domain name, not that the site behind it is trustworthy. phishunt lists the specific domains currently flagged below — those are the suspicious ones, not R12 itself.
How do I verify a certificate issued by R12?
In a desktop browser, click the padlock in the address bar and open the certificate viewer. Confirm the issuer chain ends at ISRG Root X1, that the subject matches the domain you expect, and that the notAfter date has not passed. A valid R12 certificate only proves TLS was negotiated correctly — always verify the domain name itself belongs to the service you intended to visit.
What is the difference between R12 and R10?
R12 and its siblings (R10, R11, R13, R14) share the same operator (Internet Security Research Group (ISRG)) and roll up to the same root (ISRG Root X1). CAs rotate multiple intermediates so that if one key ever has to be revoked, the damage is contained. As a user, you can treat all of them as the same trust anchor.