Suspicious
Phishings targeting AT&T
Suspicious and active websites
Phishings targeting Att
Suspicious and active websites
Active
1
New (7d)
1
Trend (7d)
—
- Countries
 United States
Suspicious sites — confidence is not always 100%. Use for Threat Hunting or watchlists.
| Last check (UTC) | First seen (UTC) ▾ | URL | Screenshot | Flags | Details |
|---|---|---|---|---|---|
| 2026-11-15 23:30 | 2026-11-12 13:03 | 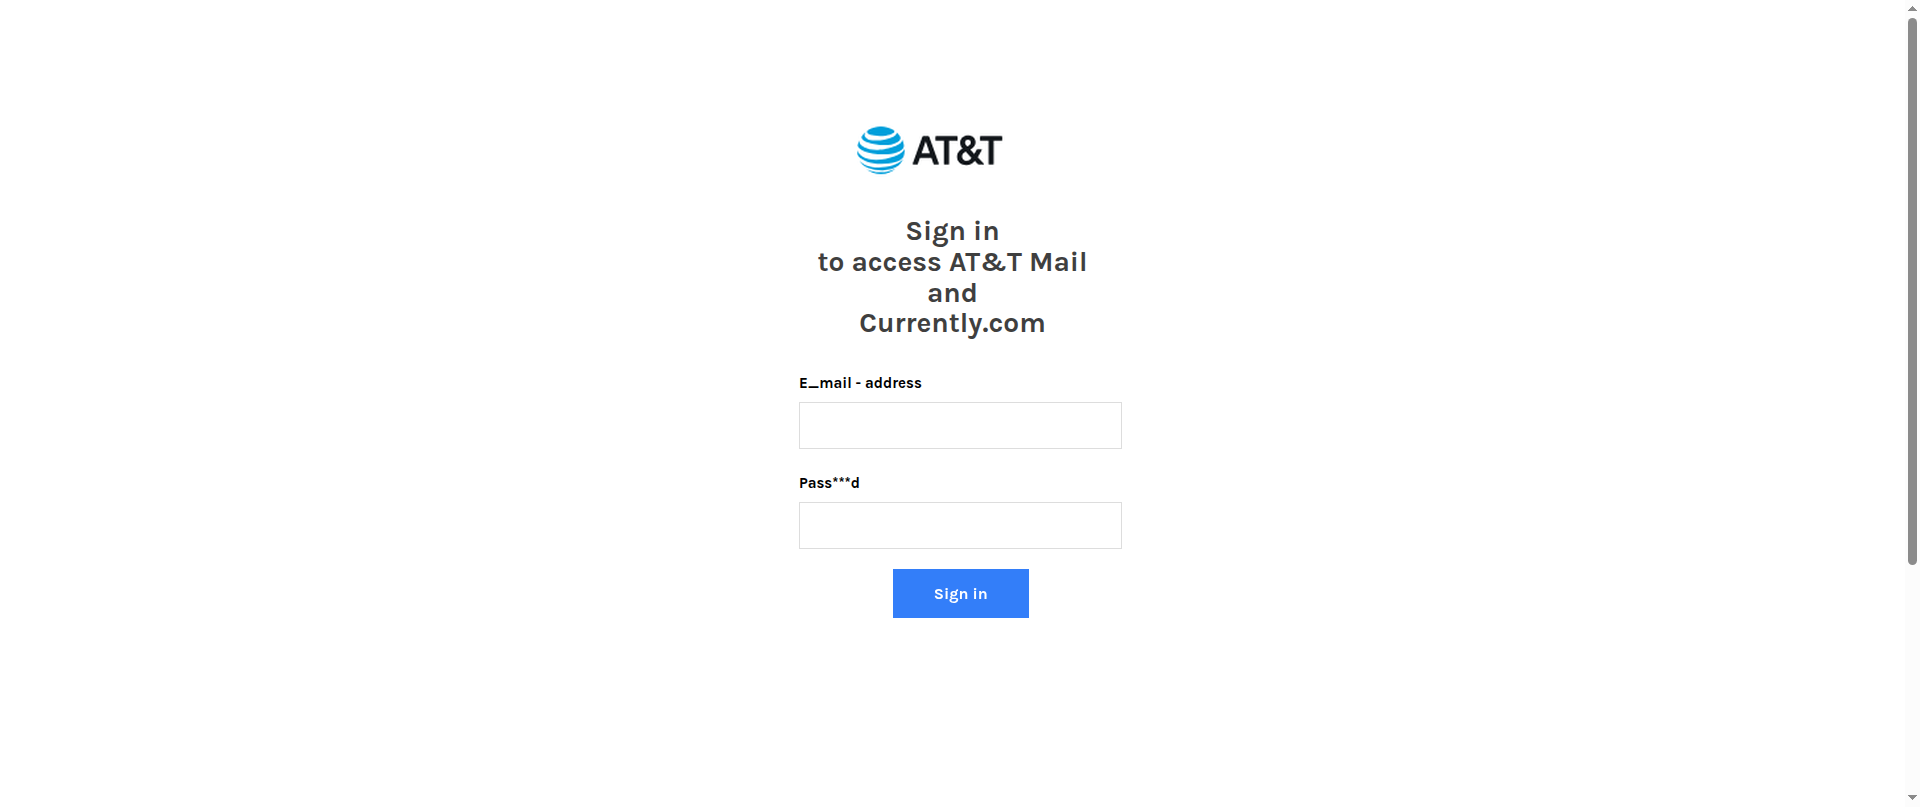 |
OpenPhish | Details |
Suspicious sites — confidence is not always 100%. Use for Threat Hunting or watchlists.
| URL | Screenshot | Details |
|---|---|---|
| https://attmail8566575.weebly…
OpenPhish |
|
Details |
AIHow to verify a real AT&T URL
- Legitimate AT&T URLs always end in
att.com(e.g.www.att.com,account.att.com). Anything else — including look-alike typosquats, hyphenated variations, or unfamiliar TLDs like.xyz/.top/.vip— is not AT&T. - The padlock icon proves TLS is active, not that the site is safe. Free DV certificates are issued to attackers in minutes; every active site listed above has a valid TLS certificate.
- If you got the link from email, SMS, or social media, do not click it. Open
att.comfrom your browser bookmark or type the domain manually. - Real AT&T pages almost never ask for credentials immediately after clicking from a message — treat any such redirect as a phishing attempt until the domain is verified.