Phishing detection: facebook.thietkewebdep.net
Facebook Screenshot
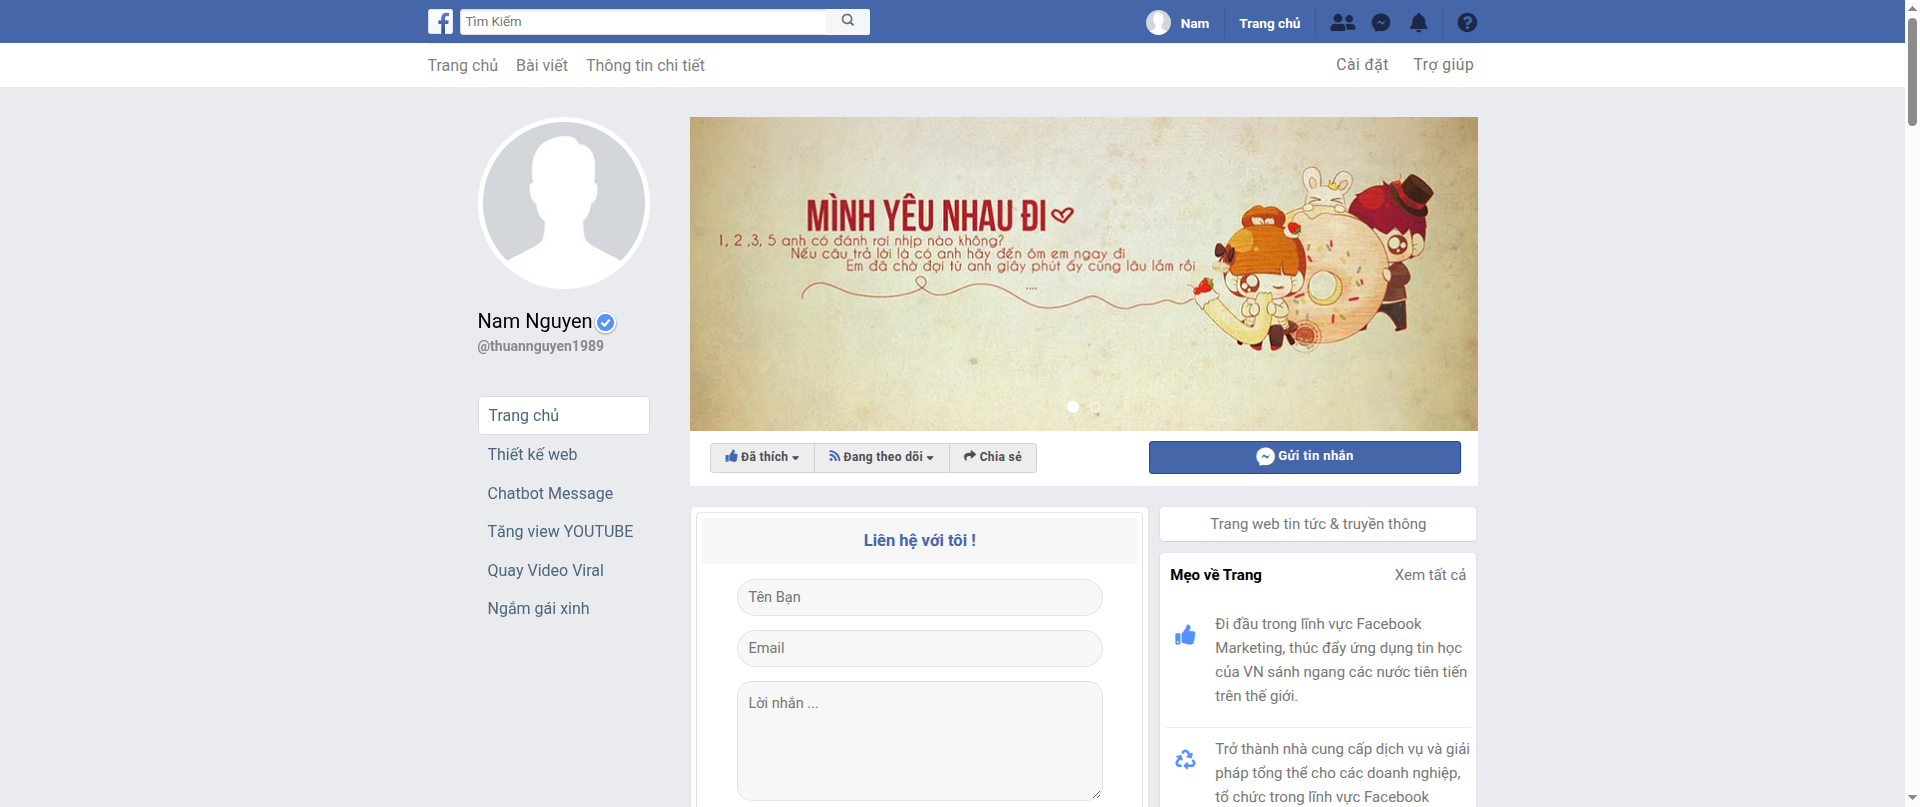
Investigate
Domain
facebook.thietkewebdep.net43 CT hosts on apex
 urlscan
 VirusTotal
 Whois
IP
103.116.107.228
 ipinfo
 Greynoise
URL
https://facebook.thietkewebdep.net
Phishunt analysis Beta
30
low suspicionheuristic risk score · not a probability
Why?
- +5.3 Keyword match
- +4.5 Brand in title
- +4.1 Brand in screenshot
- +3.0 OpenPhish
- +3.0 PhishTank
- +2.6 Brand in subdomain
- +2.2 Country mismatch
- +1.1 ASN reputation
- +1.1 No CSP header
- +1.1 No HSTS header
- +0.7 Unrecognised DNS provider
- +0.6 Registrar reputation
- +0.5 Long domain
- +0.2 Suspicious TLD
- +0.1 External scripts
- +0.1 Deep subdomain
19 signals fired · detector v3.0.0
AI analysis AIBeta
Credential harvesting
Impersonates Facebook using the brand as a subdomain hosted on a Vietnamese server. Contains a same-origin login form and reuses known phishing resources, consistent with a credential harvesting page. Confirmed malicious by OpenPhish.
OpenPhishSame-origin formBrand in subdomain
AI-generated from stored detector signals - the AI never visited the site. · 2026-09-22 · confidence 90%
Domain & Network
Whois
Network
Country
 Vietnam
Hosting
Reload Company Limited
ASN
AS135987
TLS Cert
-
Requests
Resources
Observables
Related websites
Report this phishing
Submit to blocklists