Phishing detection: notifications.microsoft-ssl.com
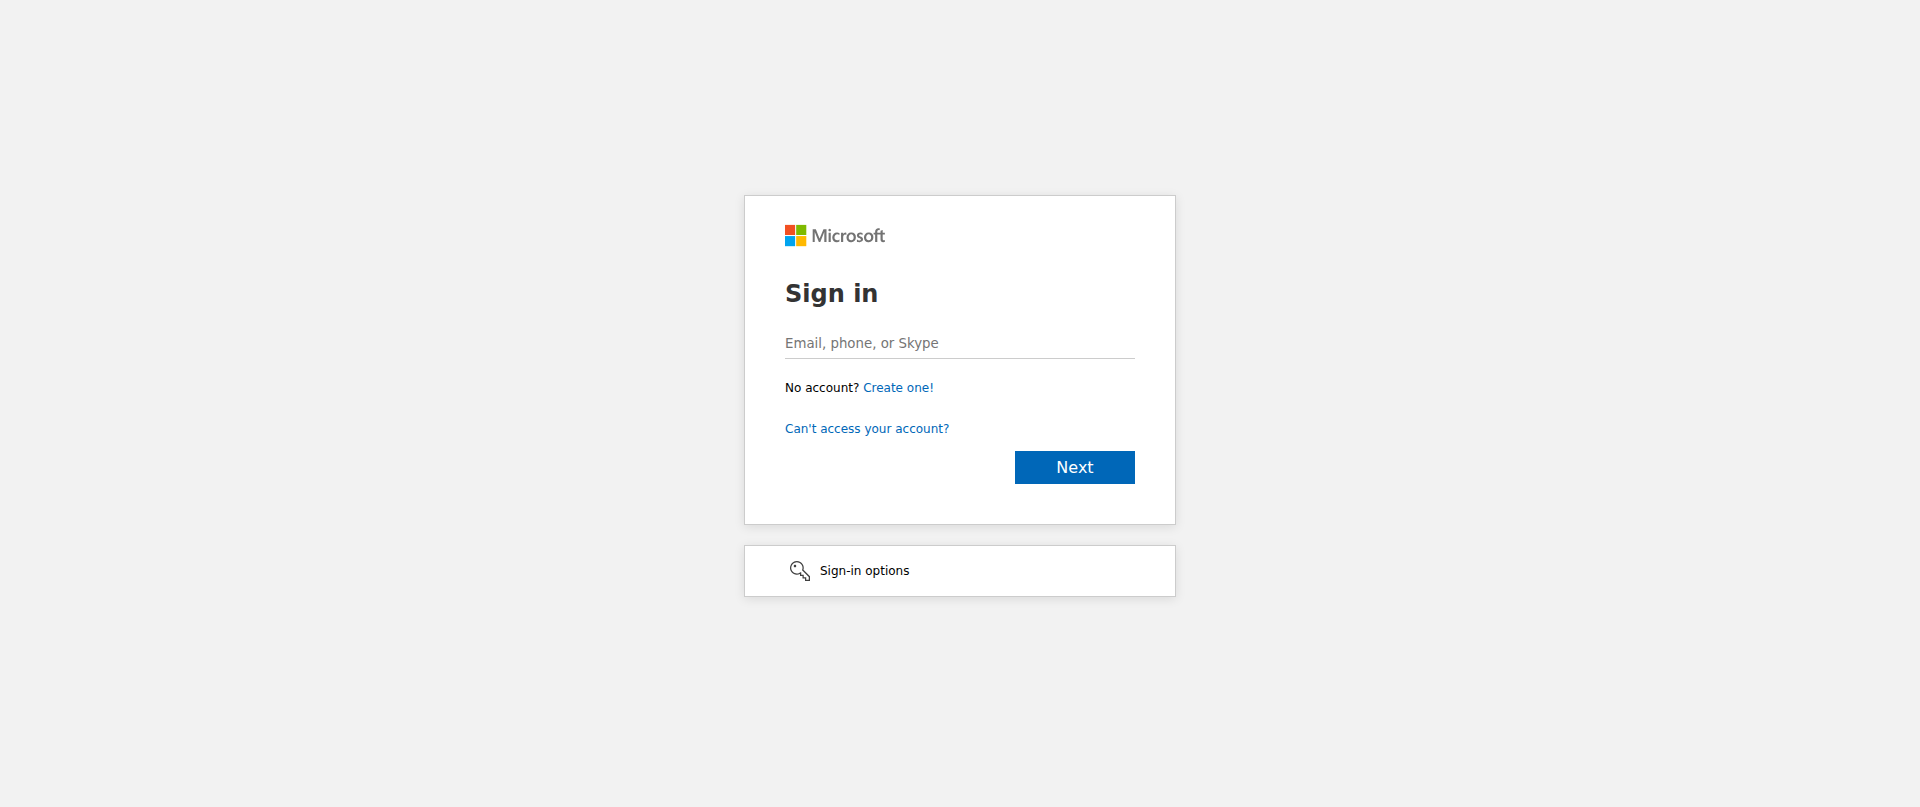
Microsoft Screenshot
Investigate
Domain
notifications.microsoft-ssl.com1 CT host on apex
 urlscan
 VirusTotal
 Whois
IP
52.36.210.209
 ipinfo
 Greynoise
URL
https://notifications.microsoft-ssl.com
Phishunt analysis Beta
70
high suspicion likely_phishingheuristic risk score · not a probability
Why?
- +5.3 Keyword match
- +5.1 Site cluster
- +4.1 Brand in screenshot
- +3.9 Password field
- +3.7 Brand in domain label
- +3.0 OpenPhish
- +1.9 ASN reputation
- +1.1 No CSP header
- +1.1 No HSTS header
- +0.7 Brand in cert SAN
- +0.7 Brand typo
- +0.6 Long domain
- +0.6 Login text in screenshot
- +0.2 Suspicious TLD
- +0.1 Hyphens
- +0.1 Deep subdomain
- Boosted to 70: Credential + brand lookalike
19 signals fired · detector v3.0.0
AI analysis AIBeta
Credential harvesting
Site impersonates Microsoft notification services using a lookalike domain hosted on Amazon AWS infrastructure. It presents a password input form for credential theft and has been confirmed malicious by OpenPhish.
OpenPhishPassword fieldBrand in domain label
AI-generated from stored detector signals - the AI never visited the site. · 2026-09-04 · confidence 80%
Domain & Network
Whois
Registrar
CSC Corporate Domains, Inc.
Network
IP
52.36.210.209 AWS EC2
Country
 United States
Hosting
Amazon.com, Inc.
ASN
AS16509
TLS Cert
Amazon RSA 2048 M04
External detection
OpenPhish
CleanGoogle Safe Browsing · PhishTank · TweetFeed · urlscan.io
Requests
Resources
Observables
Related websites
Report this phishing
 Network / ASN
Amazon.com, Inc.
 Brand owner
Microsoft
Submit to blocklists