Phishing detection: usc1.contabostorage.com
Microsoft Screenshot
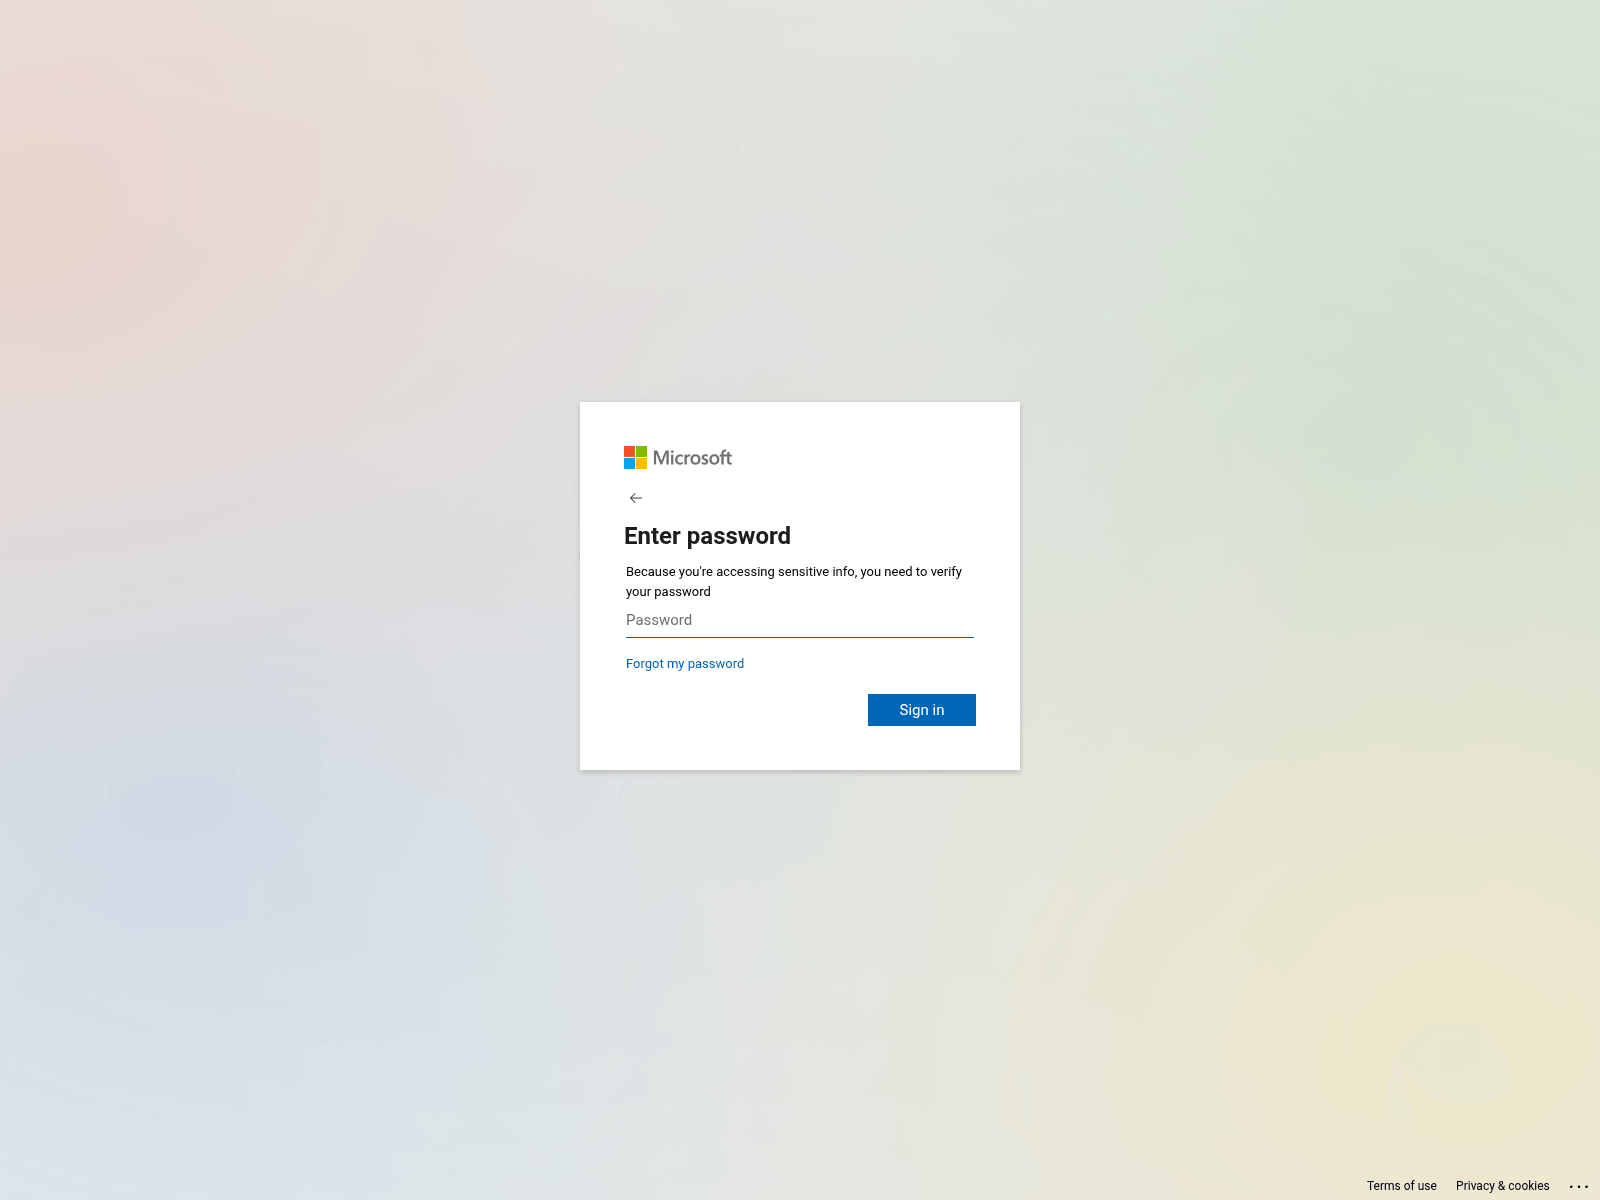
Screenshot captured by urlscan.io on 2026-09-20T01:15 UTC: our own render of this page came back blank.
Investigate
Domain
usc1.contabostorage.com1 CT host on apex
 urlscan
 VirusTotal
 Whois
IP
209.126.15.84
 ipinfo
 Greynoise
URL
https://usc1.contabostorage.com/3afb0c8c107a4058aec51787070…
Phishunt analysis Beta
75
high suspicion likely_phishingheuristic risk score · not a probability
Why?
- +5.3 Keyword match
- +4.5 Brand in title
- +4.1 Brand in screenshot
- +3.9 Password field
- +3.0 OpenPhish
- +1.1 ASN reputation
- +1.1 No CSP header
- +0.6 Brand impersonation in path
- +0.6 Login text in screenshot
- +0.6 Registrar reputation
- +0.6 Script exfil endpoint
- +0.5 Young certificate
- +0.5 Long domain
- +0.2 Suspicious TLD
- +0.1 External scripts
- +0.1 Deep subdomain
- Boosted to 75: Credential exfil kit
21 signals fired · detector v3.0.0
AI analysis AIBeta
Credential harvesting
Microsoft Hotmail phishing page served as a static file from Contabo object storage, abusing cloud infrastructure to evade detection. Contains a live password field and a script-based credential exfiltration endpoint. Confirmed malicious by OpenPhish.
Password fieldScript exfil endpointOpenPhish
AI-generated from stored detector signals - the AI never visited the site. · 2026-09-20 · confidence 92%
Domain & Network
Whois
Registrar
RegistryGate GmbH
Network
Country
 United States
Hosting
Contabo Inc.
ASN
AS40021
TLS Cert
ZeroSSL RSA DV SSL CA 2
External detection
OpenPhish
CleanGoogle Safe Browsing · PhishTank · TweetFeed · urlscan.io
Requests
Resources
Observables
Related websites
Report this phishing
 Brand owner
Microsoft
Submit to blocklists