Phishing detection: santanderbizum.com
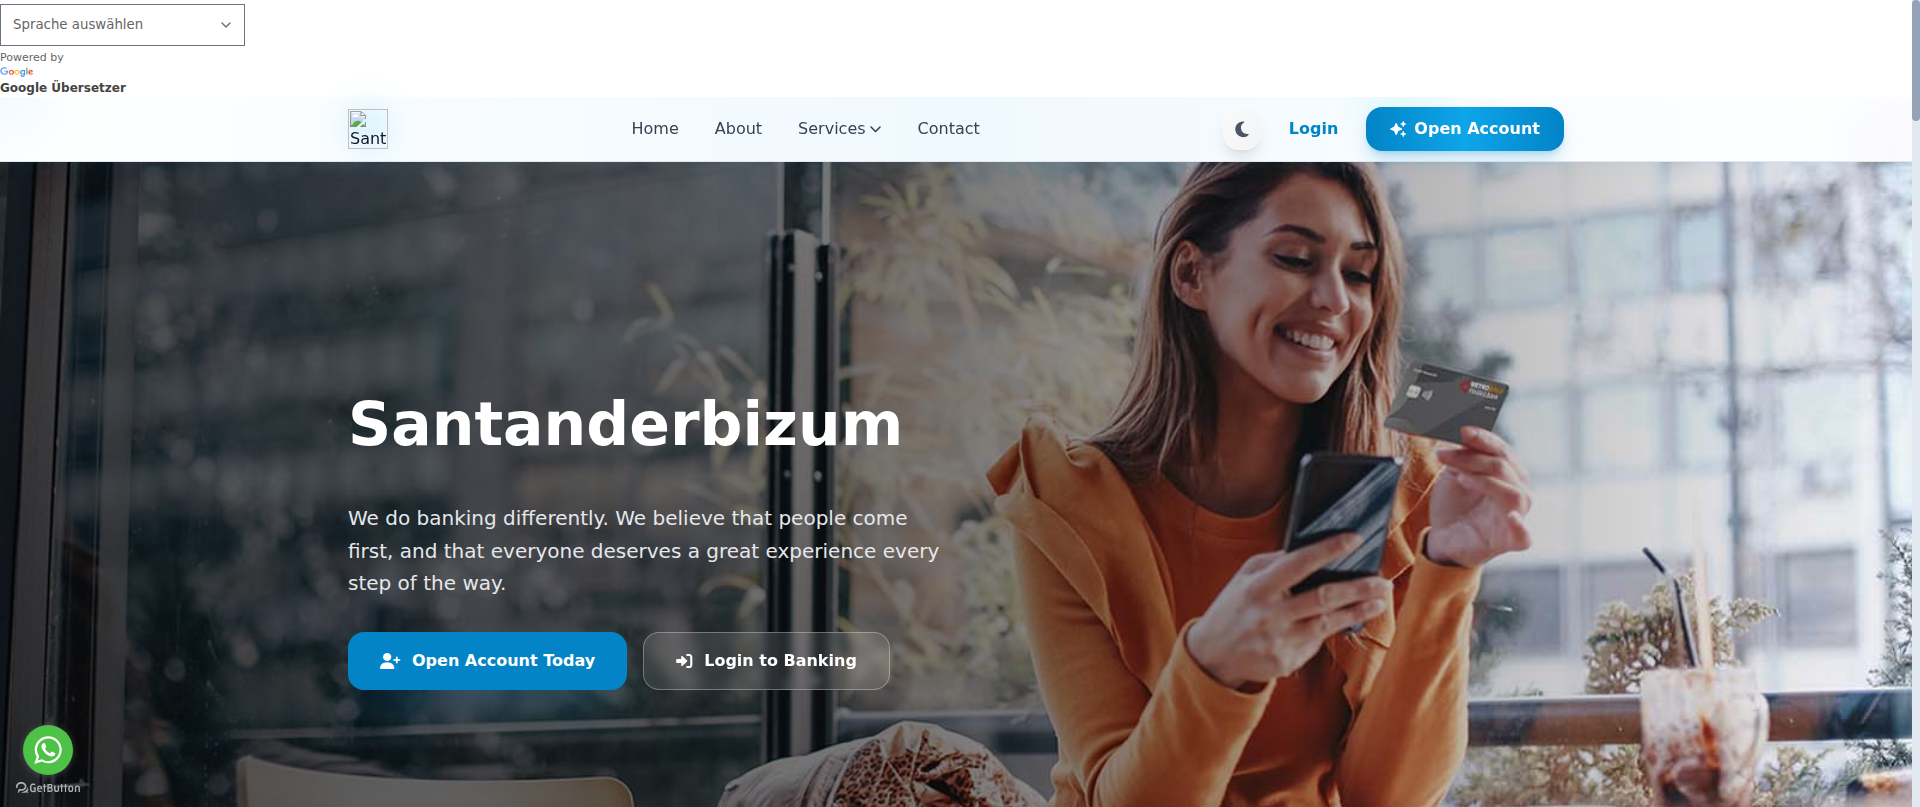
Banco Santander Screenshot
Investigate
Domain
santanderbizum.com1 CT host on apex
 urlscan
 VirusTotal
 Whois
IP
163.61.188.7
 ipinfo
 Greynoise
URL
https://santanderbizum.com
Phishunt analysis Beta
33
medium suspicion suspiciousheuristic risk score · not a probability
Why?
- +5.3 Keyword match
- +5.1 urlscan.io
- +4.5 Brand in title
- +4.1 Brand in screenshot
- +3.7 Brand in domain label
- +2.2 Country mismatch
- +1.1 ASN reputation
- +1.1 No CSP header
- +1.1 No HSTS header
- +0.8 Young domain
- +0.7 Brand in cert SAN
- +0.7 Unrecognised DNS provider
- +0.6 Login text in screenshot
- +0.6 Registrar reputation
- +0.5 Young certificate
- +0.4 Long domain
- +0.3 Free CA
- +0.2 Suspicious TLD
- +0.1 External scripts
22 signals fired · detector v3.0.0
AI analysis AIBeta
Credential harvesting
Site impersonates Santander Bank targeting Bizum users, the Spanish mobile payment platform, with login pages designed to harvest banking credentials. The domain apex and TLS certificate both reference the Santander brand. Confirmed malicious by urlscan, hosted in the US by NEW DHAKA HARDWARE.
Brand in domain labelBrand in cert SANLogin text in screenshot
AI-generated from stored detector signals - the AI never visited the site. · 2026-09-12 · confidence 88%
Domain & Network
Whois
Registrar
Atak Domain Bilgi Teknolojileri A.S.
Network
IP
163.61.188.7
Country
 United States
Hosting
NEW DHAKA HARDWARE
ASN
AS153568
TLS Cert
Let's Encrypt
External detection
urlscan.io
CleanGoogle Safe Browsing · OpenPhish · PhishTank · TweetFeed
Requests
Resources
Observables
Related websites
Report this phishing
Submit to blocklists