Phishing detection: whatsapp.tamil.bid
WhatsApp Screenshot
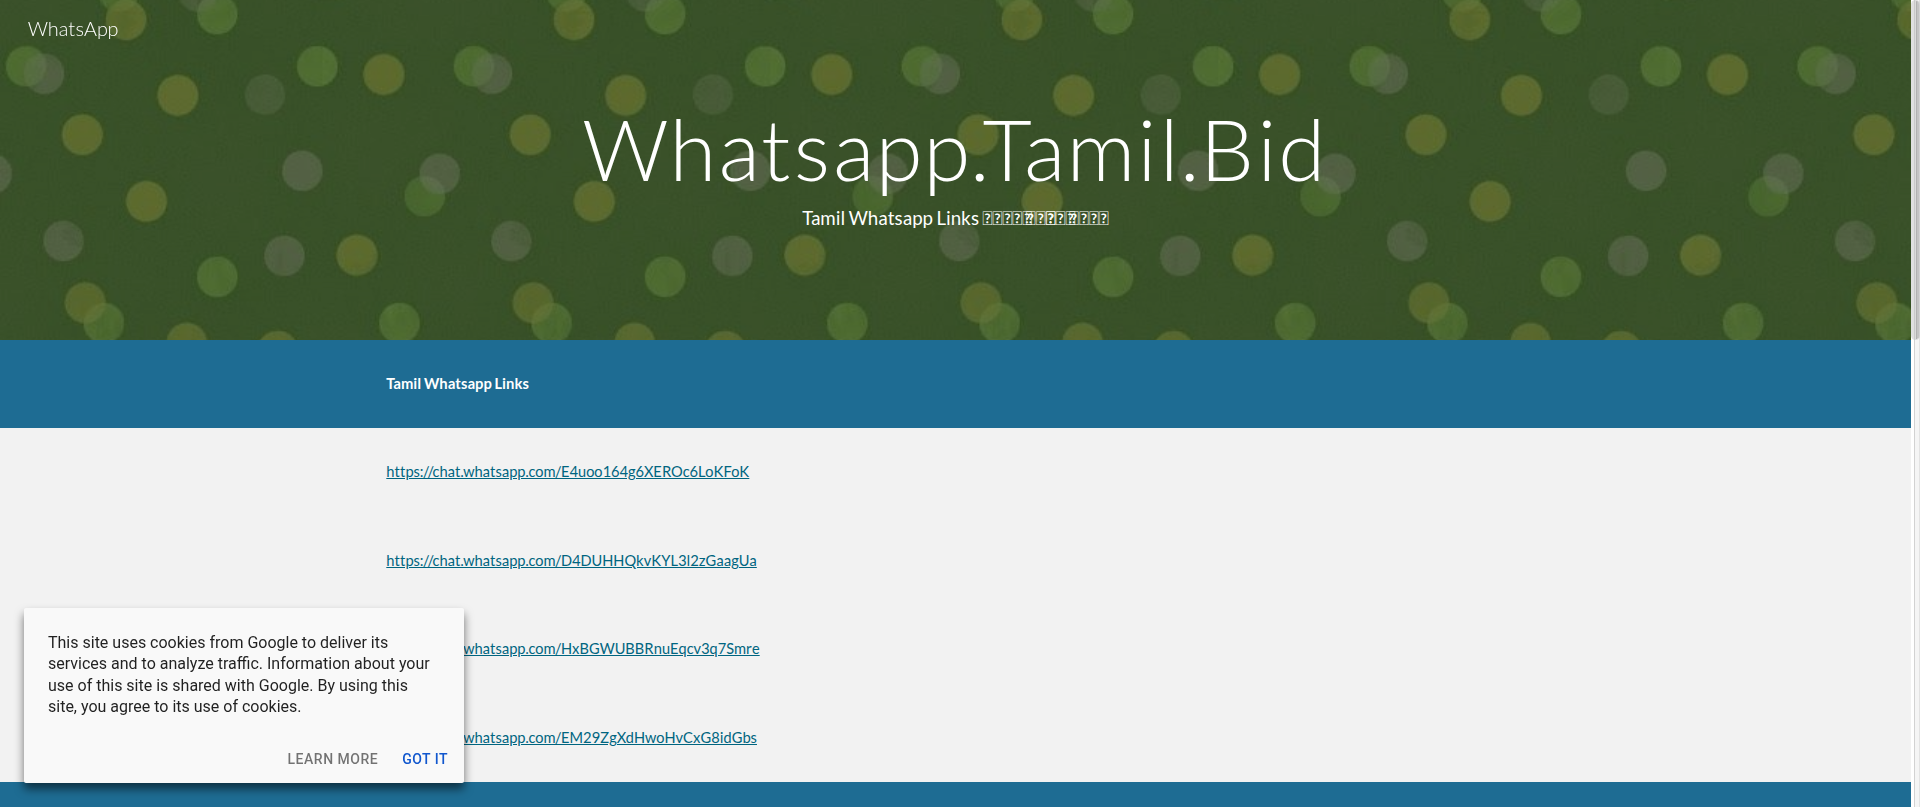
Investigate
Domain
whatsapp.tamil.bid31 CT hosts on apex
 urlscan
 VirusTotal
 Whois
IP
74.125.29.121
 ipinfo
 Greynoise
URL
https://whatsapp.tamil.bid
Phishunt analysis Beta
31
medium suspicion suspiciousheuristic risk score · not a probability
Why?
- +5.3 Keyword match
- +5.1 Site cluster
- +4.5 Brand in title
- +4.1 Brand in screenshot
- +3.0 OpenPhish
- +2.6 Brand in subdomain
- +1.2 ASN reputation
- +1.1 No HSTS header
- +0.7 Brand in cert SAN
- +0.7 Unrecognised DNS provider
- +0.6 Registrar reputation
- +0.6 Suspicious TLD
- +0.5 Young certificate
- +0.4 Long domain
- +0.3 Free CA
- +0.1 External scripts
- +0.1 Deep subdomain
19 signals fired · detector v3.0.0
AI analysis AIBeta
Credential harvesting
Impersonates WhatsApp with the brand placed as a subdomain of an abused .bid domain, with WhatsApp in the page title. Likely used to harvest WhatsApp account details. Uses a free-CA certificate, is on Google-hosted infrastructure, and is flagged by OpenPhish.
Brand in subdomainOpenPhishSuspicious TLD
AI-generated from stored detector signals - the AI never visited the site. · 2026-10-03 · confidence 75%
Domain & Network
Whois
Registrar
Dominet (HK) Limited
Network
IP
74.125.29.121 Google _spf.google.com
Country
 Switzerland
Hosting
Google LLC
ASN
AS15169
TLS Cert
WR3
External detection
OpenPhish
CleanGoogle Safe Browsing · PhishTank · TweetFeed · urlscan.io
Requests
Resources
Observables
Related websites
Report this phishing
Submit to blocklists