Phishing detection: lapaca.webdirecto.com
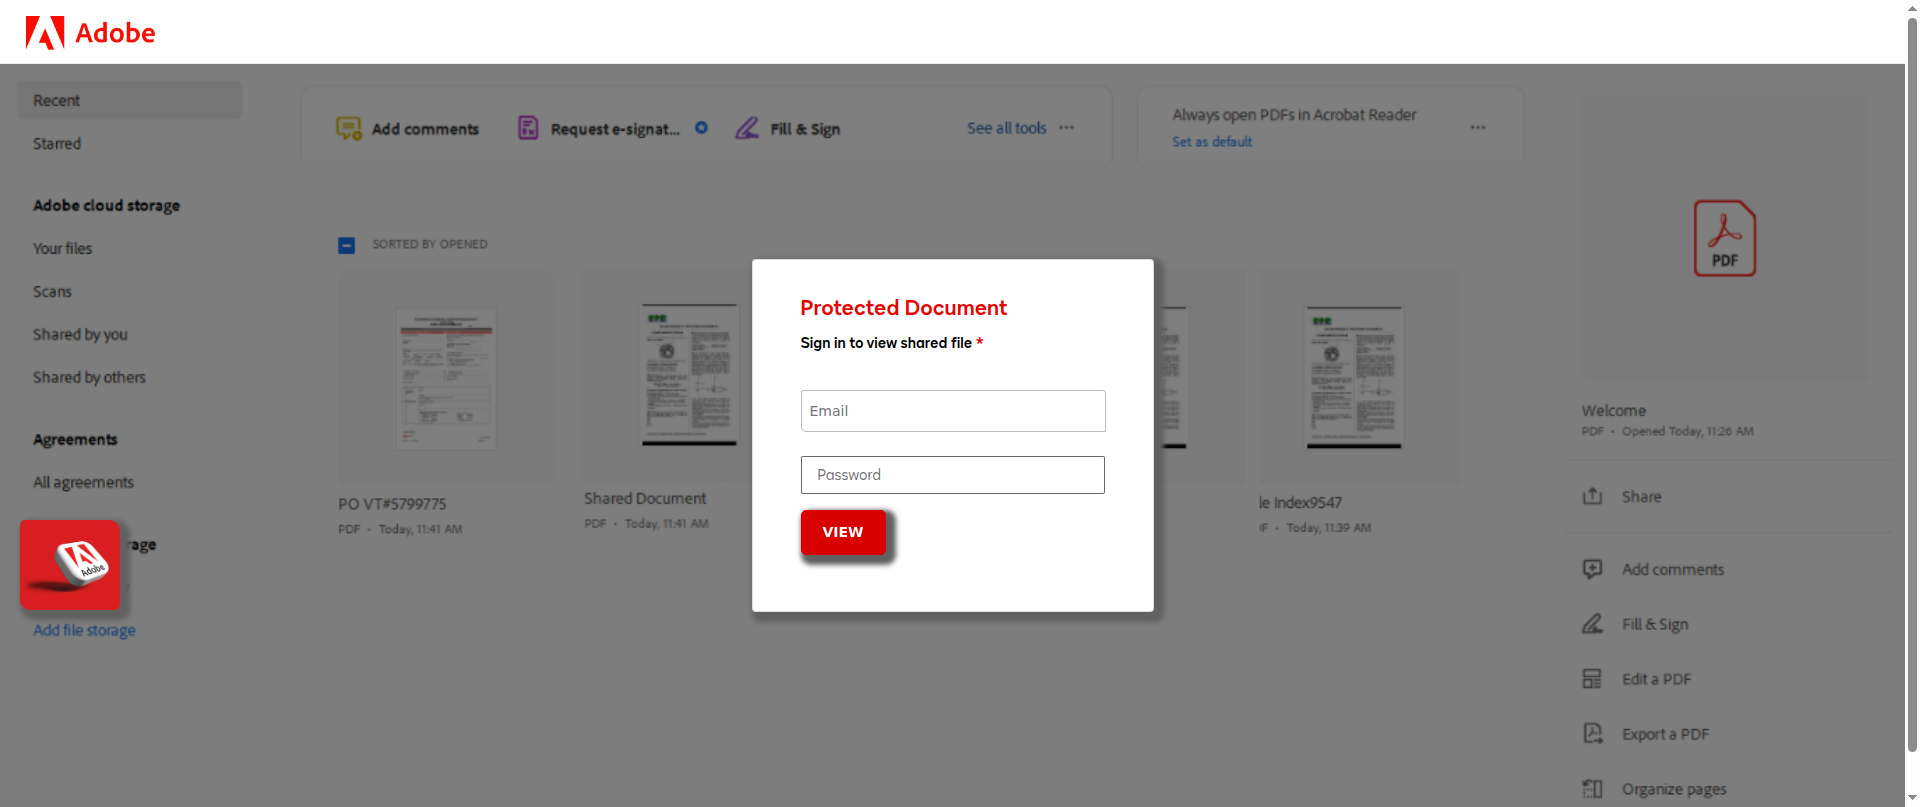
Adobe Screenshot
Investigate
Domain
lapaca.webdirecto.com11 CT hosts on apex
 urlscan
 VirusTotal
 Whois
IP
79.112.153.148
 ipinfo
 Greynoise
URL
https://lapaca.webdirecto.com/wp-includes/Text/tdweain/yogs…
Phishunt analysis Beta
27
low suspicionheuristic risk score · not a probability
Why?
- +5.3 Keyword match
- +4.5 Brand in title
- +3.0 OpenPhish
- +3.0 PhishTank
- +3.0 TweetFeed
- +2.2 Country mismatch
- +1.1 ASN reputation
- +1.1 No CSP header
- +1.1 No HSTS header
- +0.6 Brand impersonation in path
- +0.6 Login text in screenshot
- +0.5 Young certificate
- +0.4 Long domain
- +0.3 Free CA
- +0.2 Suspicious TLD
- +0.1 Deep subdomain
20 signals fired · detector v3.0.0
AI analysis AIBeta
Credential harvesting
Page hosted under a compromised WordPress includes directory on an unrelated domain impersonates Adobe through an adobe.html lure, likely harvesting Adobe account credentials. Listed in OpenPhish; the host resolves to a Spanish residential telecom ISP.
Brand impersonation in pathOpenPhishBrand in title
AI-generated from stored detector signals - the AI never visited the site. · 2026-11-14 · confidence 80%
Domain & Network
Whois
Registrar
OVH sas
Network
Country
 Spain
Spain
Hosting
DIGI SPAIN TELECOM S.A
ASN
AS57269
TLS Cert
YR2
Requests
Resources
Observables
Related websites
Report this phishing
Submit to blocklists