Suspicious
Phishings targeting Adobe
Suspicious and active websites
Phishings targeting Adobe
Suspicious and active websites
Active
9
New (7d)
5
Trend (7d)
↑67%
- Countries
 United States
 United Kingdom
 Germany
Suspicious sites — confidence is not always 100%. Use for Threat Hunting or watchlists.
| Last check (UTC) | First seen (UTC) ▾ | URL | Screenshot | Flags | Details |
|---|---|---|---|---|---|
| 2026-10-12 11:30 | 2026-10-11 13:04 | 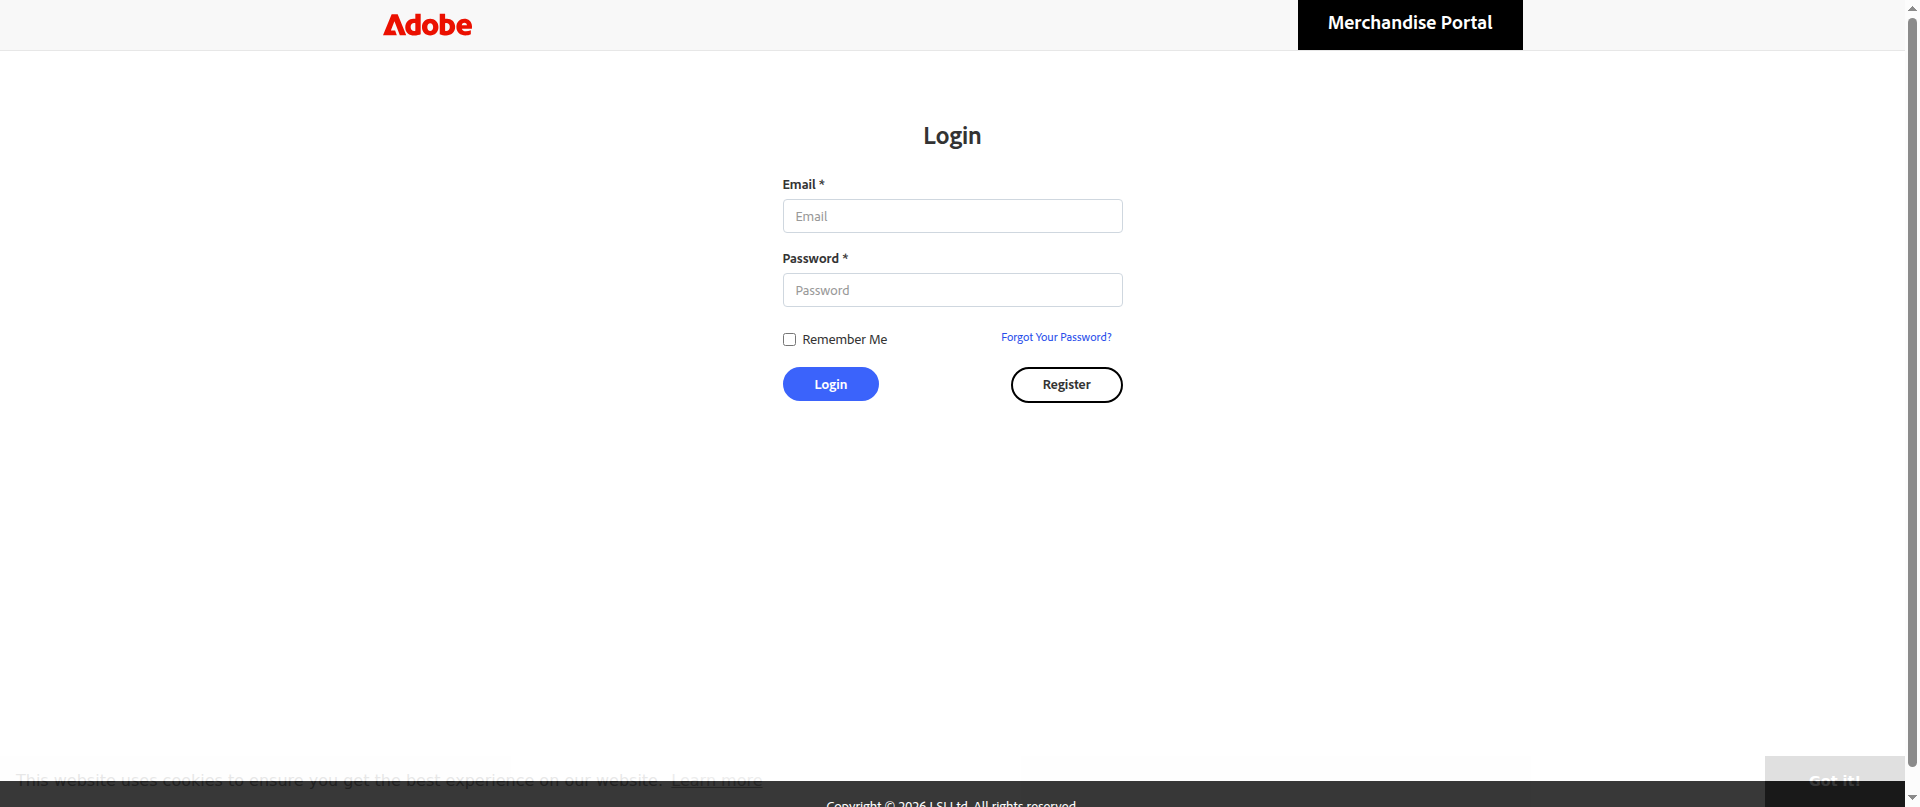 |
OpenPhish | Details | |
| 2026-10-12 11:30 | 2026-10-11 01:03 |  |
OpenPhish | Details | |
| 2026-10-12 11:30 | 2026-10-10 01:15 |  |
OpenPhish | Details | |
| 2026-10-12 11:30 | 2026-10-08 01:02 | 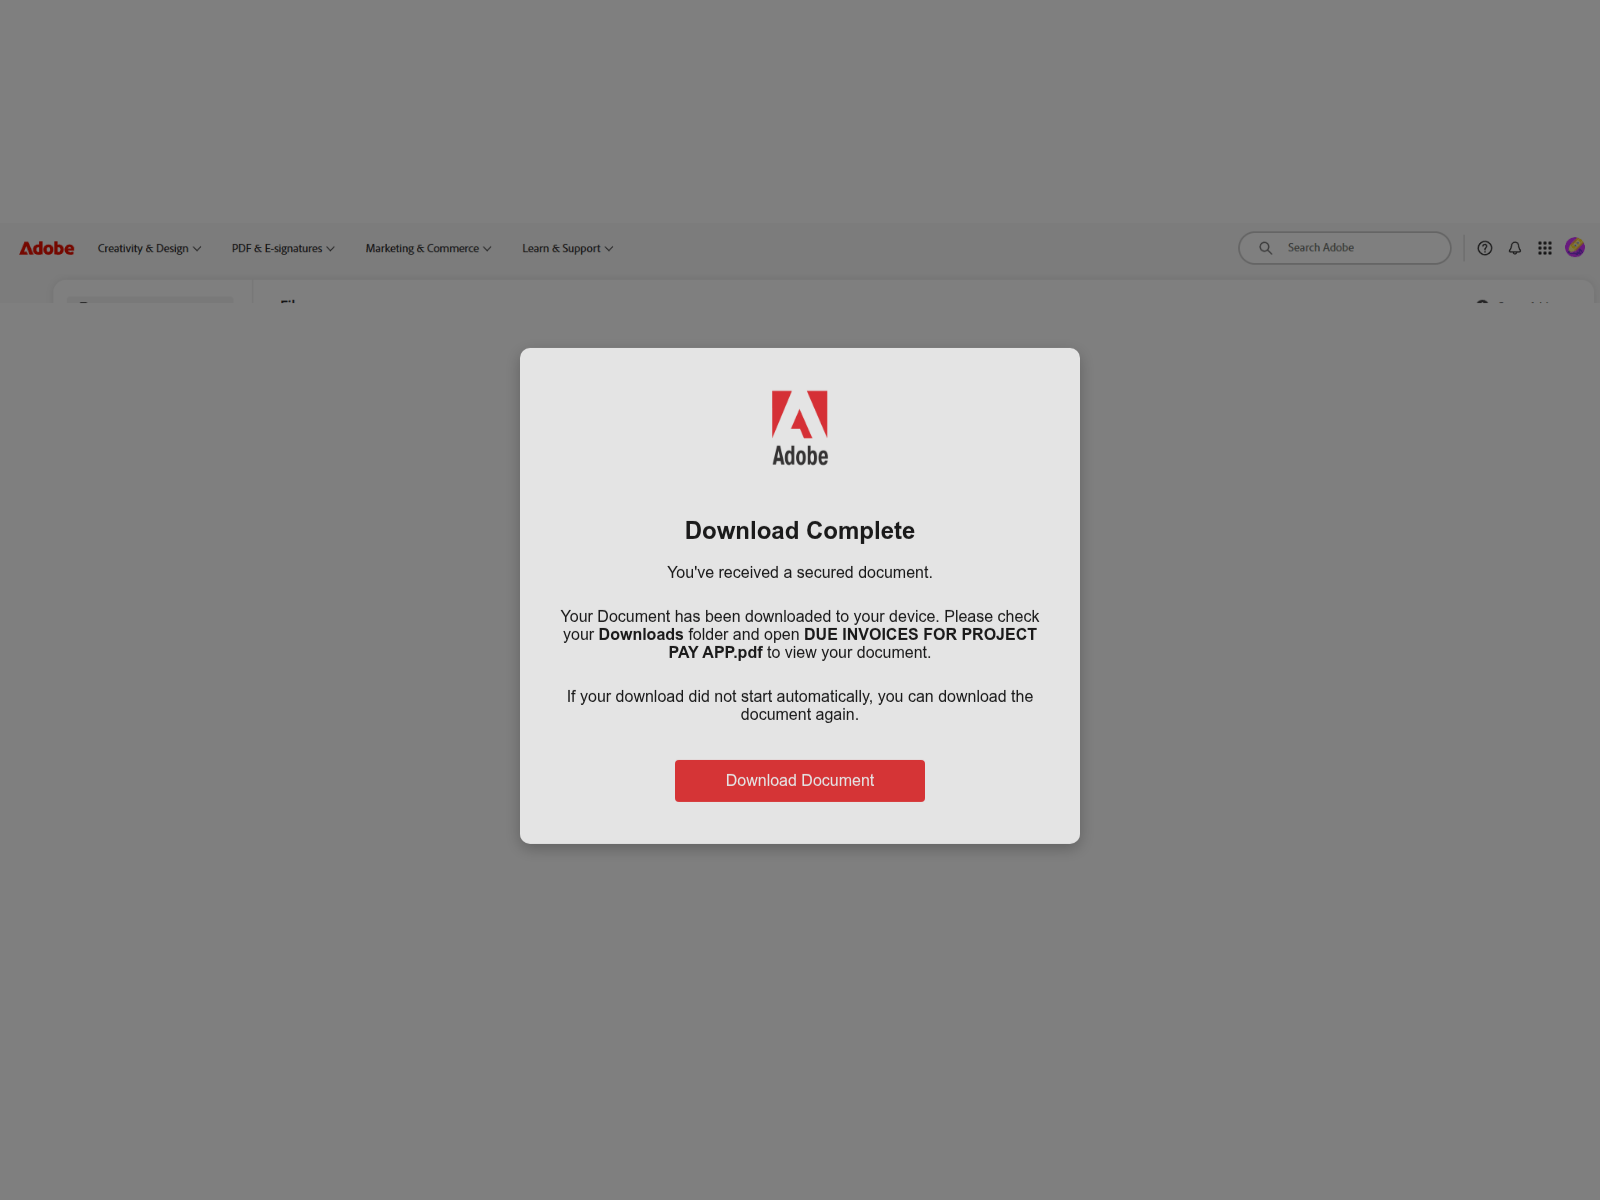 |
OpenPhish | Details | |
| 2026-10-12 11:30 | 2026-10-06 17:25 |  |
GSB | Details | |
| 2026-10-12 11:30 | 2026-10-01 04:02 |  |
OpenPhish TweetFeed | Details | |
| 2026-10-12 11:30 | 2026-10-01 01:02 | 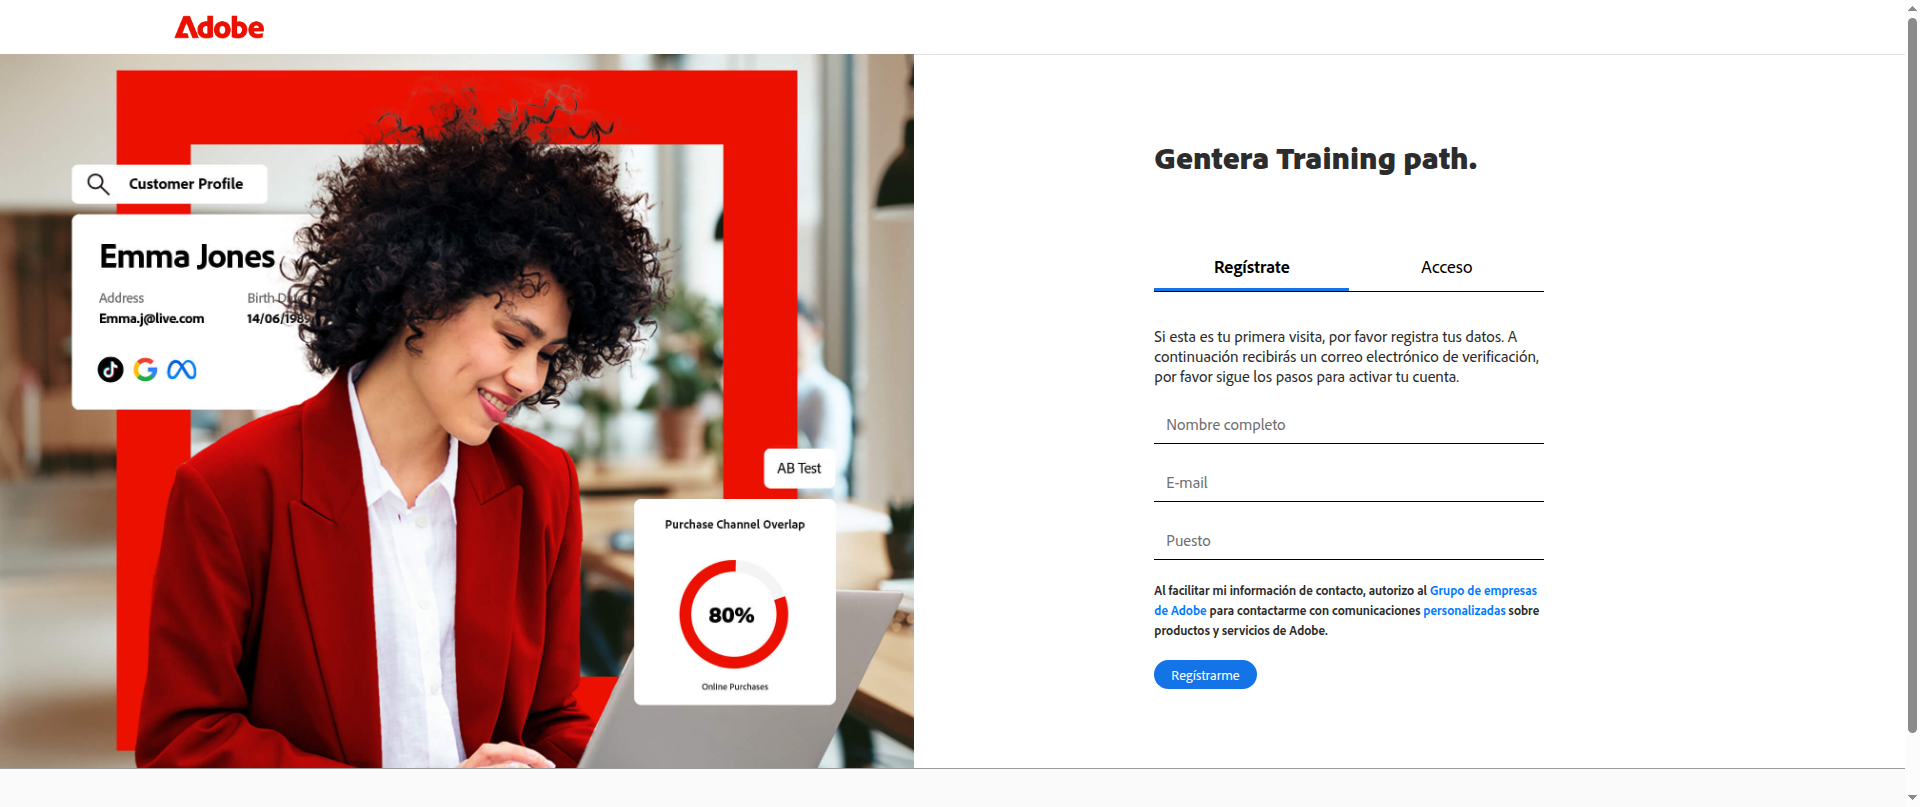 |
OpenPhish | Details | |
| 2026-10-12 11:30 | 2026-09-30 01:03 |  |
OpenPhish PhishTank | Details | |
| 2026-10-12 11:30 | 2026-09-19 06:01 |  |
OpenPhish TweetFeed | Details |
Suspicious sites — confidence is not always 100%. Use for Threat Hunting or watchlists.
| URL | Screenshot | Details |
|---|---|---|
| https://adobe.promorange.co.uk
OpenPhish |
|
Details |
| https://adobeinstaller-virid.…
OpenPhish |
|
Details |
| https://1yz.com/secure/Adobe_…
OpenPhish |
|
Details |
| https://jyothycirrussaviation…
OpenPhish |
|
Details |
| https://adobedelcielo.com
GSB |
|
Details |
| https://strutsupportsystems.c…
OpenPhish TweetFeed |
|
Details |
| https://adobeexperience.com.b…
OpenPhish |
|
Details |
| https://luxora.qpon/AdobeInst…
OpenPhish PhishTank |
|
Details |
| https://taslimaenterprise.com…
OpenPhish TweetFeed |
|
Details |
AIHow to verify a real Adobe URL
- Legitimate Adobe URLs always end in
adobe.com(e.g.www.adobe.com,account.adobe.com). Anything else — including look-alike typosquats, hyphenated variations, or unfamiliar TLDs like.xyz/.top/.vip— is not Adobe. - The padlock icon proves TLS is active, not that the site is safe. Free DV certificates are issued to attackers in minutes; every active site listed above has a valid TLS certificate.
- If you got the link from email, SMS, or social media, do not click it. Open
adobe.comfrom your browser bookmark or type the domain manually. - Real Adobe pages almost never ask for credentials immediately after clicking from a message — treat any such redirect as a phishing attempt until the domain is verified.