Suspicious

Phishings targeting DocuSign

Suspicious and active websites


Phishings targeting Docusign

Suspicious and active websites


Active
4
New (7d)
0
Trend (7d)
↓100%
About
AIE-signature target. Phishing mimics a 'document awaiting signature' notification — a well-worn wrapper for both credential harvest and malware delivery, since the fake link looks routine in a business inbox.
Countries
United StatesUnited States (3) · ArgentinaArgentina (1)
TLS certs
YR2 (2) · YR1 (2)

Suspicious sites — confidence is not always 100%. Use for Threat Hunting or watchlists.
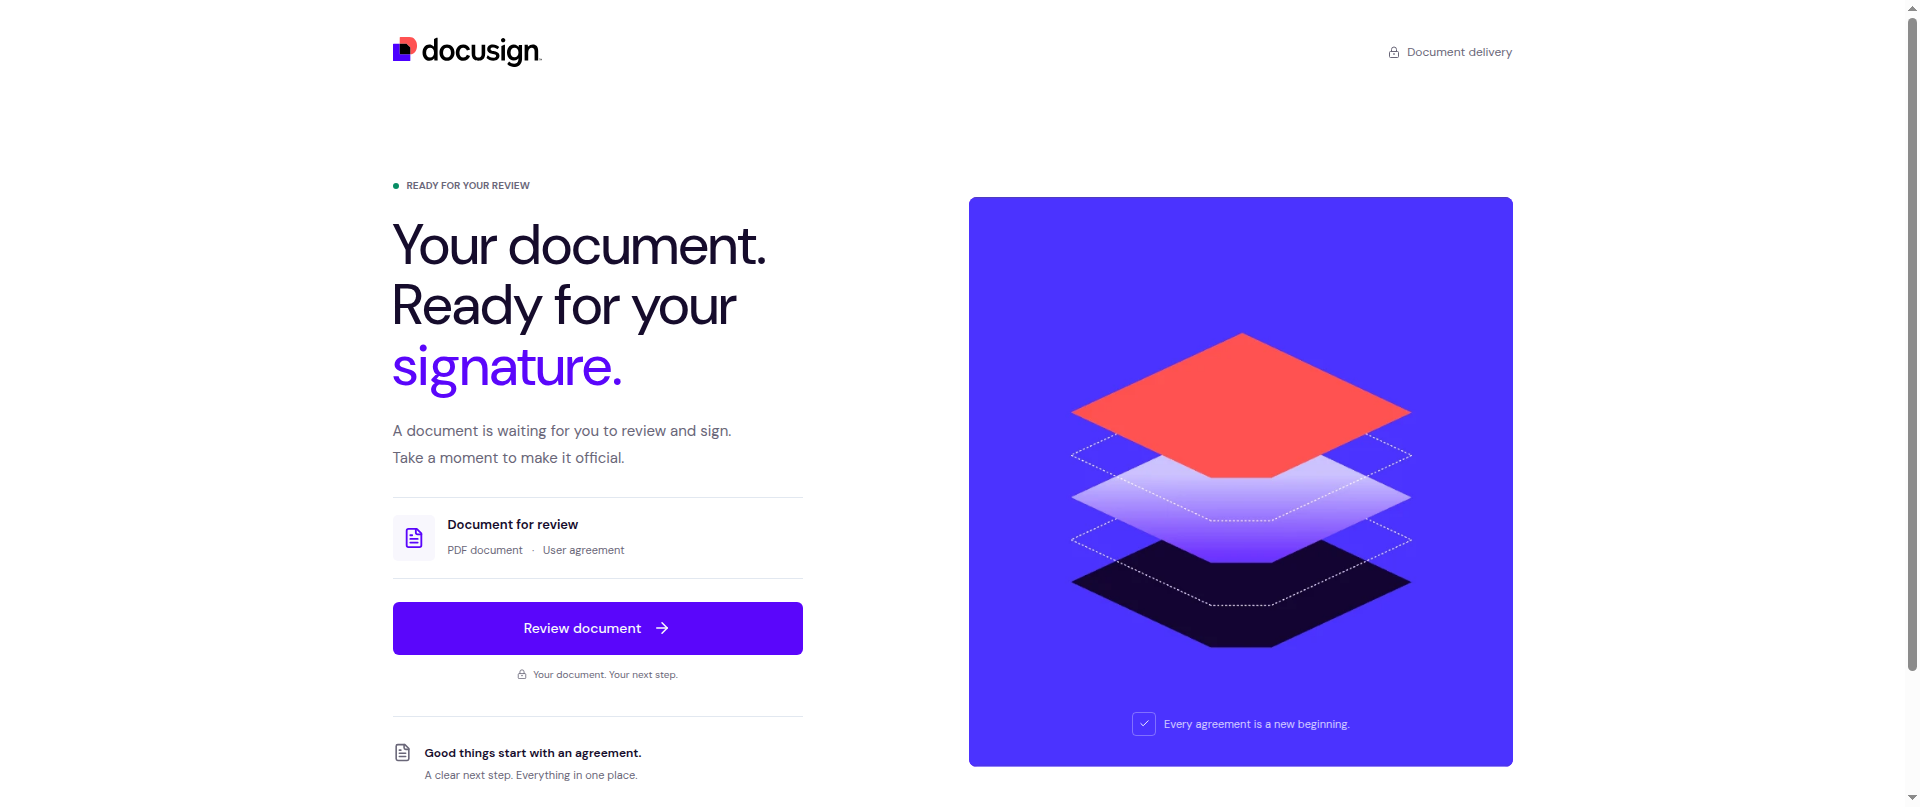
Last check (UTC) First seen (UTC) ▾ URL Screenshot Flags Details
2026-11-01 05:30 2026-10-19 01:02
https://signer.docusign.maccesshub.com/2d8bef1b-e939-49cd-8b59-cdbe9b…
Screenshot of signer.docusign.maccesshub.com OpenPhish Details
2026-11-01 05:30 2026-10-02 13:04
https://piedrasdecolon.com.ar/docusign
Screenshot of piedrasdecolon.com.ar OpenPhish Details
2026-11-01 05:30 2026-09-29 17:25
https://docusign.com.myfolder.secure-docusign.preview.smallflyingarts…
Screenshot of docusign.com.myfolder.secure-docusign.preview.smallflyingarts.net GSB Details
2026-11-01 05:30 2026-09-23 13:03
https://ptai.in/docusign_redirect.html
Screenshot of ptai.in OpenPhish Details

Suspicious sites — confidence is not always 100%. Use for Threat Hunting or watchlists.
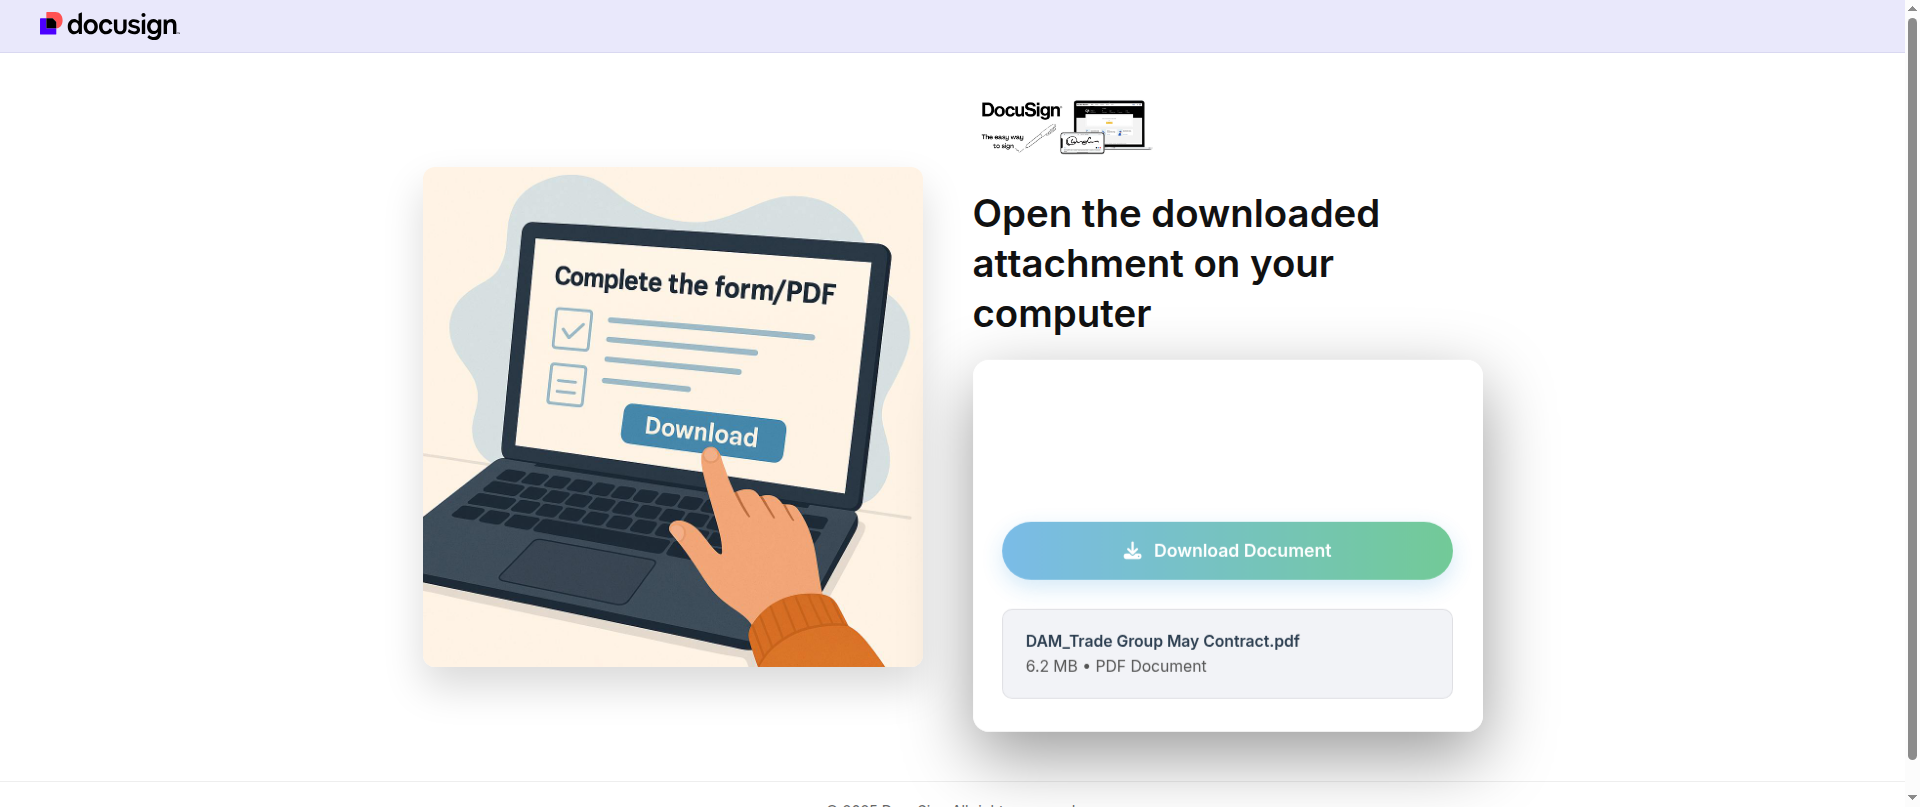
URL Screenshot Details
https://signer.docusign.macce…
OpenPhish
Screenshot of signer.docusign.maccesshub.com Details
https://piedrasdecolon.com.ar…
OpenPhish
Screenshot of piedrasdecolon.com.ar Details
https://docusign.com.myfolder…
GSB
Screenshot of docusign.com.myfolder.secure-docusign.preview.smallflyingarts.net Details
https://ptai.in/docusign_redi…
OpenPhish
Screenshot of ptai.in Details

AIHow to verify a real DocuSign URL

  • Legitimate DocuSign URLs always end in docusign.com (e.g. www.docusign.com, account.docusign.com). Anything else — including look-alike typosquats, hyphenated variations, or unfamiliar TLDs like .xyz / .top / .vip — is not DocuSign.
  • The padlock icon proves TLS is active, not that the site is safe. Free DV certificates are issued to attackers in minutes; every active site listed above has a valid TLS certificate.
  • If you got the link from email, SMS, or social media, do not click it. Open docusign.com from your browser bookmark or type the domain manually.
  • Real DocuSign pages almost never ask for credentials immediately after clicking from a message — treat any such redirect as a phishing attempt until the domain is verified.