Phishing detection: facebook.tamil.bid
Facebook Screenshot
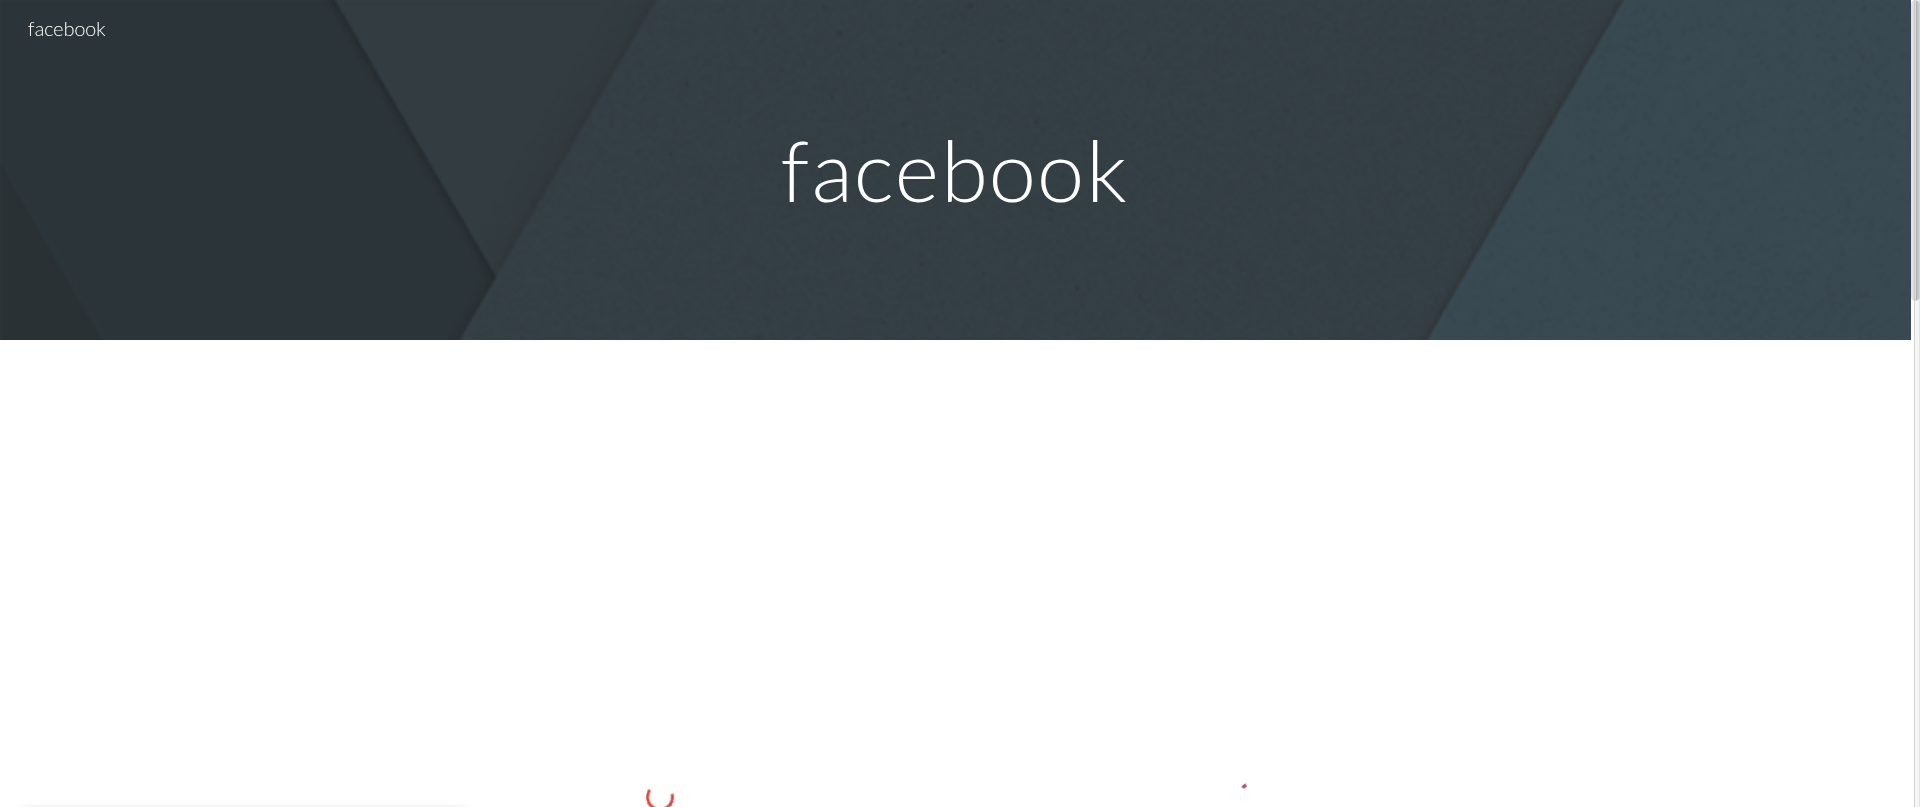
Investigate
Domain
facebook.tamil.bid31 CT hosts on apex
 urlscan
 VirusTotal
 Whois
IP
192.178.183.121
 ipinfo
 Greynoise
URL
https://facebook.tamil.bid
Phishunt analysis Beta
32
medium suspicion suspiciousheuristic risk score · not a probability
Why?
- +5.3 Keyword match
- +4.5 Brand in title
- +4.1 Brand in screenshot
- +4.1 Site cluster
- +3.0 OpenPhish
- +2.6 Brand in subdomain
- +2.2 Country mismatch
- +1.3 ASN reputation
- +1.1 No HSTS header
- +0.7 Brand in cert SAN
- +0.7 Unrecognised DNS provider
- +0.6 Registrar reputation
- +0.6 Suspicious TLD
- +0.4 Long domain
- +0.3 Free CA
- +0.1 External scripts
- +0.1 Deep subdomain
20 signals fired · detector v3.0.0
AI analysis AIBeta
Credential harvesting
Fake Facebook page hosted on an unrelated .bid domain that places the brand name as a subdomain and in the page title. It appears to harvest Facebook login credentials. Flagged by OpenPhish, with no HSTS and a free Let's Encrypt certificate.
Brand in subdomainOpenPhishBrand in title
AI-generated from stored detector signals - the AI never visited the site. · 2026-10-14 · confidence 80%
Domain & Network
Whois
Registrar
Dominet (HK) Limited
Network
IP
192.178.183.121 Google services
Country
 Germany
Hosting
Google LLC
ASN
AS15169
TLS Cert
WR3
External detection
OpenPhish
CleanGoogle Safe Browsing · PhishTank · TweetFeed · urlscan.io
Requests
Resources
Observables
Related websites
Report this phishing
Submit to blocklists