Phishing detection: fedex.bkeva.cfd
FedEx Screenshot
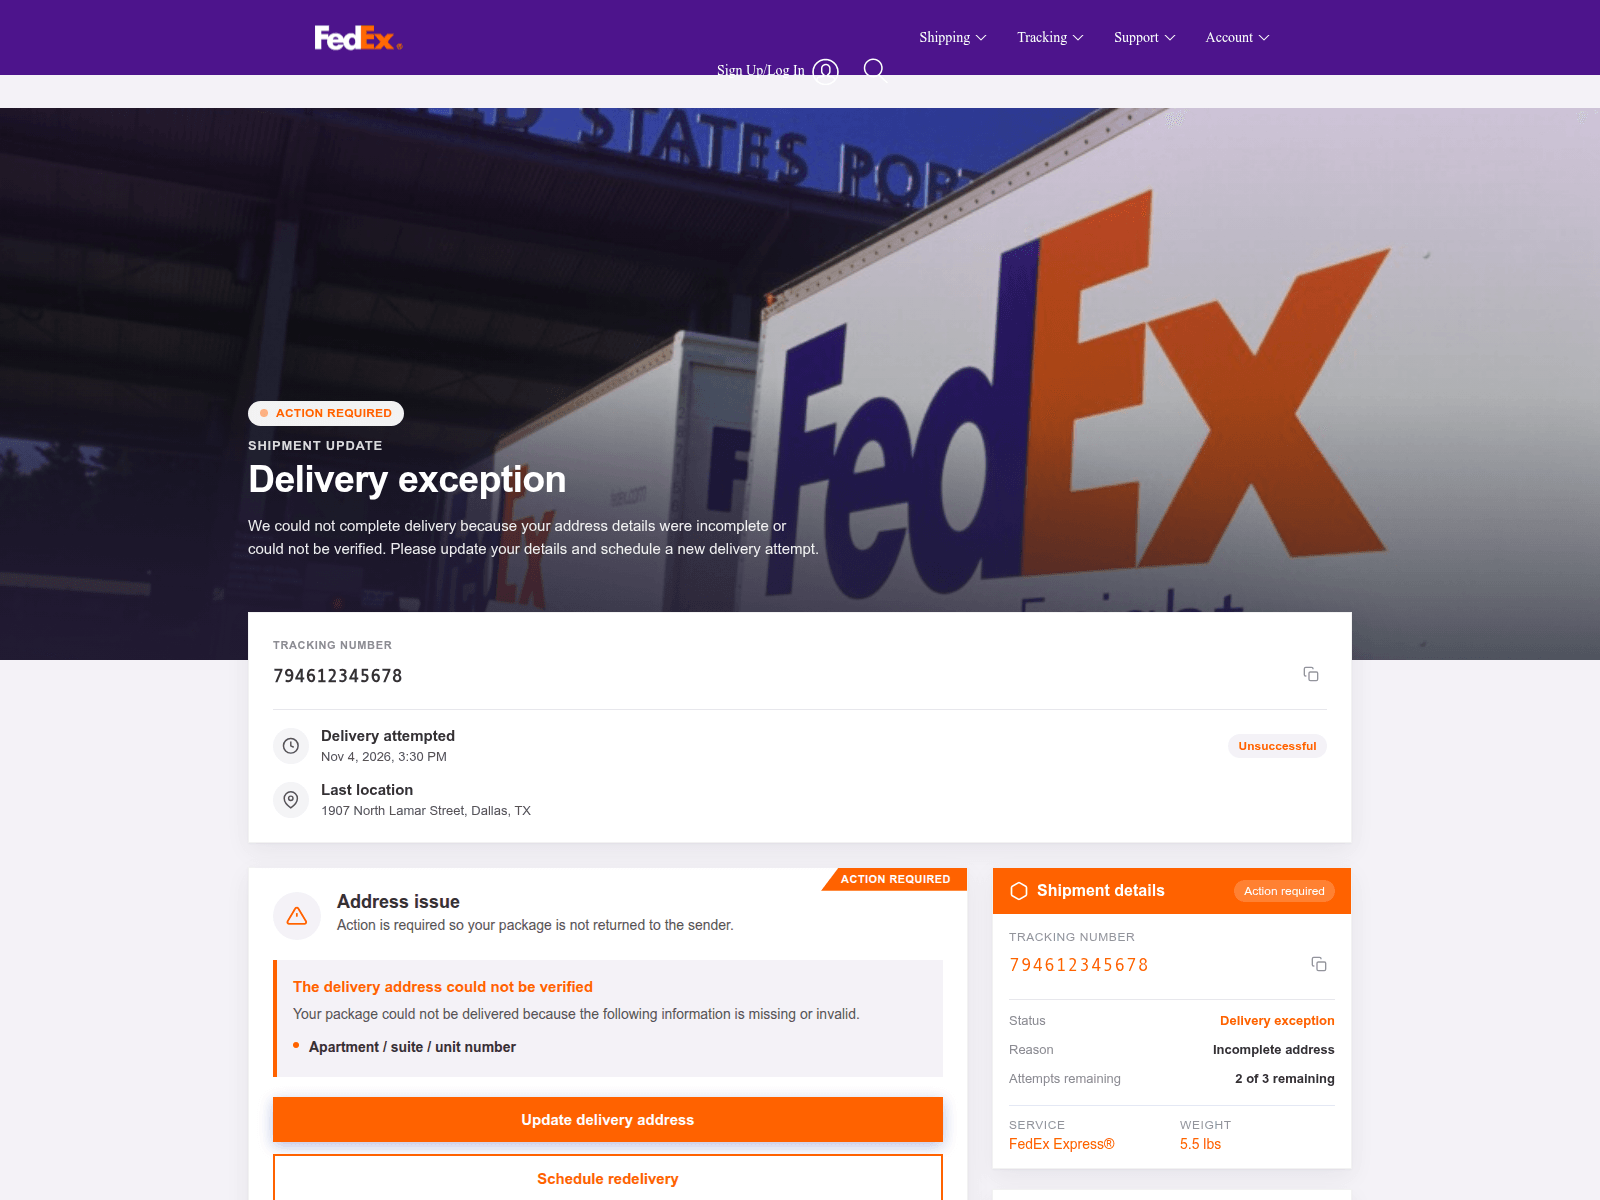
Screenshot captured by urlscan.io on 2026-11-06T04:30 UTC: our own render of this page came back blank.
Investigate
Domain
fedex.bkeva.cfd1 CT host on apex
 urlscan
 VirusTotal
 Whois
IP
47.89.137.76
 ipinfo
 Greynoise
URL
https://fedex.bkeva.cfd/com.us
Phishunt analysis Beta
44
high suspicion likely_phishingheuristic risk score · not a probability
Why?
- +6.1 Google Safe Browsing
- +5.3 Keyword match
- +5.1 Site cluster
- +4.5 Brand in title
- +4.0 Young domain
- +3.5 ASN reputation
- +3.4 Shared IP cluster
- +3.0 OpenPhish
- +2.6 Brand in subdomain
- +1.1 No CSP header
- +0.9 Young certificate
- +0.9 No registrar lock
- +0.7 Brand in cert SAN
- +0.7 Brand typo
- +0.7 Unrecognised DNS provider
- +0.6 Suspicious TLD
- +0.3 Free CA
- +0.3 Long domain
- +0.1 Deep subdomain
22 signals fired · detector v3.0.0
AI analysis AIBeta
Delivery scam
FedEx-branded subdomain on a throwaway .cfd domain, one of many on the same Alibaba Cloud IP, likely a delivery scam collecting personal or payment details. Flagged by Google Safe Browsing and OpenPhish.
Brand in subdomainGoogle Safe BrowsingShared IP cluster
AI-generated from stored detector signals - the AI never visited the site. · 2026-11-06 · confidence 85%
Domain & Network
Whois
Registrar
Dynadot Inc
Network
IP
47.89.137.76
Country
 United States
ASN
AS45102
TLS Cert
YR1
GSB category: SOCIAL_ENGINEERING
CleanPhishTank · TweetFeed · urlscan.io
Requests
Resources
Observables
Related websites
Report this phishing
Submit to blocklists