Phishing detection: vint.yjiankuny.workers.dev
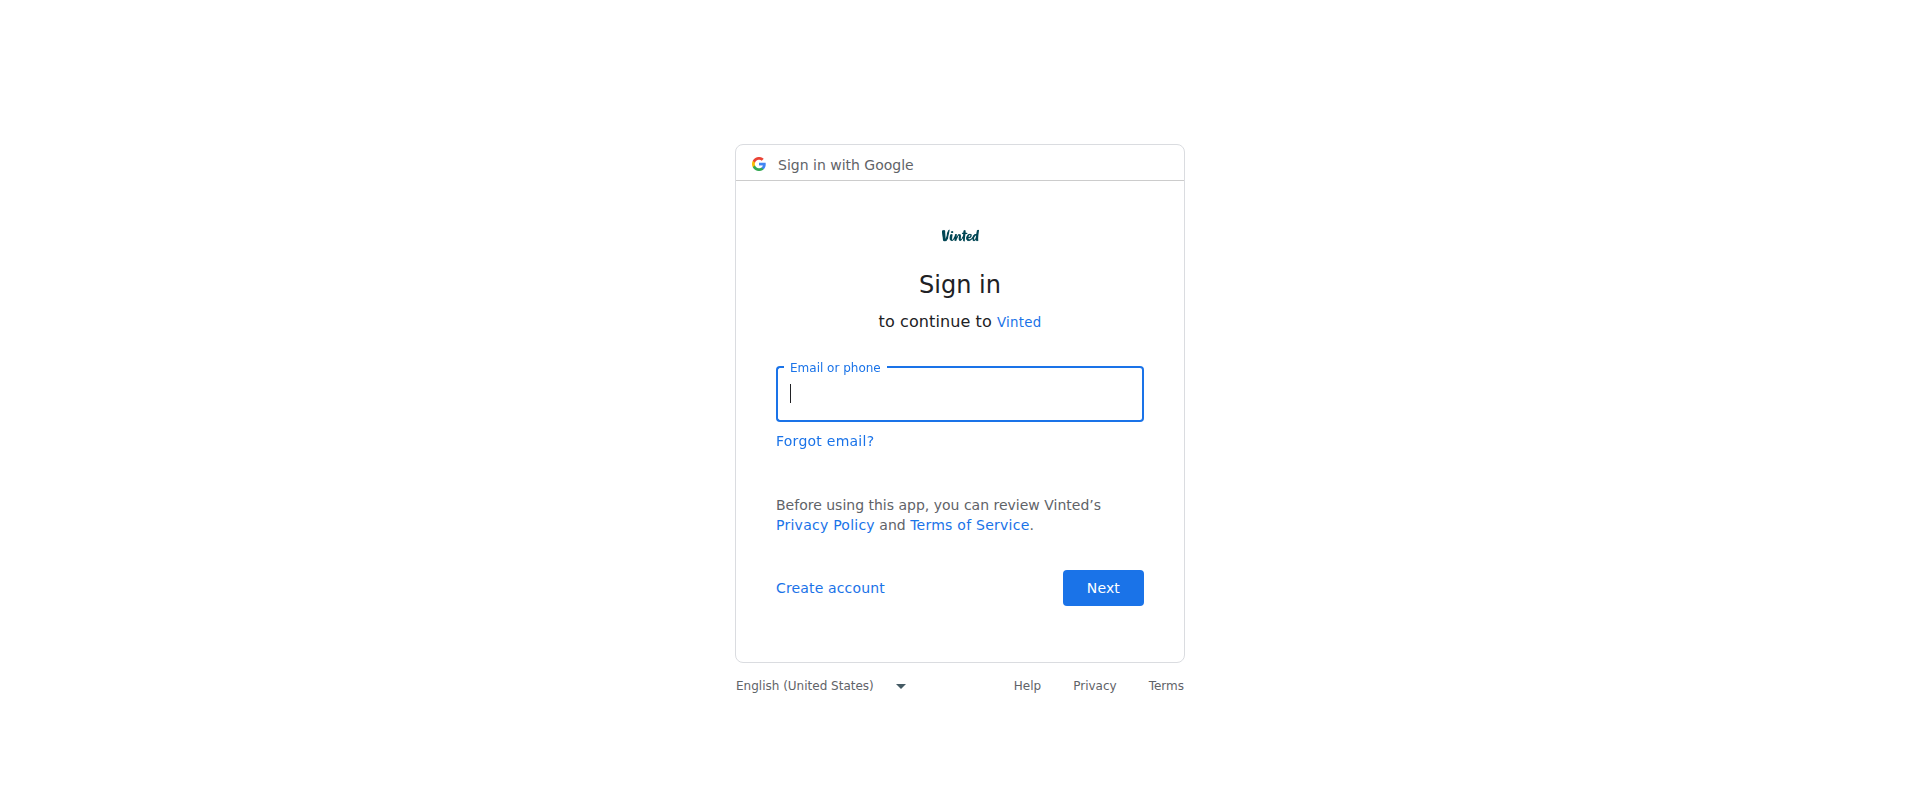
Google Screenshot
Investigate
Domain
vint.yjiankuny.workers.dev6 CT hosts on apex
 urlscan
 VirusTotal
 Whois
IP
104.21.10.181
 ipinfo
 Greynoise
URL
https://vint.yjiankuny.workers.dev/auth/google/oauth?redire…
Phishunt analysis Beta
23
low suspicionheuristic risk score · not a probability
Why?
- +5.3 Keyword match
- +5.1 Site cluster
- +4.1 Brand in screenshot
- +3.0 OpenPhish
- +2.0 Young domain
- +1.1 ASN reputation
- +0.6 Brand impersonation in path
- +0.6 Login text in screenshot
- +0.6 Suspicious TLD
- +0.5 Long domain
- +0.3 Free CA
- +0.3 Deep subdomain
14 signals fired · detector v3.0.0
AI analysis AIBeta
Credential harvesting
A Cloudflare Workers-hosted page mimicking a Google OAuth sign-in flow with a signup redirect. The brand does not match the host, the page links out to the brand, and OpenPhish lists it, indicating Google account credential harvesting.
Brand impersonation in pathOpenPhishPaaS host
AI-generated from stored detector signals - the AI never visited the site. · 2026-10-24 · confidence 72%
Domain & Network
Whois
Registrar
CloudFlare, Inc.
Network
IP
104.21.10.181 Cloudflare CDN
Country
 United States
Hosting
Cloudflare, Inc.
ASN
AS13335
TLS Cert
WE1
External detection
OpenPhish
CleanGoogle Safe Browsing · PhishTank · TweetFeed · urlscan.io
Requests
Resources
Observables
Related websites
Report this phishing
Submit to blocklists