Phishing detection: 4zjerlm.yourwebs.app
Google Screenshot
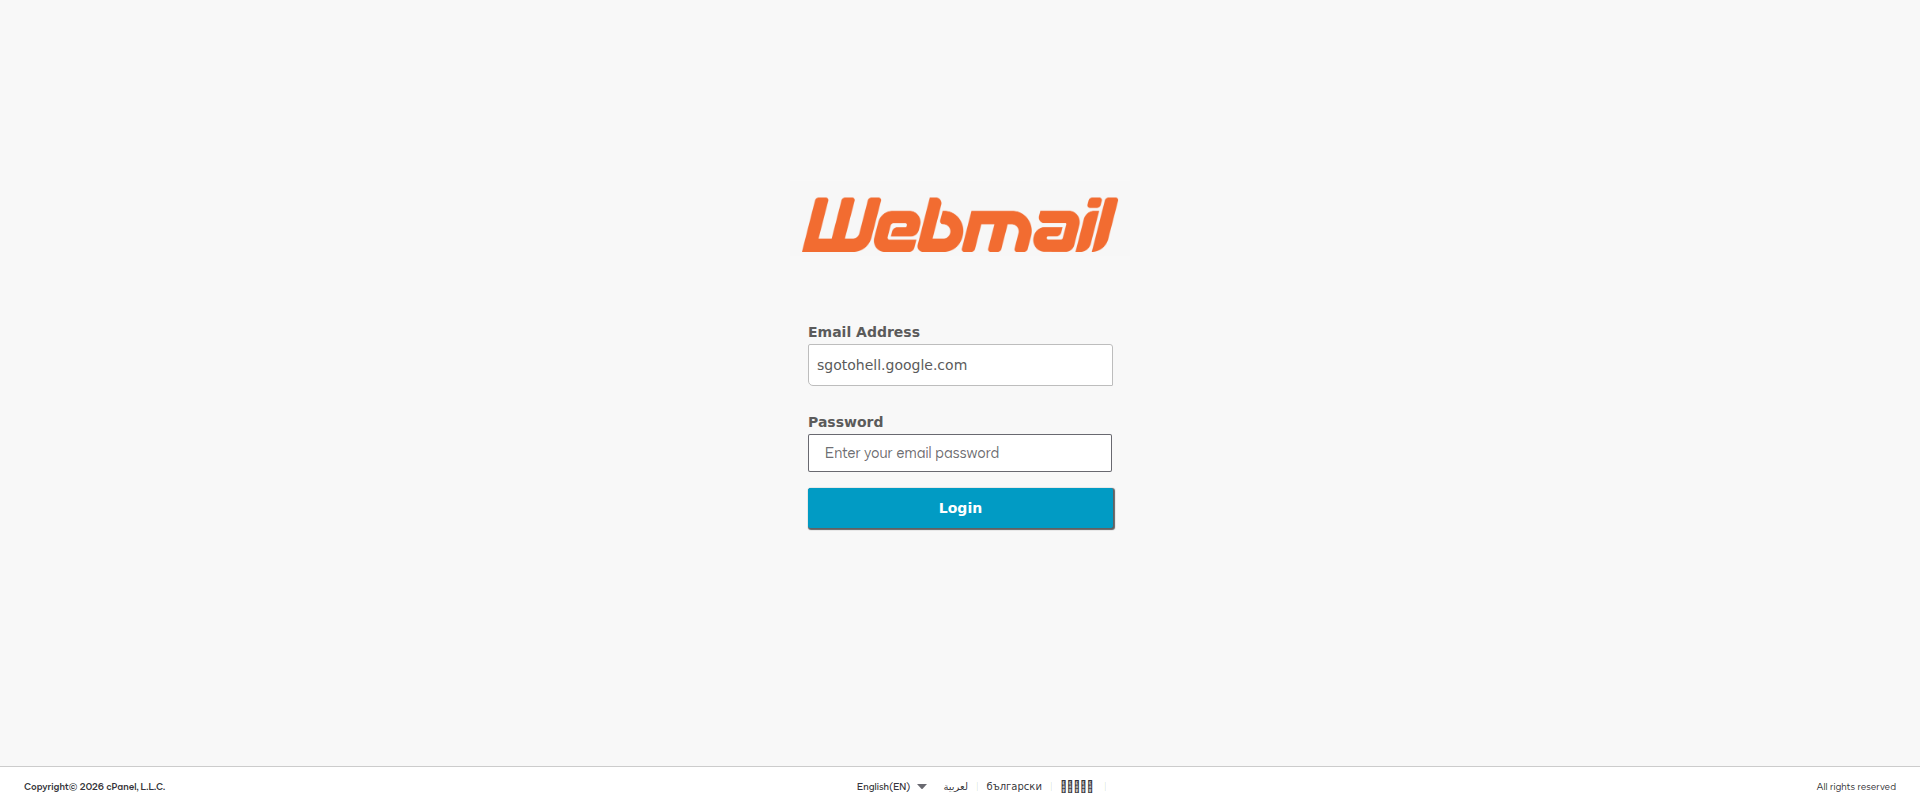
Investigate
Domain
4zjerlm.yourwebs.app1 CT host on apex
 urlscan
 VirusTotal
 Whois
IP
188.114.97.3
 ipinfo
 Greynoise
URL
https://4zjerlm.yourwebs.app/#sgotohell.google.com
Phishunt analysis Beta
45
high suspicion likely_phishingheuristic risk score · not a probability
Why?
- +6.1 Google Safe Browsing
- +5.3 Keyword match
- +5.1 Site cluster
- +3.9 Password field
- +3.4 Shared IP cluster
- +3.0 OpenPhish
- +1.3 ASN reputation
- +1.1 No HSTS header
- +0.8 Young domain
- +0.6 Suspicious TLD
- +0.4 Long domain
- +0.3 Free CA
- +0.1 External scripts
- +0.1 Deep subdomain
- Boosted to 45: Google-flagged credential form
18 signals fired · detector v3.0.0
AI analysis AIBeta
Credential harvesting
A randomly named subdomain on a free app-hosting service impersonates Google, with a fragment crafted to look like a Google address. It is flagged by Google Safe Browsing (social engineering) and OpenPhish and sits behind Cloudflare, likely harvesting Google account credentials.
Google Safe BrowsingOpenPhishKeyword match
AI-generated from stored detector signals - the AI never visited the site. · 2026-10-21 · confidence 75%
Domain & Network
Whois
Registrar
CloudFlare, Inc.
Network
IP
188.114.97.3 Cloudflare CDN
Country
 United States
Hosting
Cloudflare, Inc.
ASN
AS13335
TLS Cert
YE1
GSB category: SOCIAL_ENGINEERING
CleanPhishTank · TweetFeed · urlscan.io
Requests
Resources
Observables
Related websites
Report this phishing
Submit to blocklists