Phishing detection: autoconfig.hsbccpersonalonlinebanking.com
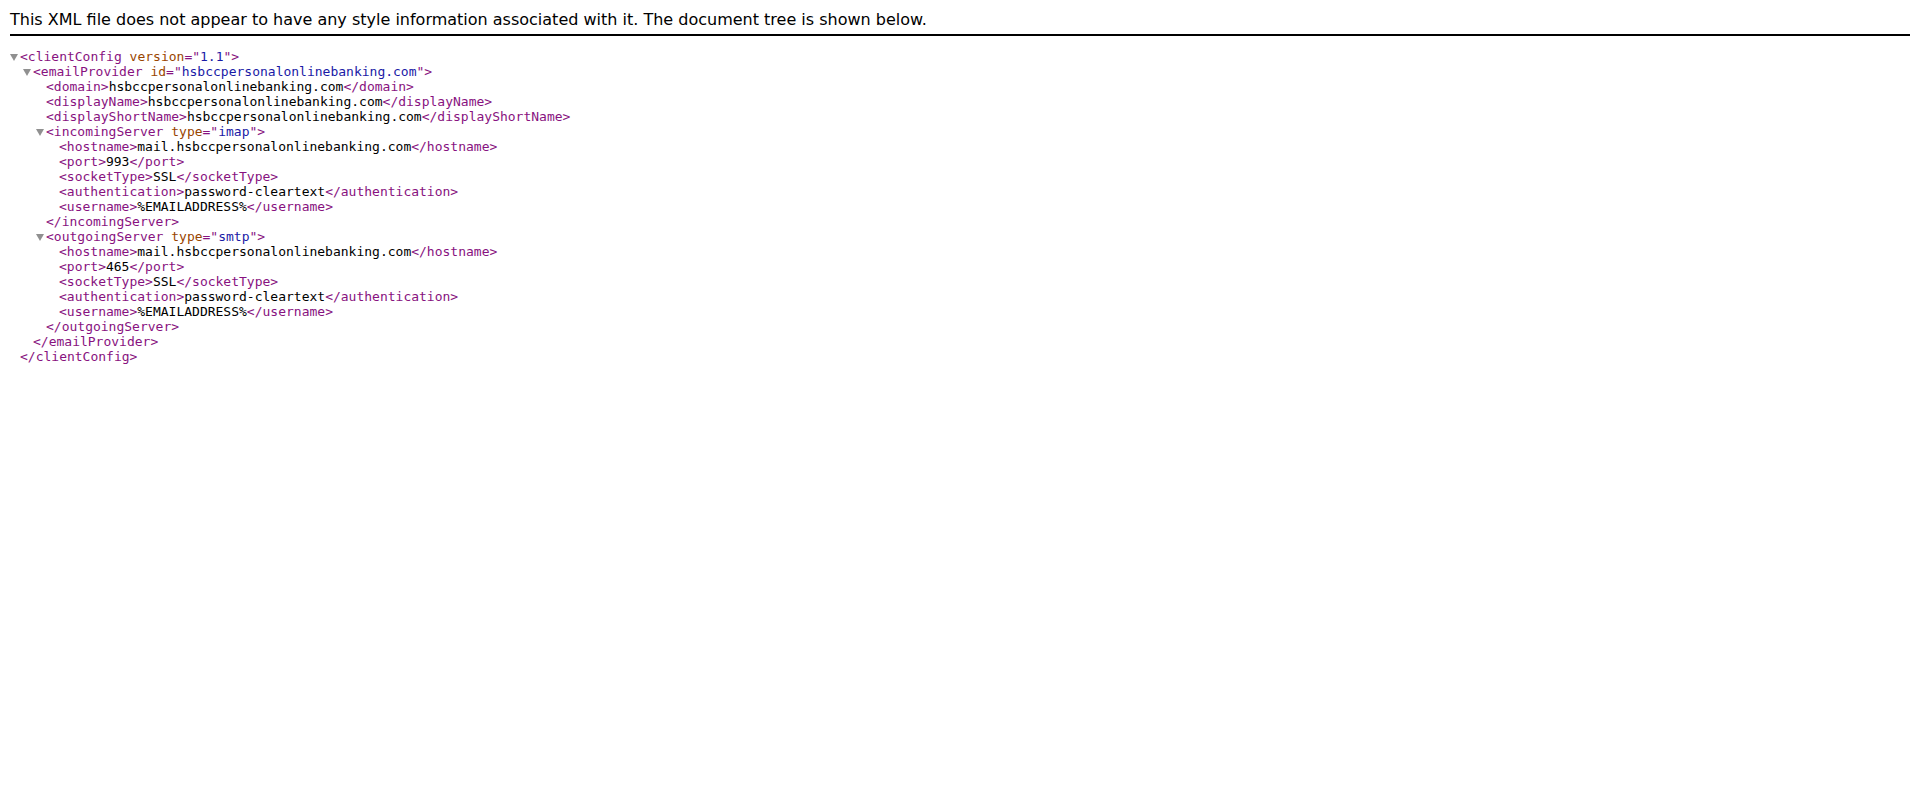
HSBC Screenshot
Investigate
Domain
autoconfig.hsbccpersonalonlinebanking.com10 CT hosts on apex
 urlscan
 VirusTotal
 Whois
IP
198.38.92.102
 ipinfo
 Greynoise
URL
https://autoconfig.hsbccpersonalonlinebanking.com
Phishunt analysis Beta
38
medium suspicion suspiciousheuristic risk score · not a probability
Why?
- +6.1 Google Safe Browsing
- +5.3 Keyword match
- +4.1 Brand in screenshot
- +3.7 Brand in domain label
- +3.5 ASN reputation
- +3.4 Shared IP cluster
- +2.3 Cert reuse
- +2.0 Site cluster
- +1.1 No CSP header
- +1.1 No HSTS header
- +0.8 Young domain
- +0.7 Brand in cert SAN
- +0.7 Unrecognised DNS provider
- +0.6 Long domain
- +0.6 Login text in screenshot
- +0.6 Registrar reputation
- +0.5 Young certificate
- +0.3 Free CA
- +0.2 Suspicious TLD
- +0.1 Deep subdomain
22 signals fired · detector v3.0.0
AI analysis AIBeta
Credential harvesting
Uses an autoconfig subdomain on the same fraudulent HSBC-branded apex domain, consistent with email infrastructure staging for a broader credential harvesting campaign. Flagged by Google Safe Browsing as social engineering and registered through an abuse-prone registrar in the UK.
Google Safe BrowsingBrand in domain labelRegistrar reputation
AI-generated from stored detector signals - the AI never visited the site. · 2026-09-16 · confidence 75%
Domain & Network
Whois
Registrar
Upperlink Limited
Network
Country
 United Kingdom
Hosting
WHG Hosting Services Ltd
ASN
AS51713
TLS Cert
YR1
External detection
Google Safe Browsing
GSB category: SOCIAL_ENGINEERING
CleanOpenPhish · PhishTank · TweetFeed · urlscan.io
Requests
Resources
Observables
Related websites
Report this phishing
Submit to blocklists