Phishing detection: microsoftconfig-3.vercel.app
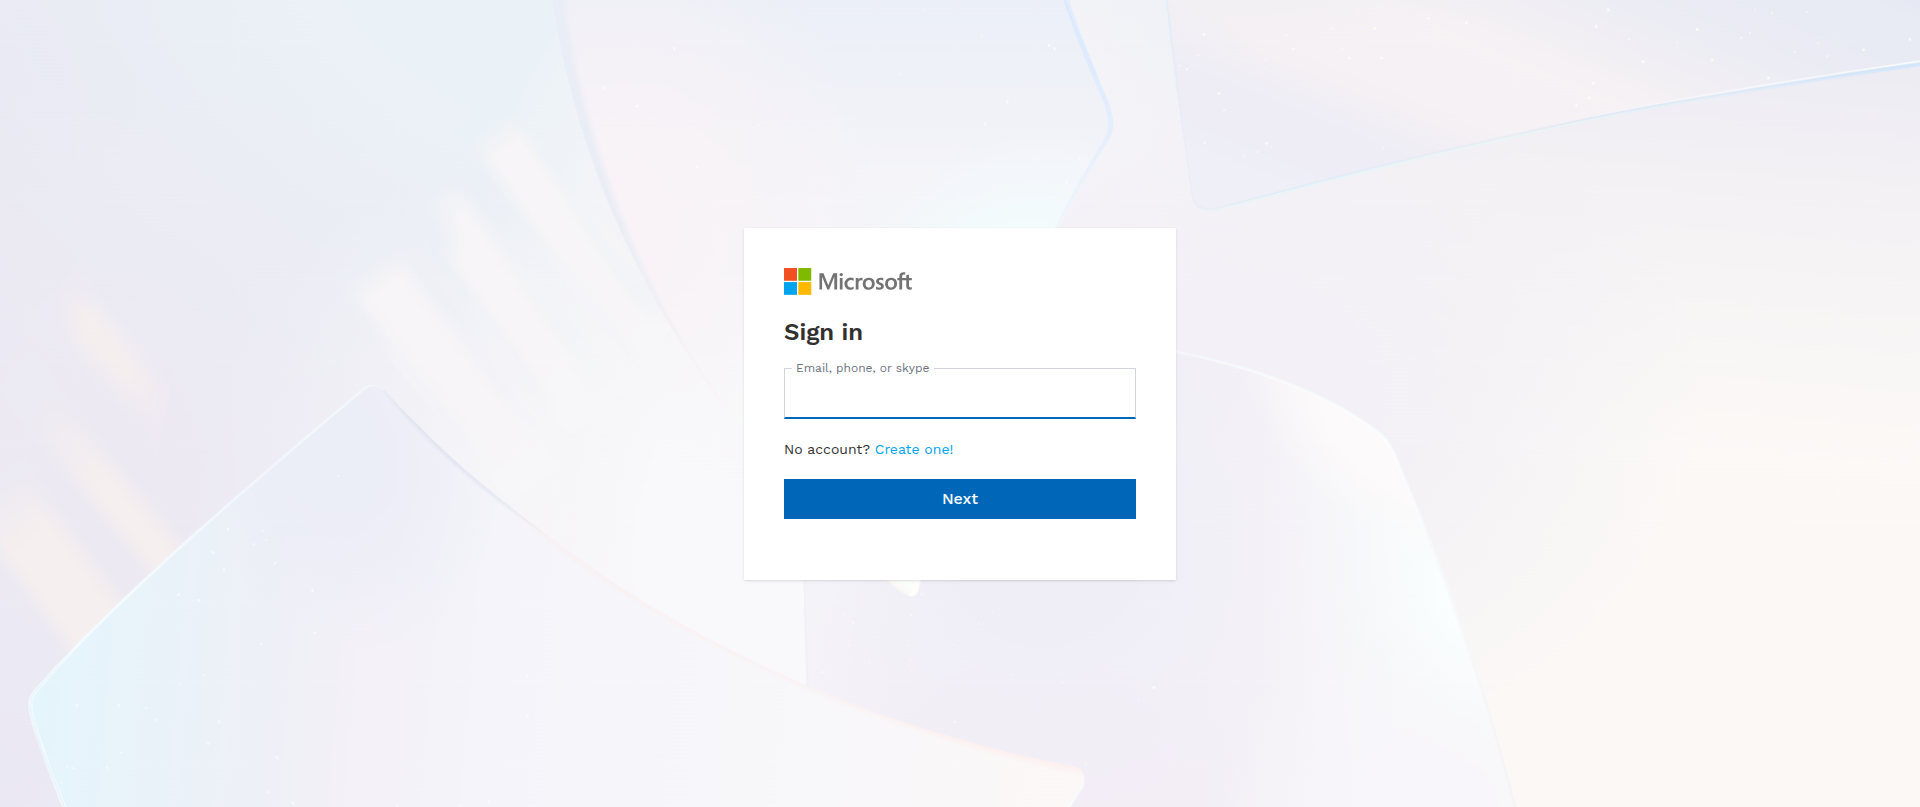
Microsoft Screenshot
Investigate
Domain
microsoftconfig-3.vercel.app0 CT hosts on apex
 urlscan
 VirusTotal
 Whois
IP
216.198.79.3
 ipinfo
 Greynoise
URL
https://microsoftconfig-3.vercel.app
Phishunt analysis Beta
47
high suspicion likely_phishingheuristic risk score · not a probability
Why?
- +6.1 Google Safe Browsing
- +5.3 Keyword match
- +5.1 Site cluster
- +4.1 Brand in screenshot
- +3.9 Password field
- +3.7 Brand in domain label
- +3.4 Cert reuse
- +3.4 Shared IP cluster
- +3.0 OpenPhish
- +3.0 PhishTank
- +2.0 Young domain
- +1.1 ASN reputation
- +1.1 No CSP header
- +0.6 Long domain
- +0.6 Login text in screenshot
- +0.6 Suspicious TLD
- +0.3 Free CA
- +0.1 Hyphens
- +0.1 External scripts
- +0.1 Deep subdomain
25 signals fired · detector v3.0.0
AI analysis AIBeta
Credential harvesting
Impersonates Microsoft on a Vercel app subdomain with a password input field. Listed by OpenPhish and flagged by Google Safe Browsing, it harvests Microsoft account credentials. Shares IP and certificate with similar sites.
Password fieldOpenPhishGoogle Safe Browsing
AI-generated from stored detector signals - the AI never visited the site. · 2026-10-25 · confidence 85%
Domain & Network
Whois
Registrar
Tucows Domains Inc
Network
IP
216.198.79.3
Country
 United States
Hosting
Amazon.com, Inc.
ASN
AS16509
TLS Cert
WR1
GSB category: SOCIAL_ENGINEERING
CleanTweetFeed · urlscan.io
Requests
Resources
Observables
Related websites
Report this phishing
 Network / ASN
Amazon.com, Inc.
 Brand owner
Microsoft
Submit to blocklists