Phishing detection: wildlands.acltci.com
Microsoft Screenshot
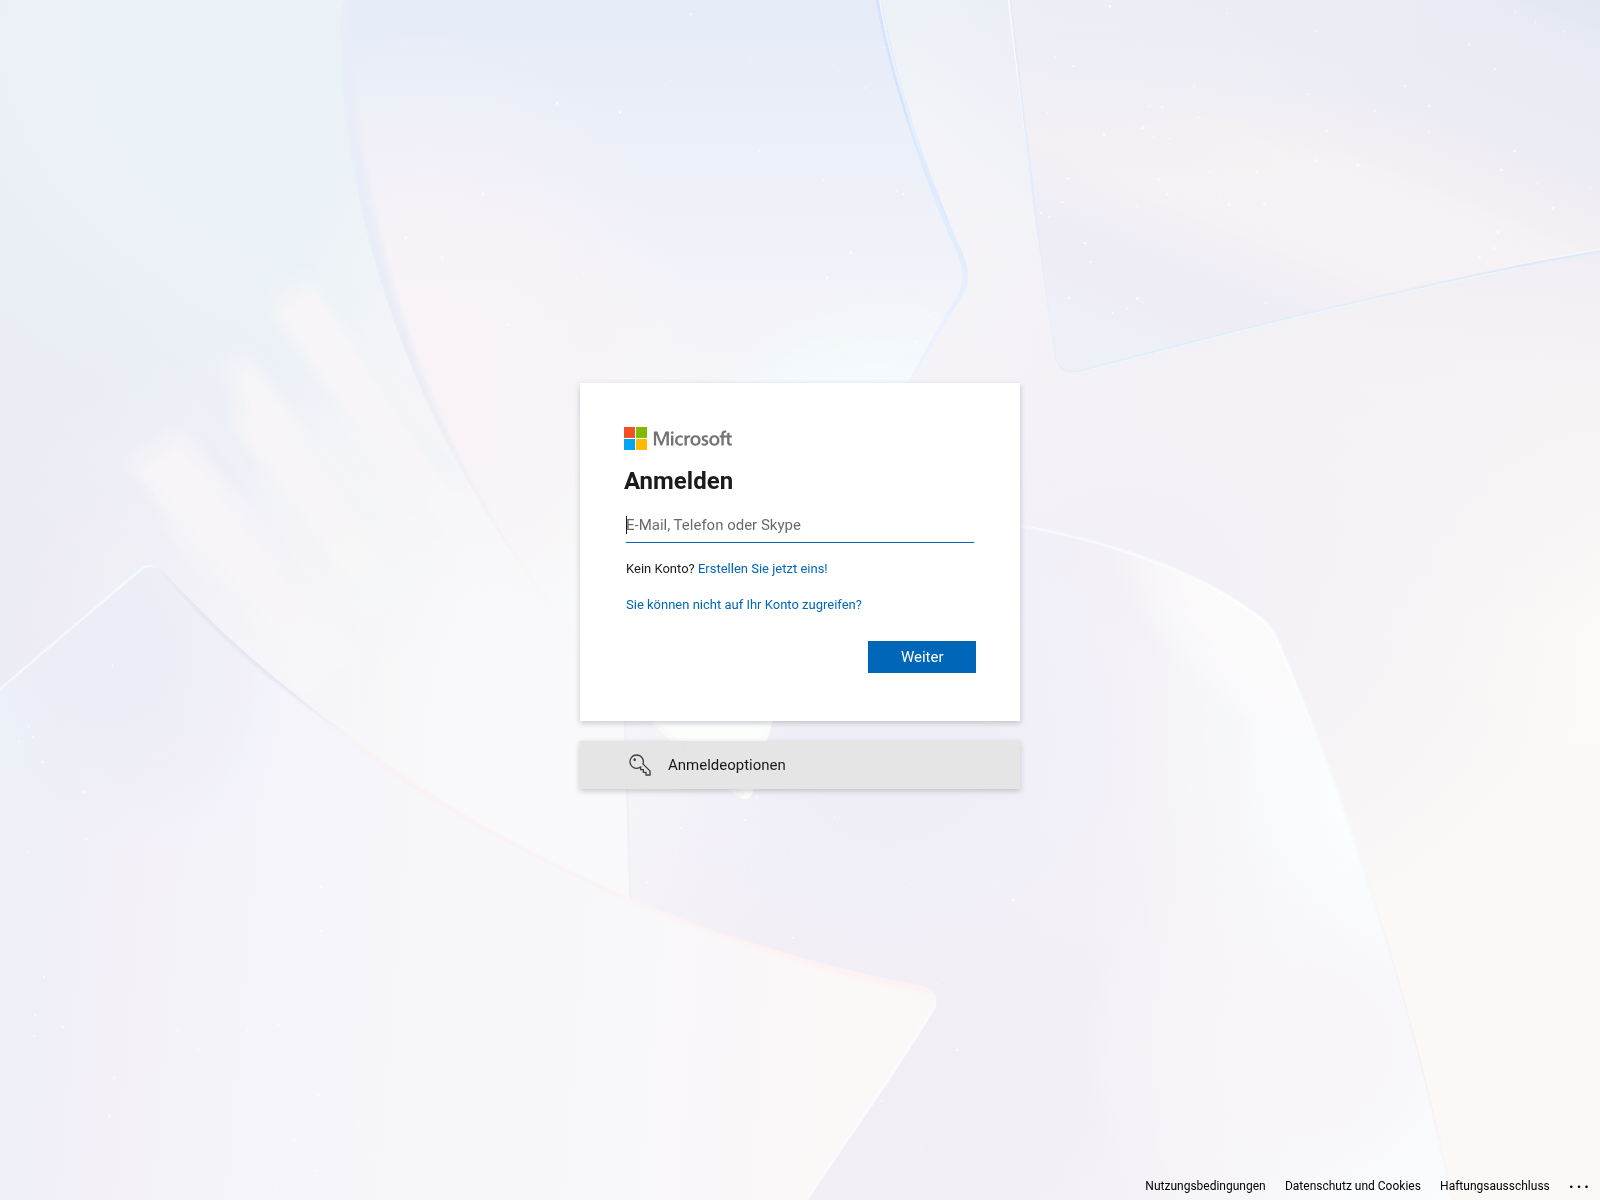
Screenshot captured by urlscan.io on 2026-09-24T01:02 UTC: our own render of this page came back blank.
Investigate
Domain
wildlands.acltci.com27 CT hosts on apex
 urlscan
 VirusTotal
 Whois
IP
216.24.57.18
 ipinfo
 Greynoise
URL
https://wildlands.acltci.com/login?method=signin&mode=secur…
Phishunt analysis Beta
27
low suspicionheuristic risk score · not a probability
Why?
- +5.3 Keyword match
- +4.1 Brand in screenshot
- +3.9 Password field
- +3.0 OpenPhish
- +3.0 PhishTank
- +1.1 ASN reputation
- +1.1 No CSP header
- +1.1 No HSTS header
- +0.9 Young certificate
- +0.7 Brand typo
- +0.7 Unrecognised DNS provider
- +0.6 Brand impersonation in path
- +0.4 Long domain
- +0.4 Credential path
- +0.3 Free CA
- +0.2 Suspicious TLD
- +0.1 External scripts
- +0.1 Deep subdomain
22 signals fired · detector v3.0.0
AI analysis AIBeta
Credential harvesting
Site impersonates Microsoft login using a suspicious URL path with OAuth-style parameters and a redirect to the legitimate Microsoft online login service. Hosted on Render infrastructure and flagged by OpenPhish. Likely a credential harvesting proxy or adversary-in-the-middle page.
OpenPhishCredential pathKeyword match
AI-generated from stored detector signals - the AI never visited the site. · 2026-09-24 · confidence 65%
Domain & Network
Whois
Registrar
Tucows Domains Inc.
Network
IP
216.24.57.18
Country
 United States
Hosting
Render
ASN
AS397273
TLS Cert
WE1
Requests
Resources
Observables
Related websites
Report this phishing
 Brand owner
Microsoft
Submit to blocklists