Phishing detection: admin.foroshgahma.com
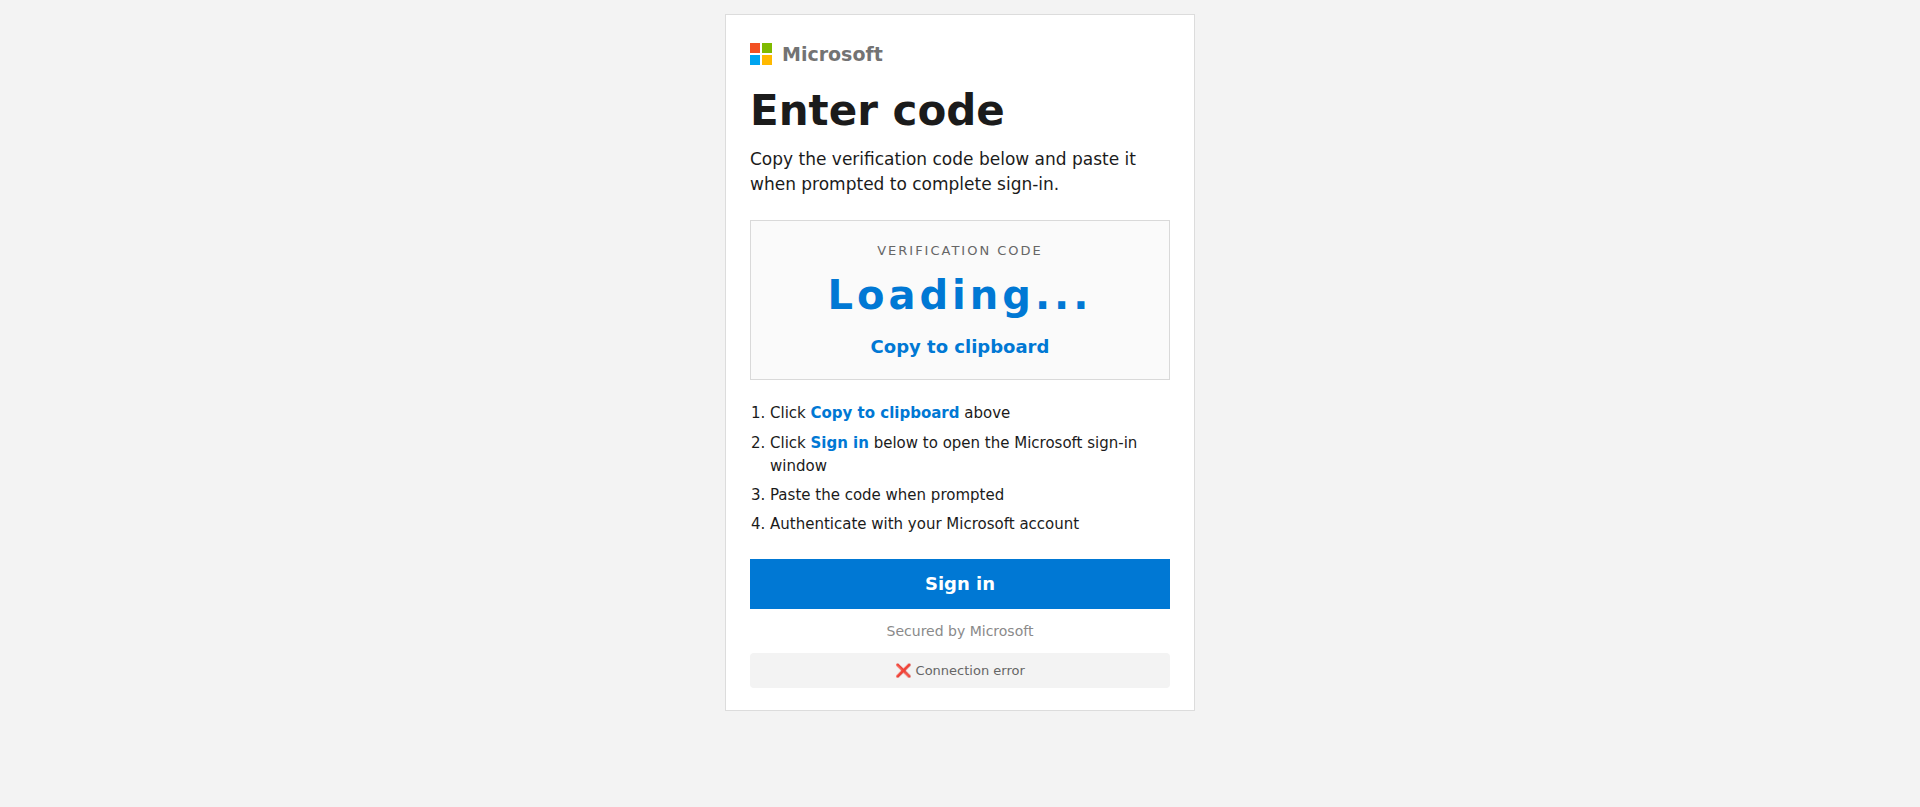
Microsoft Screenshot
Investigate
Domain
admin.foroshgahma.com6 CT hosts on apex
 urlscan
 VirusTotal
 Whois
IP
45.139.11.78
 ipinfo
 Greynoise
URL
http://admin.foroshgahma.com/rfp/proposal/shared/microsoft_…
Phishunt analysis Beta
32
medium suspicion suspiciousheuristic risk score · not a probability
Why?
- +5.3 Keyword match
- +5.1 urlscan.io
- +4.5 Brand in title
- +4.1 Brand in screenshot
- +3.0 OpenPhish
- +2.2 Country mismatch
- +1.1 ASN reputation
- +1.1 No CSP header
- +1.1 No HSTS header
- +0.7 Unrecognised DNS provider
- +0.6 Brand impersonation in path
- +0.6 Login text in screenshot
- +0.6 Registrar reputation
- +0.5 Young certificate
- +0.4 Long domain
- +0.3 Free CA
- +0.2 Obfuscated JavaScript
- +0.2 Suspicious TLD
- +0.1 Deep subdomain
20 signals fired · detector v3.0.0
AI analysis AIBeta
Credential harvesting
Fake Microsoft passwordless sign-in page served over plain HTTP from an unrelated admin subdomain on an Iranian host, likely harvesting Microsoft account credentials. Uses obfuscated JavaScript and is flagged by OpenPhish and urlscan.
Brand impersonation in pathObfuscated JavaScripturlscan.io
AI-generated from stored detector signals - the AI never visited the site. · 2026-11-17 · confidence 82%
Domain & Network
Whois
Network
IP
45.139.11.78
Country
 Iran
Iran
Hosting
Vandad Vira Hooman LLC
ASN
AS60631
TLS Cert
YR1
CleanGoogle Safe Browsing · PhishTank · TweetFeed
Report this phishing
 Brand owner
Microsoft
Submit to blocklists