Phishing detection: im.nbpublic.com
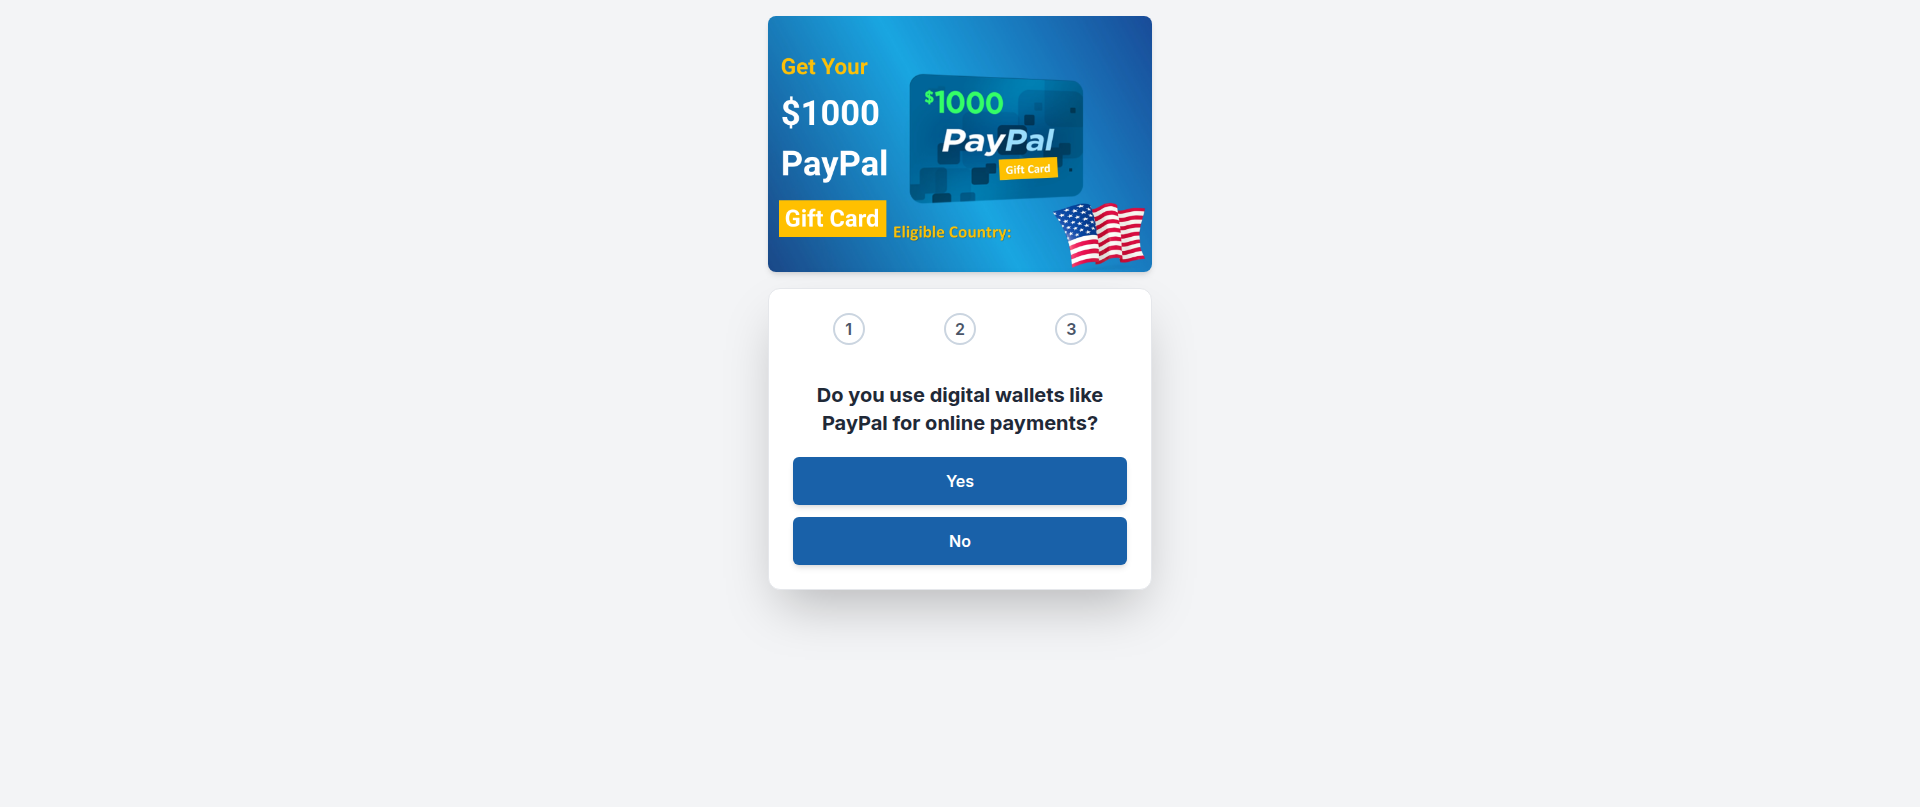
PayPal Screenshot
Investigate
Domain
im.nbpublic.com1 CT host on apex
 urlscan
 VirusTotal
 Whois
IP
172.67.199.187
 ipinfo
 Greynoise
URL
https://im.nbpublic.com/loading_page/paypal/paypal_cf_3/ind…
Phishunt analysis Beta
24
low suspicionheuristic risk score · not a probability
Why?
- +5.3 Keyword match
- +5.1 Site cluster
- +4.1 Brand in screenshot
- +3.0 OpenPhish
- +1.9 ASN reputation
- +1.1 No CSP header
- +1.1 No HSTS header
- +0.6 Brand impersonation in path
- +0.5 Young certificate
- +0.3 Free CA
- +0.3 Long domain
- +0.2 Suspicious TLD
- +0.1 External scripts
- +0.1 Deep subdomain
16 signals fired · detector v3.0.0
AI analysis AIBeta
Credential harvesting
A third-party domain hosts a PayPal-branded phishing page within a nested path, likely to harvest PayPal credentials or payment information. Confirmed malicious by OpenPhish; the heavily encoded URL token suggests a tracked, targeted phishing campaign hosted on Cloudflare infrastructure.
OpenPhishBrand impersonation in pathKeyword match
AI-generated from stored detector signals - the AI never visited the site. · 2026-09-16 · confidence 65%
Domain & Network
Whois
Registrar
GoDaddy.com, LLC
Network
Country
 United States
Hosting
Cloudflare, Inc.
ASN
AS13335
TLS Cert
WE1
External detection
OpenPhish
CleanGoogle Safe Browsing · PhishTank · TweetFeed · urlscan.io
Requests
Resources
Observables
Related websites
Report this phishing
 Brand owner
PayPal
Submit to blocklists