Phishing detection: roblox.com.ml
Roblox Screenshot
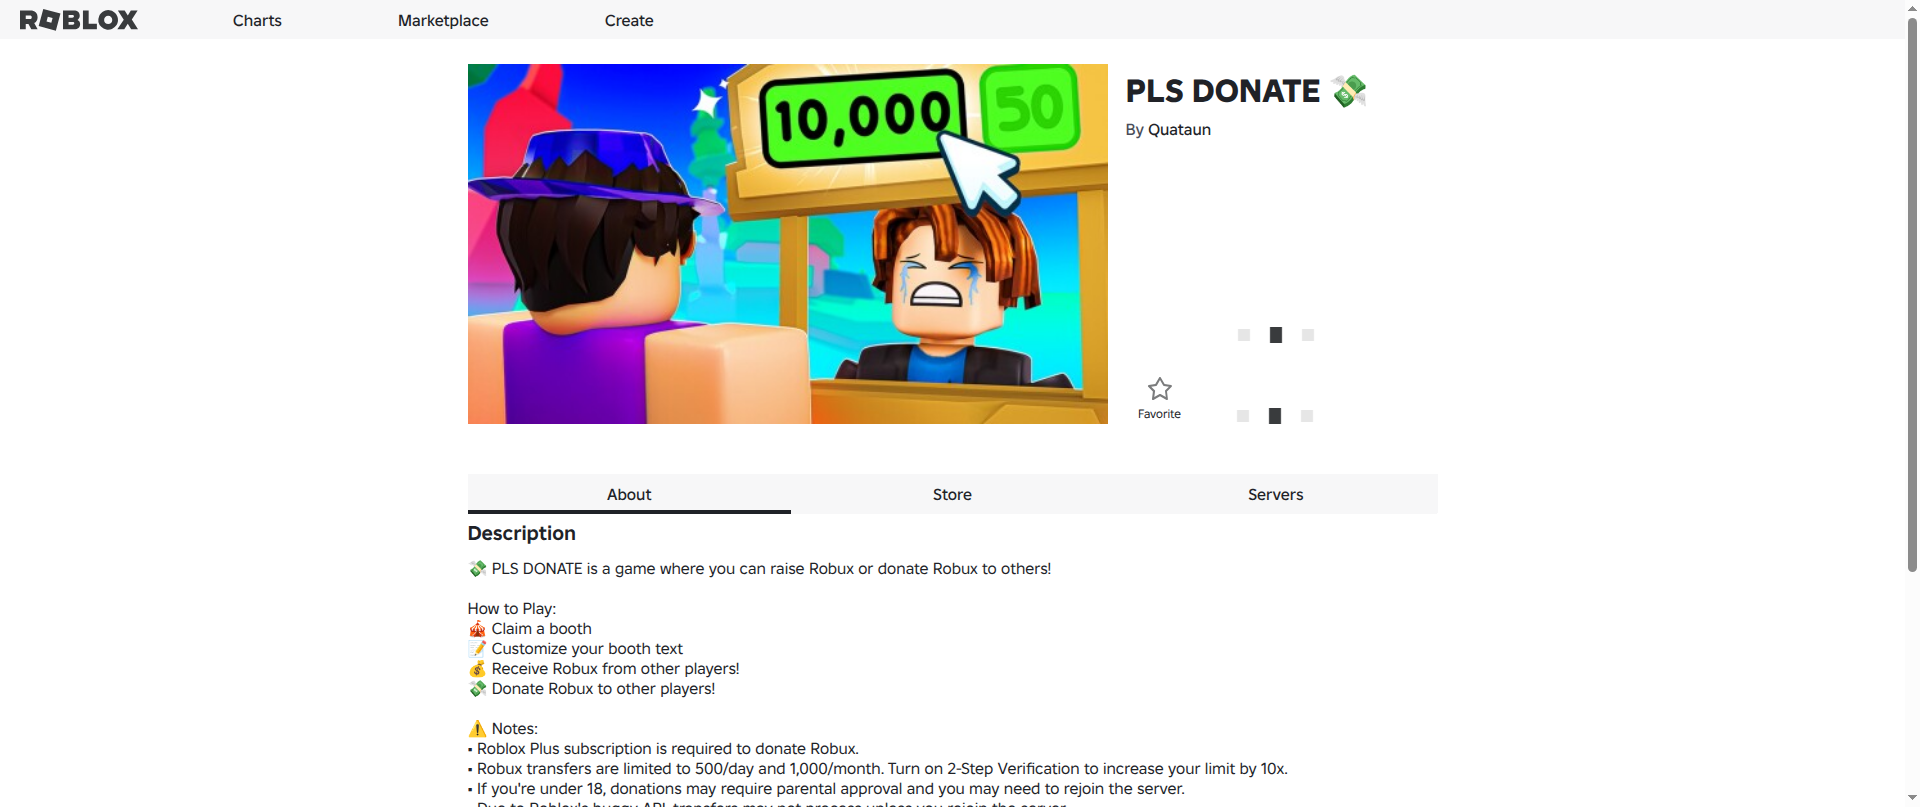
Investigate
Domain
roblox.com.ml2 CT hosts on apex
 urlscan
 VirusTotal
 Whois
IP
31.56.209.148
 ipinfo
 Greynoise
URL
https://roblox.com.ml/games/8737602449/PLS-DONATE?privateSe…
Phishunt analysis Beta
32
medium suspicion suspiciousheuristic risk score · not a probability
Why?
- +5.3 Keyword match
- +4.5 Brand in title
- +4.1 Brand in screenshot
- +3.2 Brand favicon
- +3.0 OpenPhish
- +2.2 Country mismatch
- +1.3 Brand typo
- +1.2 ASN reputation
- +1.1 No CSP header
- +1.1 No HSTS header
- +1.0 Site cluster
- +0.7 Brand in cert SAN
- +0.6 Brand impersonation in path
- +0.6 Registrar reputation
- +0.6 Suspicious TLD
- +0.5 Young certificate
- +0.3 Free CA
- +0.3 Long domain
- +0.2 External scripts
- +0.1 Deep subdomain
21 signals fired · detector v3.0.0
AI analysis AIBeta
Credential harvesting
A lookalike domain on the .ml TLD uses the Roblox name and a 'PLS DONATE' game path with a private-server link parameter to imitate Roblox, likely luring players into credential theft. Listed in OpenPhish.
OpenPhishBrand impersonation in pathBrand in title
AI-generated from stored detector signals - the AI never visited the site. · 2026-10-01 · confidence 75%
Domain & Network
Whois
Registrar
AGETIC Registrar
Network
Country
 The Netherlands
Hosting
SWISSNET LLC
ASN
AS209373
TLS Cert
YE2
External detection
OpenPhish
CleanGoogle Safe Browsing · PhishTank · TweetFeed · urlscan.io
Requests
Resources
Observables
Related websites
Report this phishing
Submit to blocklists