Phishing detection: webproxy.goku8.workers.dev
Wells Fargo Screenshot
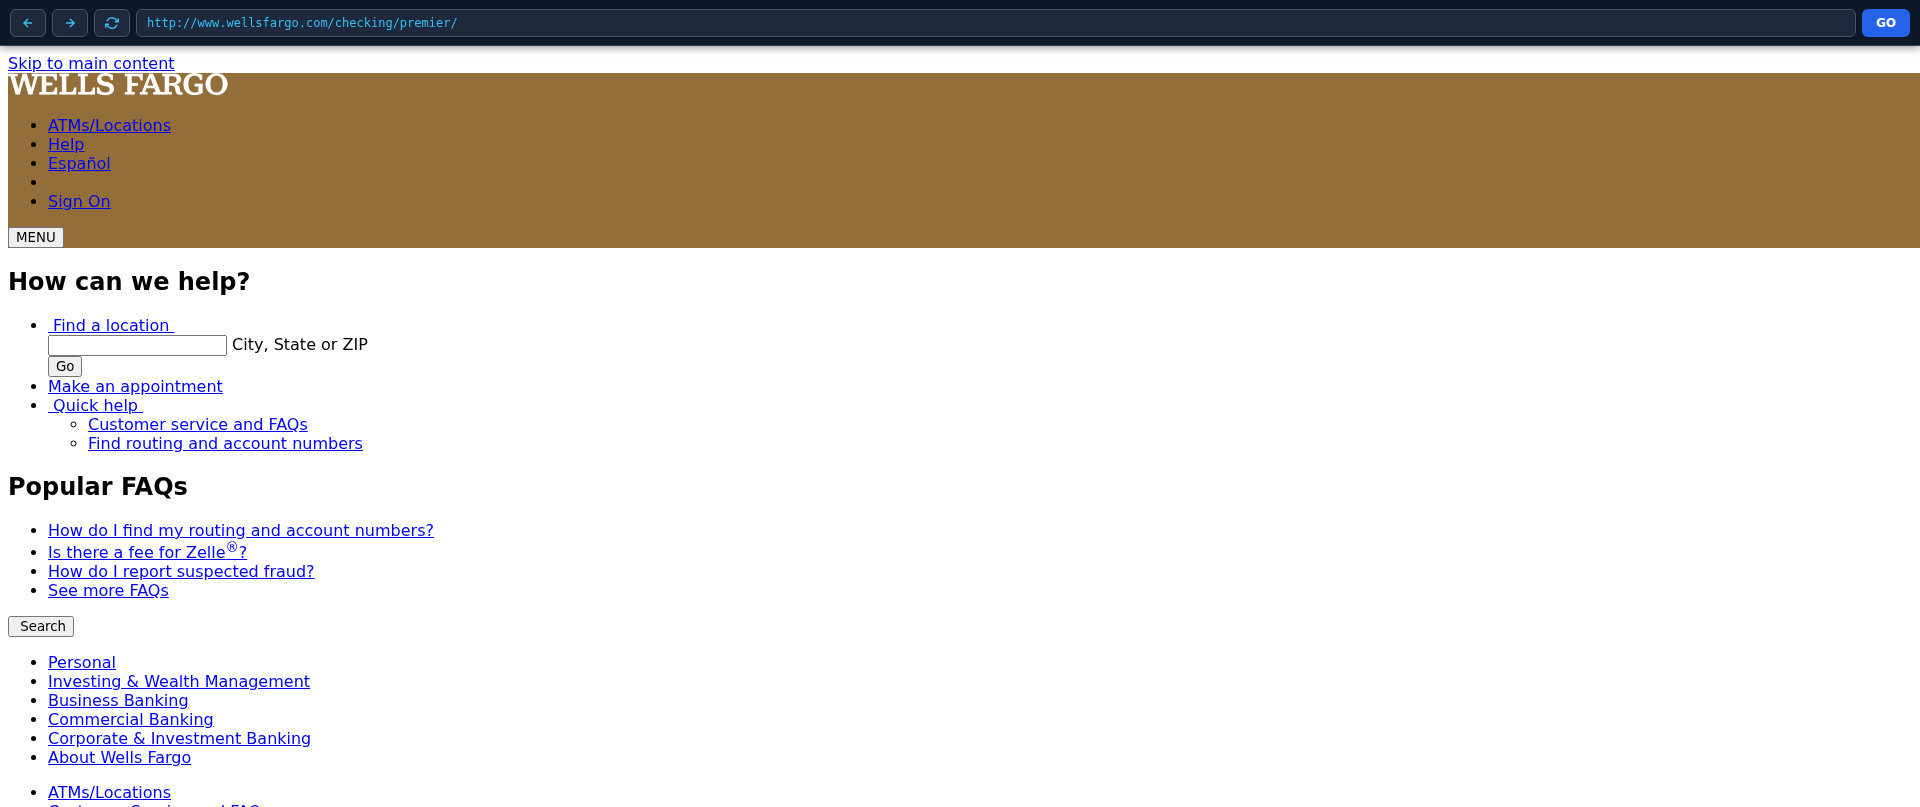
Investigate
Domain
webproxy.goku8.workers.dev1 CT host on apex
 urlscan
 VirusTotal
 Whois
IP
188.114.96.3
 ipinfo
 Greynoise
URL
https://webproxy.goku8.workers.dev/http://www.wellsfargo.co…
Phishunt analysis Beta
40
high suspicion likely_phishingheuristic risk score · not a probability
Why?
- +6.1 Google Safe Browsing
- +5.3 Keyword match
- +5.1 Site cluster
- +4.5 Brand in title
- +4.1 Brand in screenshot
- +3.4 Shared IP cluster
- +3.2 Brand favicon
- +3.0 OpenPhish
- +1.1 ASN reputation
- +1.1 No CSP header
- +0.6 Brand impersonation in path
- +0.6 Suspicious TLD
- +0.5 Young certificate
- +0.5 Long domain
- +0.3 Free CA
- +0.3 Deep subdomain
- +0.1 External scripts
21 signals fired · detector v3.0.0
AI analysis AIBeta
Credential harvesting
Proxies the real Wells Fargo checking page through a Cloudflare Workers host, an adversary-in-the-middle setup that can capture banking credentials. Listed by OpenPhish and flagged by Google Safe Browsing.
Brand impersonation in pathOpenPhishPaaS host
AI-generated from stored detector signals - the AI never visited the site. · 2026-11-12 · confidence 90%
Domain & Network
Whois
Registrar
CloudFlare, Inc.
Network
IP
188.114.96.3 Cloudflare CDN
Country
 United States
Hosting
Cloudflare, Inc.
ASN
AS13335
TLS Cert
YE2
GSB category: SOCIAL_ENGINEERING
CleanPhishTank · TweetFeed · urlscan.io
Requests
Resources
Observables
Related websites
Report this phishing
 Brand owner
Wells Fargo
Submit to blocklists