Phishing detection: eu-assets.contentstack.com
WeTransfer Screenshot
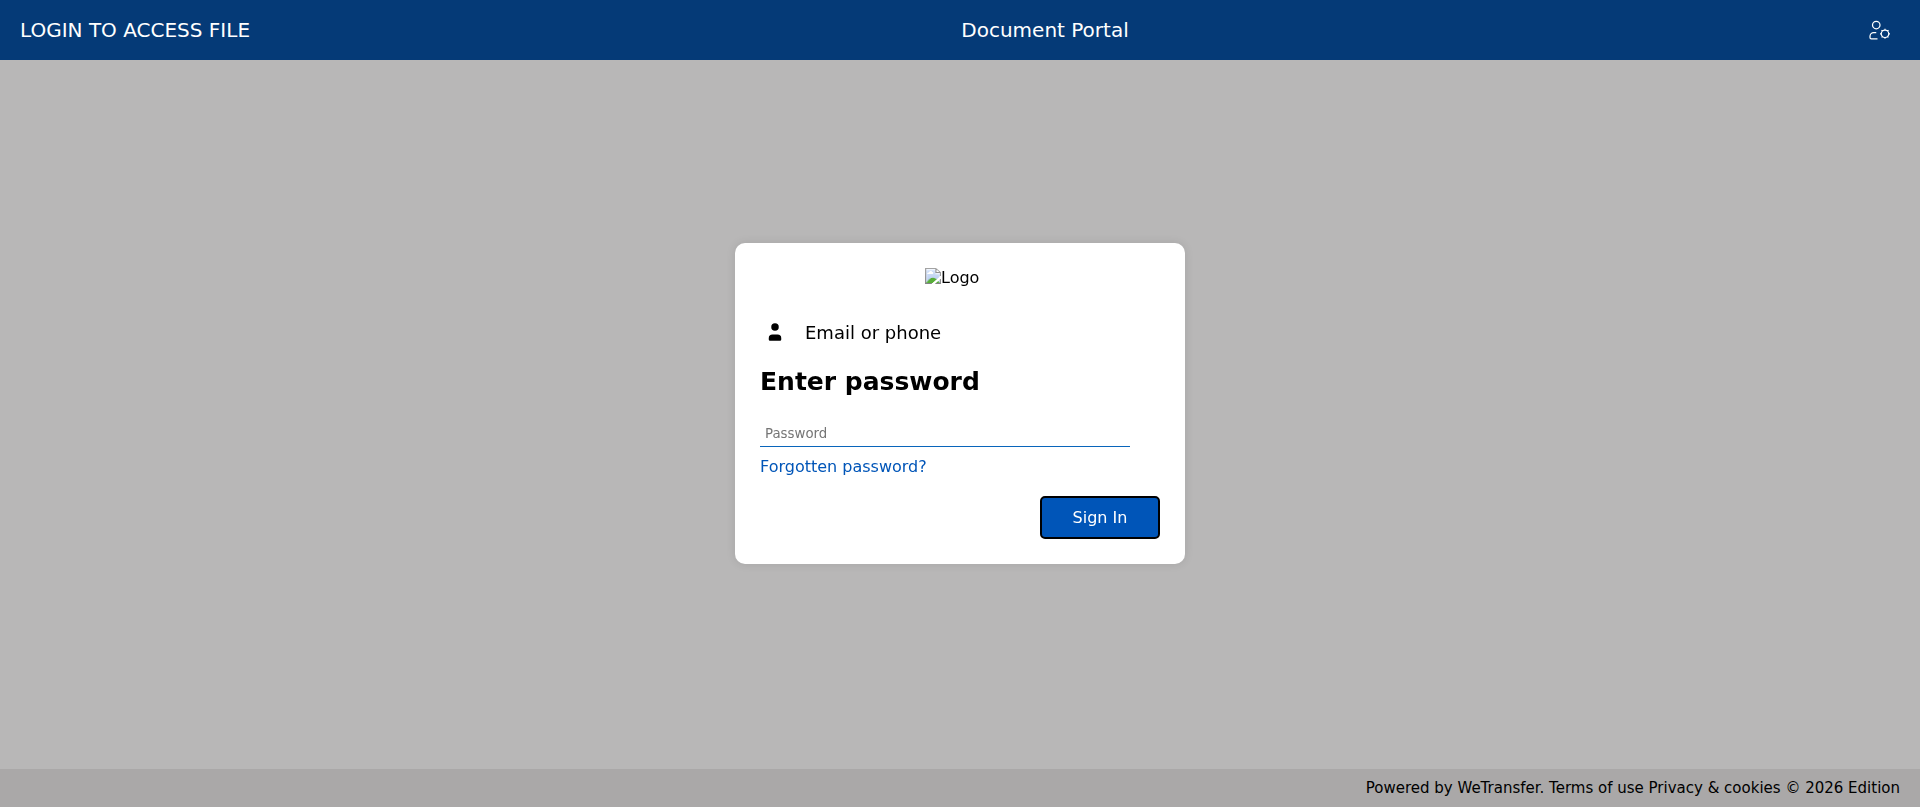
Investigate
Domain
eu-assets.contentstack.com54 CT hosts on apex
 urlscan
 VirusTotal
 Whois
IP
104.17.123.52
 ipinfo
 Greynoise
URL
https://eu-assets.contentstack.com/v3/assets/blt006917f377b…
Phishunt analysis Beta
75
high suspicion likely_phishingheuristic risk score · not a probability
Why?
- +5.3 Keyword match
- +5.1 Site cluster
- +4.1 Brand in screenshot
- +3.9 Password field
- +3.0 OpenPhish
- +2.2 Country mismatch
- +1.8 ASN reputation
- +1.1 No CSP header
- +0.6 Brand impersonation in path
- +0.6 Login text in screenshot
- +0.6 Script exfil endpoint
- +0.5 Long domain
- +0.2 Suspicious TLD
- +0.1 Hyphens
- +0.1 Deep subdomain
- Boosted to 75: Credential exfil kit
17 signals fired · detector v3.0.0
AI analysis AIBeta
Credential harvesting
A WeTransfer phishing page injected into a legitimate Contentstack CDN asset, flagged by OpenPhish. A script exfiltration endpoint is present, indicating credential or data harvesting. The brand appears entirely off-host, suggesting deliberate abuse of trusted CDN infrastructure to evade filters.
Brand impersonation in pathScript exfil endpointOpenPhish
AI-generated from stored detector signals - the AI never visited the site. · 2026-09-21 · confidence 72%
Domain & Network
Whois
Registrar
Dynadot Inc
Network
Country
 United States
Hosting
Cloudflare, Inc.
ASN
AS13335
TLS Cert
GandiCert
External detection
OpenPhish
CleanGoogle Safe Browsing · PhishTank · TweetFeed · urlscan.io
Requests
Resources
Observables
Related websites
Report this phishing
Submit to blocklists