Phishing detection: whatsappdjin.bond
WhatsApp Screenshot
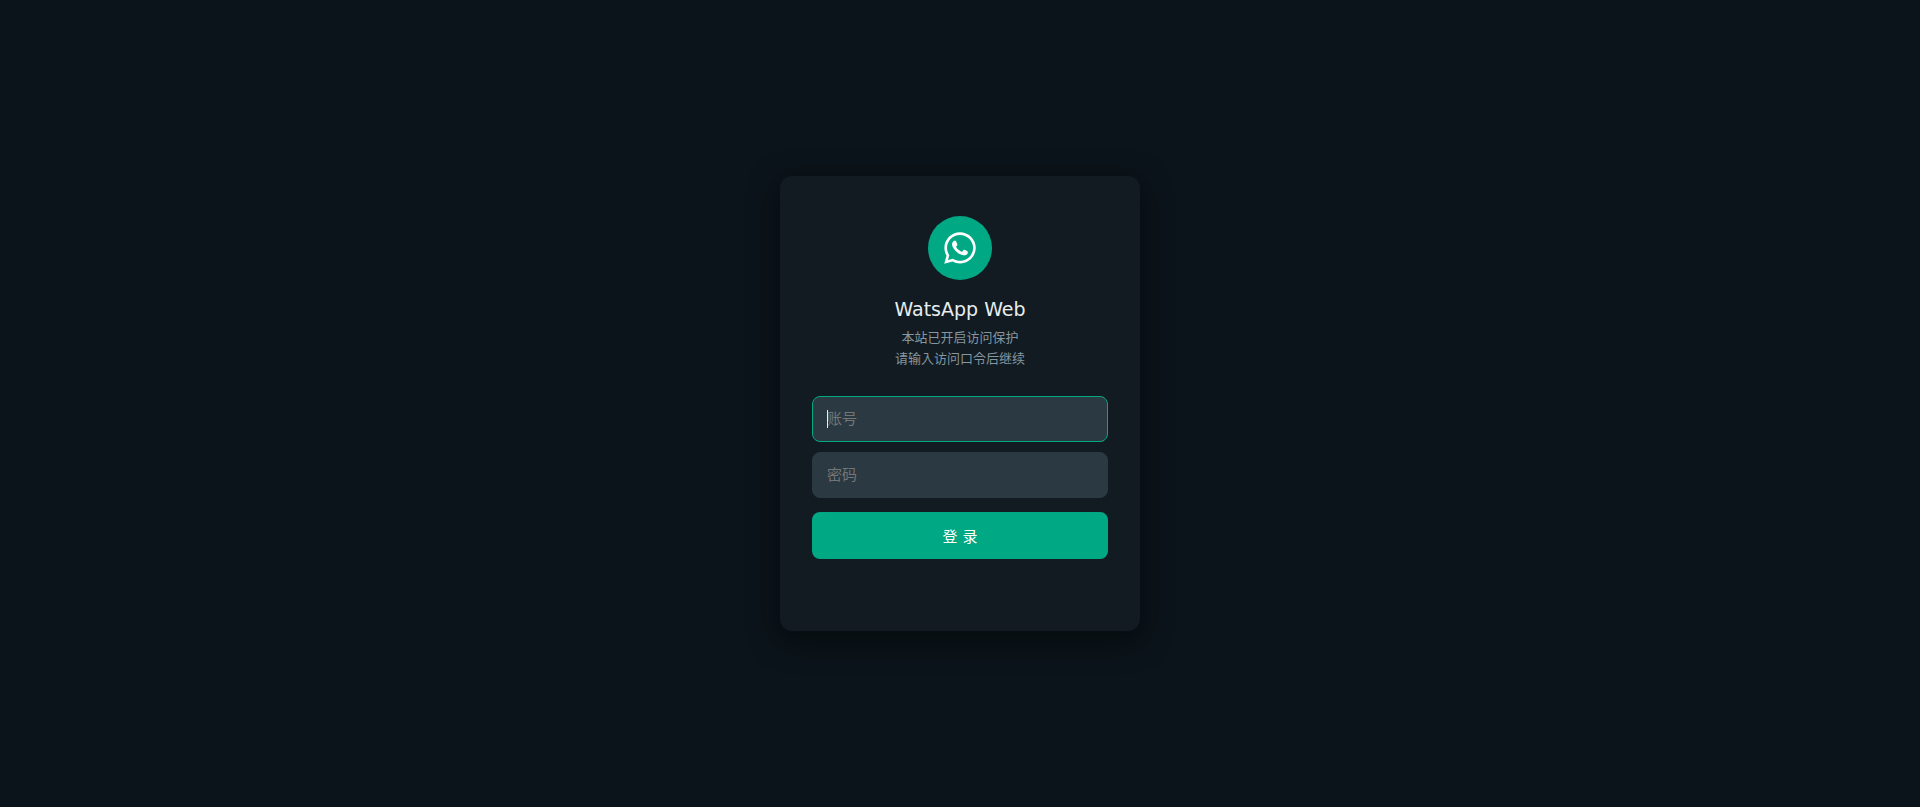
Investigate
Domain
whatsappdjin.bond2 CT hosts on apex
 urlscan
 VirusTotal
 Whois
IP
107.150.39.202
 ipinfo
 Greynoise
URL
https://whatsappdjin.bond
Phishunt analysis Beta
70
high suspicion likely_phishingheuristic risk score · not a probability
Why?
- +6.1 Google Safe Browsing
- +5.3 Keyword match
- +4.0 Young domain
- +3.9 Password field
- +3.7 Brand in domain label
- +3.5 ASN reputation
- +2.0 Site cluster
- +1.7 Shared IP cluster
- +1.3 Suspicious TLD
- +1.1 No CSP header
- +0.9 Young certificate
- +0.9 No registrar lock
- +0.7 Brand in cert SAN
- +0.7 Unrecognised DNS provider
- +0.6 Registrar reputation
- +0.3 Free CA
- +0.3 Long domain
- Boosted to 45: Google-flagged credential form
- Boosted to 70: Credential + brand lookalike
20 signals fired · detector v3.0.0
AI analysis AIBeta
Credential harvesting
Day-old .bond domain embedding the WhatsApp name, with a password input and a brand-named certificate, impersonating WhatsApp to harvest logins. Shares an IP with a sibling domain; flagged by Google Safe Browsing.
Password fieldYoung domainGoogle Safe Browsing
AI-generated from stored detector signals - the AI never visited the site. · 2026-11-19 · confidence 85%
Domain & Network
Whois
Registrar
NameMart Pte. Ltd.
Network
Country
 United States
Hosting
Nocix, LLC
ASN
AS33387
TLS Cert
YR1
External detection
Google Safe Browsing
GSB category: SOCIAL_ENGINEERING
CleanOpenPhish · PhishTank · TweetFeed · urlscan.io
Campaign
Requests
Resources
Observables
Related websites
Report this phishing
Submit to blocklists