Phishing detection: auth.properties
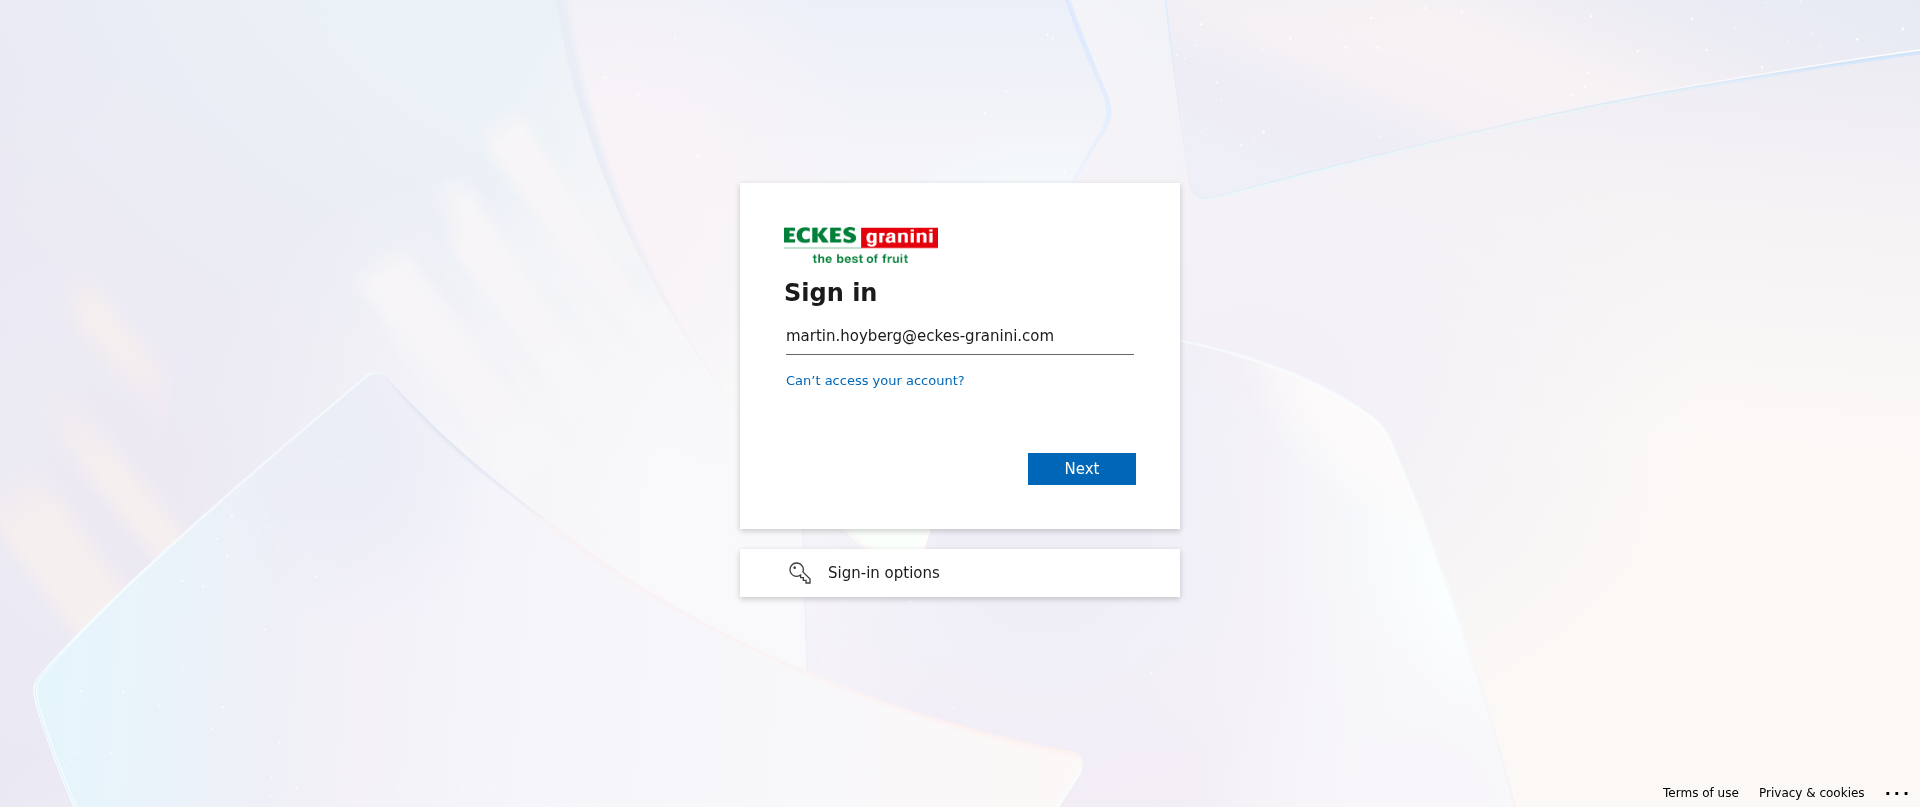
Microsoft Screenshot
Investigate
Domain
auth.properties1 CT host on apex
 urlscan
 VirusTotal
 Whois
IP
212.104.128.1
 ipinfo
 Greynoise
URL
https://auth.properties/E.rU-TDP5DOv4?/microsoftonline/mail…
Phishunt analysis Beta
45
high suspicion likely_phishingheuristic risk score · not a probability
Why?
- +6.1 Google Safe Browsing
- +5.3 Keyword match
- +5.1 Site cluster
- +4.5 Brand in title
- +3.9 Password field
- +3.0 OpenPhish
- +2.2 Country mismatch
- +1.5 ASN reputation
- +1.1 No CSP header
- +0.9 Young certificate
- +0.6 Brand impersonation in path
- +0.6 Login text in screenshot
- +0.6 Suspicious TLD
- +0.3 Free CA
- +0.3 Long domain
- Boosted to 45: Google-flagged credential form
17 signals fired · detector v3.0.0
AI analysis AIBeta
Credential harvesting
Site impersonates Microsoft Online using a mailbox upgrade lure, hosted in Finland via Cloudflare with an obfuscated path embedding a user ID string. Flagged by Google Safe Browsing as social engineering and confirmed malicious by OpenPhish.
Google Safe BrowsingOpenPhishBrand impersonation in path
AI-generated from stored detector signals - the AI never visited the site. · 2026-09-22 · confidence 91%
Domain & Network
Whois
Registrar
Gandi SAS
Network
Country
 Finland
Hosting
Cloudflare, Inc.
ASN
AS13335
TLS Cert
WE1
GSB category: SOCIAL_ENGINEERING
CleanPhishTank · TweetFeed · urlscan.io
Requests
Resources
Observables
Related websites
Report this phishing
 Brand owner
Microsoft
Submit to blocklists