Suspicious
Phishings targeting Trezor
Suspicious and active websites
Phishings targeting Trezor
Suspicious and active websites
Active
6
New (7d)
2
Trend (7d)
↑100%
- Countries
 United States
Possible campaigns
1 of these is in a suspected cluster
4e4f2ab7bba1
Suspicious sites — confidence is not always 100%. Use for Threat Hunting or watchlists.
| Last check (UTC) | First seen (UTC) ▾ | URL | Screenshot | Flags | Details |
|---|---|---|---|---|---|
| 2026-09-14 03:30 | 2026-09-13 13:02 | 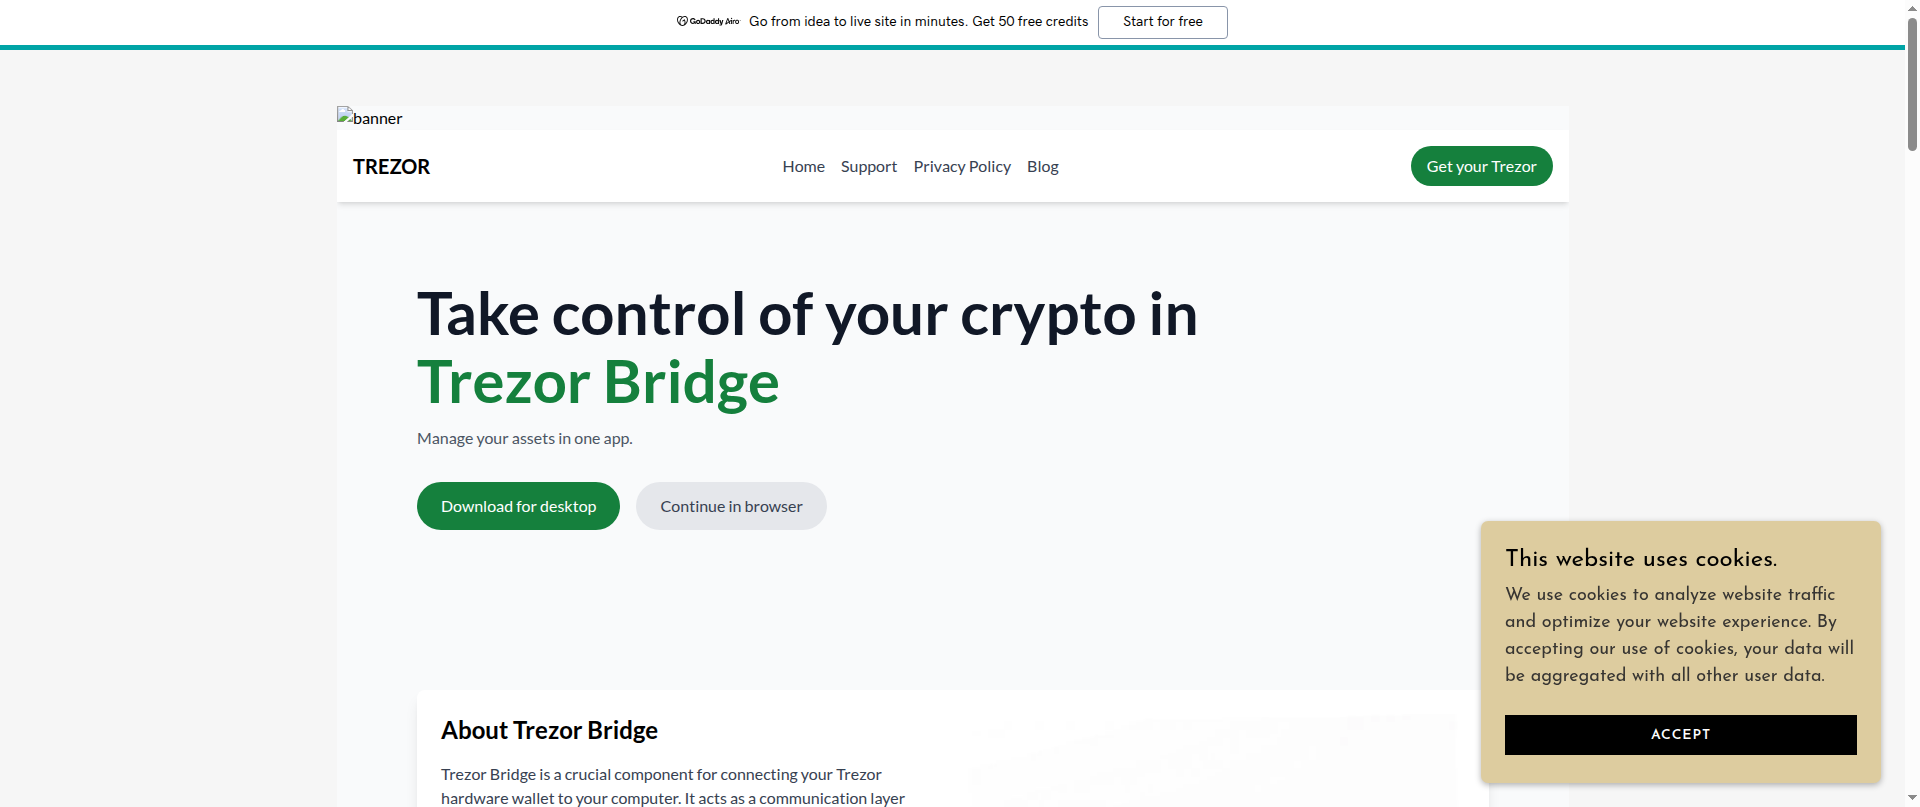 |
OpenPhish | Details | |
| 2026-09-14 03:30 | 2026-09-13 13:02 | 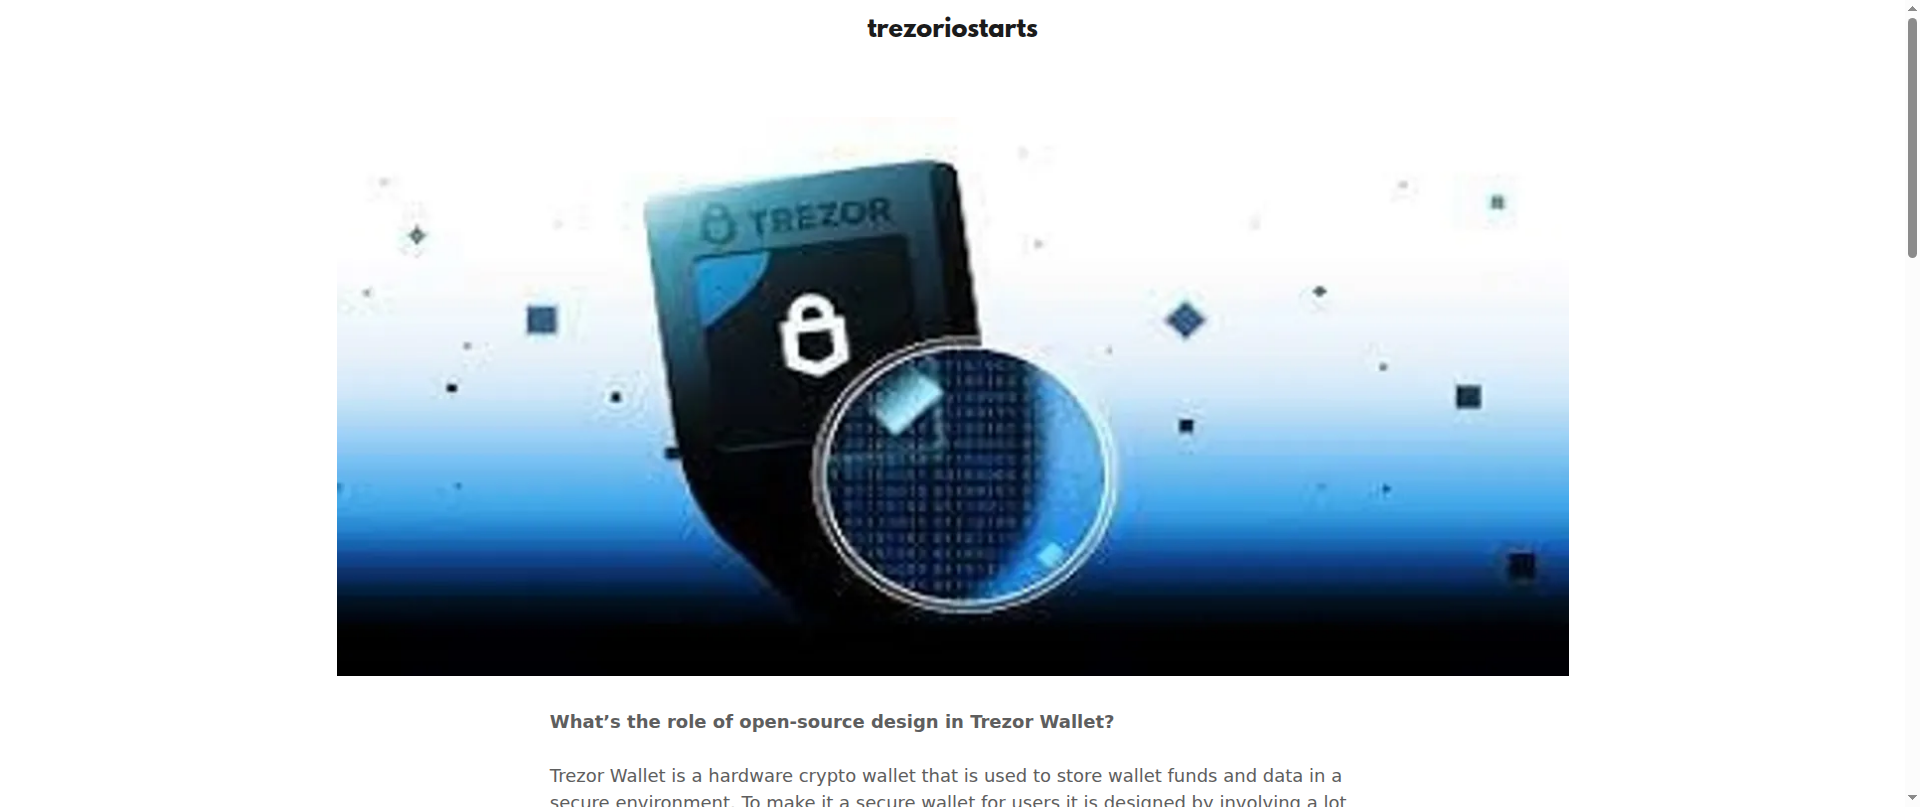 |
OpenPhish | Details | |
| 2026-09-14 03:30 | 2026-09-02 13:04 | 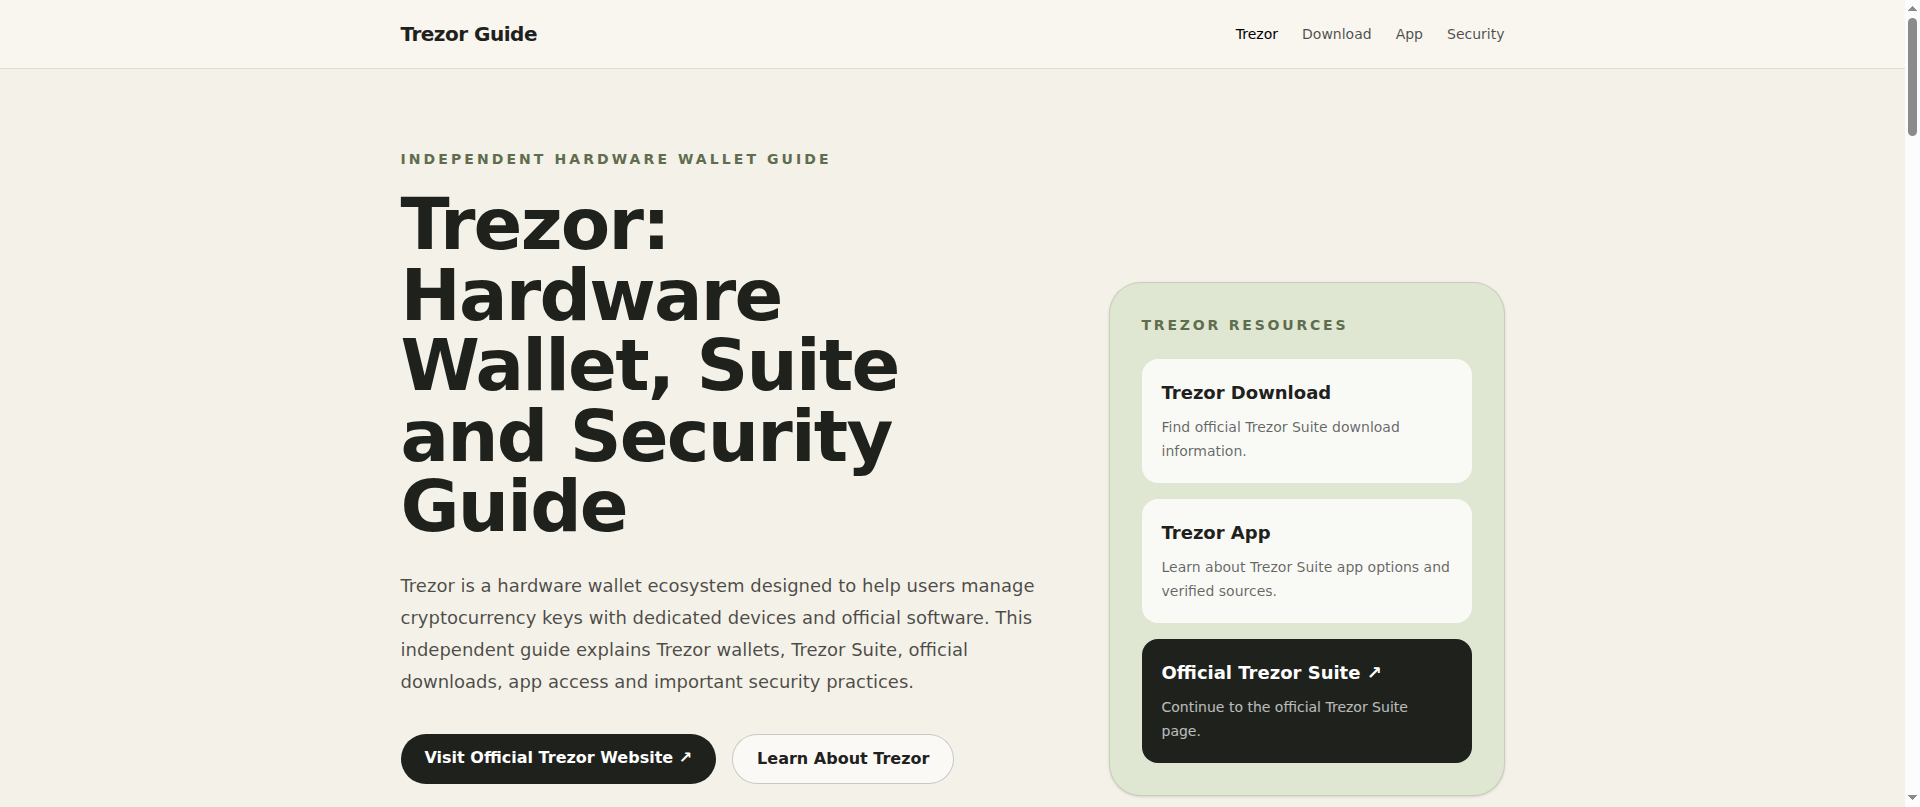 |
OpenPhish | Details | |
| 2026-09-14 03:30 | 2026-08-26 01:02 | 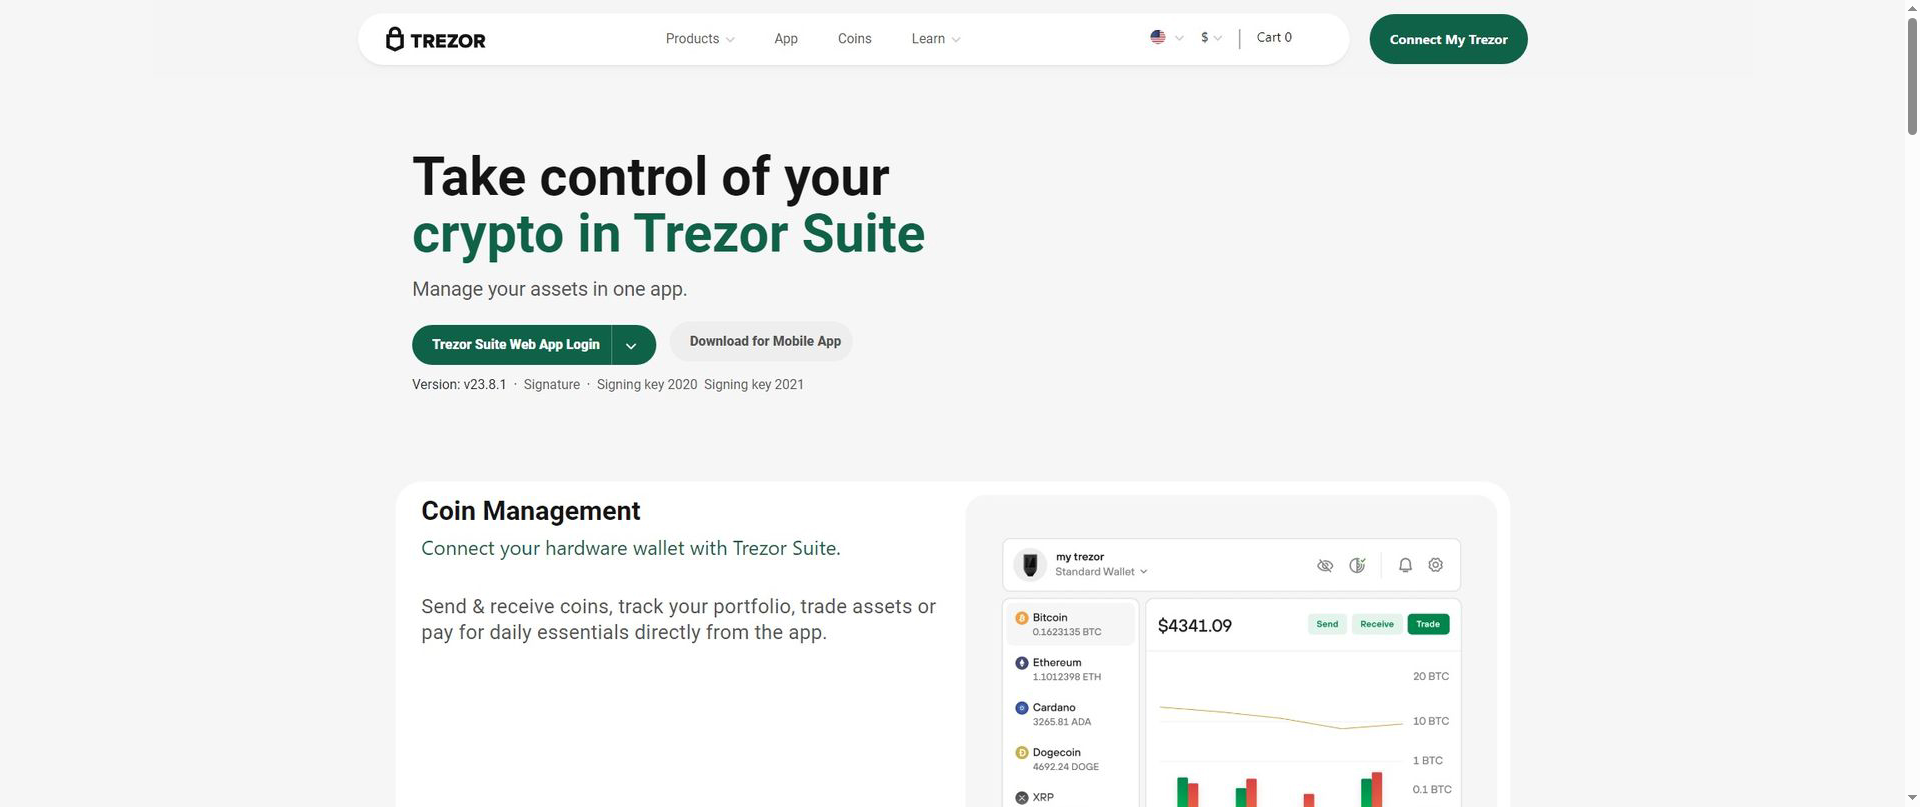 |
OpenPhish urlscan | Details | |
| 2026-09-14 03:30 | 2026-08-13 13:02 | 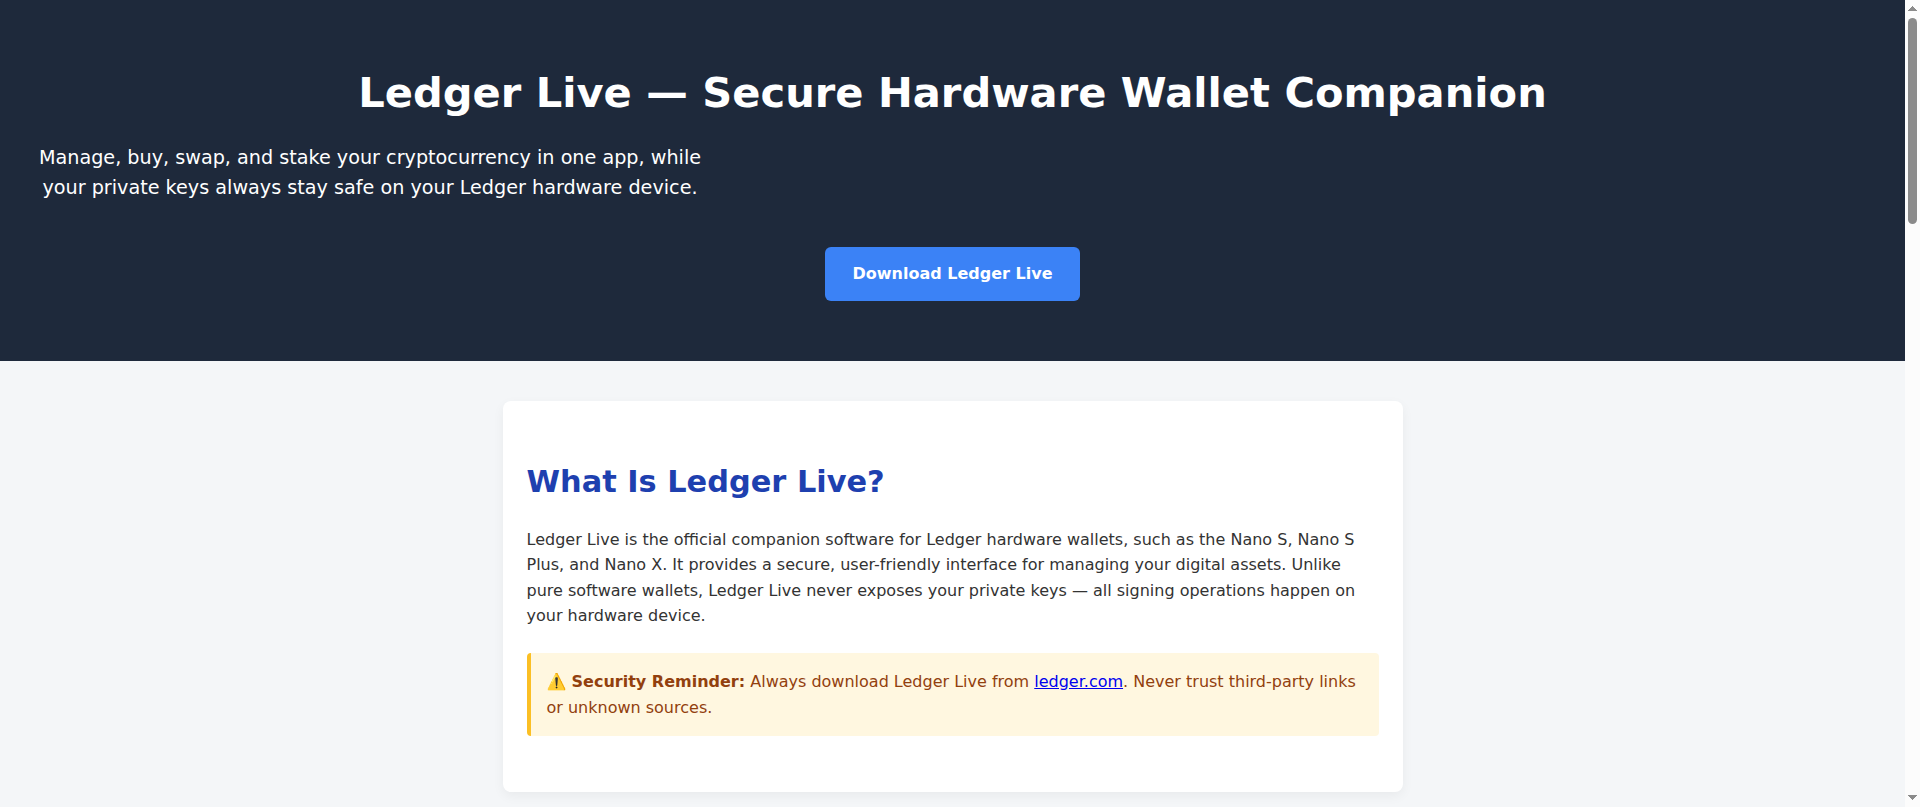 |
OpenPhish urlscan | Details | |
| 2026-09-14 03:30 | 2026-08-07 01:01 |  |
OpenPhish | Details |
Suspicious sites — confidence is not always 100%. Use for Threat Hunting or watchlists.
| URL | Screenshot | Details |
|---|---|---|
| https://welcome-trezor-bridge…
OpenPhish |
|
Details |
| https://trezoriostarts.godadd…
OpenPhish |
|
Details |
| https://trezorguide.vercel.app
OpenPhish |
|
Details |
| https://docs-trezor-app.pages…
OpenPhish urlscan |
|
Details |
| https://web-trezor-io-start-u…
OpenPhish urlscan |
|
Details |
| http://trezor-login-us-auth-s…
OpenPhish |
|
Details |
AIHow to verify a real Trezor URL
- Legitimate Trezor URLs always end in
trezor.io(e.g.www.trezor.io,account.trezor.io). Anything else — including look-alike typosquats, hyphenated variations, or unfamiliar TLDs like.xyz/.top/.vip— is not Trezor. - The padlock icon proves TLS is active, not that the site is safe. Free DV certificates are issued to attackers in minutes; every active site listed above has a valid TLS certificate.
- If you got the link from email, SMS, or social media, do not click it. Open
trezor.iofrom your browser bookmark or type the domain manually. - Real Trezor pages almost never ask for credentials immediately after clicking from a message — treat any such redirect as a phishing attempt until the domain is verified.