Phishing detection: panjabi.amar-dokan.com
Wells Fargo Screenshot
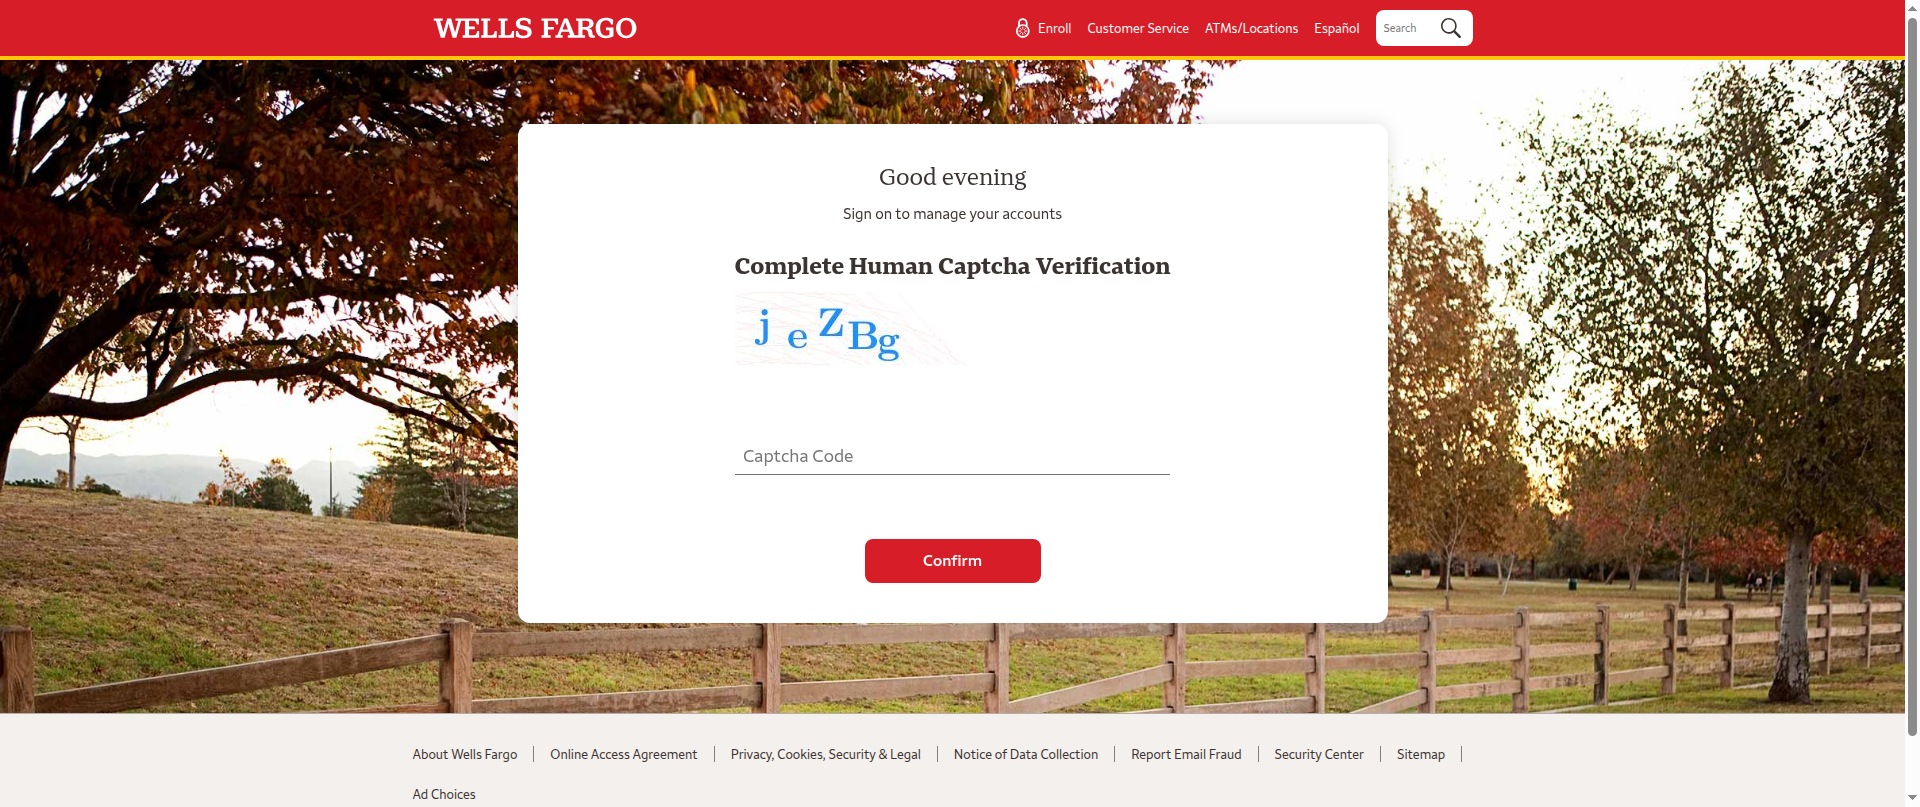
Investigate
Domain
panjabi.amar-dokan.com1 CT host on apex
 urlscan
 VirusTotal
 Whois
IP
163.227.239.17
 ipinfo
 Greynoise
URL
http://panjabi.amar-dokan.com/Wellsfargologs
Phishunt analysis Beta
32
medium suspicion suspiciousheuristic risk score · not a probability
Why?
- +6.1 Google Safe Browsing
- +5.3 Keyword match
- +4.5 Brand in title
- +4.1 Brand in screenshot
- +3.0 OpenPhish
- +2.2 Country mismatch
- +1.1 ASN reputation
- +1.1 No CSP header
- +1.1 No HSTS header
- +0.8 Young domain
- +0.6 Brand impersonation in path
- +0.6 Registrar reputation
- +0.5 Long domain
- +0.3 Free CA
- +0.2 Suspicious TLD
- +0.1 Hyphens
- +0.1 Deep subdomain
20 signals fired · detector v3.0.0
AI analysis AIBeta
Credential harvesting
Wells Fargo banking credential harvesting page hosted on an unrelated domain in Bangladesh. The URL path explicitly references Wells Fargo and the page presents a same-origin login form. Flagged by Google Safe Browsing as social engineering and confirmed by OpenPhish.
Google Safe BrowsingOpenPhishSame-origin form
AI-generated from stored detector signals - the AI never visited the site. · 2026-09-18 · confidence 78%
Domain & Network
Whois
Registrar
Spaceship, Inc.
Network
Country
 Bangladesh
Hosting
Wolast Technologies
ASN
AS150142
TLS Cert
YR1
GSB category: SOCIAL_ENGINEERING
CleanPhishTank · TweetFeed · urlscan.io
Requests
Resources
Observables
Related websites
Report this phishing
 Brand owner
Wells Fargo
Submit to blocklists