Phishing detection: exodusathleticclub.com
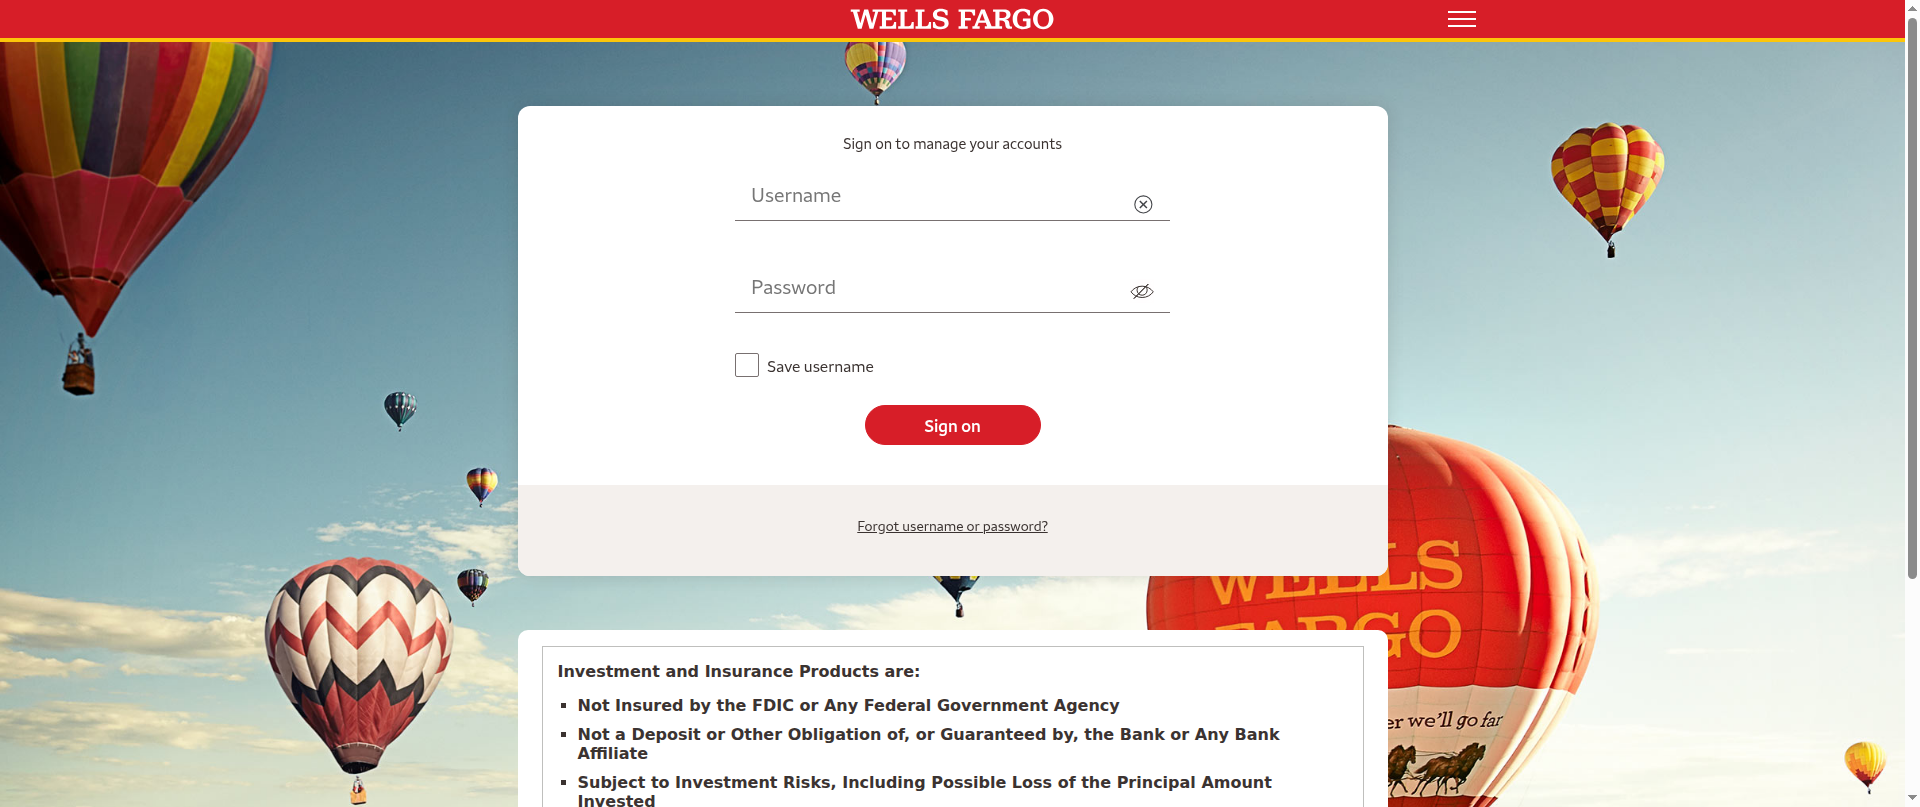
Wells Fargo Screenshot
Investigate
Domain
exodusathleticclub.com2 CT hosts on apex
 urlscan
 VirusTotal
 Whois
IP
151.101.130.159
 ipinfo
 Greynoise
URL
https://exodusathleticclub.com/wp-content/themes/wordpress/…
Phishunt analysis Beta
70
high suspicion likely_phishingheuristic risk score · not a probability
Why?
- +6.1 Google Safe Browsing
- +5.3 Keyword match
- +5.1 Site cluster
- +4.5 Brand in title
- +4.1 Brand in screenshot
- +3.9 Password field
- +3.7 Brand in domain label
- +3.0 OpenPhish
- +1.1 ASN reputation
- +1.1 No CSP header
- +1.1 No HSTS header
- +0.9 Young certificate
- +0.6 Login text in screenshot
- +0.5 Long domain
- +0.3 Free CA
- +0.2 External scripts
- +0.2 Suspicious TLD
- Boosted to 45: Google-flagged credential form
- Boosted to 70: Credential + brand lookalike
22 signals fired · detector v3.0.0
AI analysis AIBeta
Credential harvesting
Wells Fargo phishing page under a folder named for a one-time passcode download, planted on a compromised fitness club WordPress site. It has a password field and a same-origin form to capture credentials. Flagged by Google Safe Browsing (social engineering) and OpenPhish.
Google Safe BrowsingPassword fieldBrand in domain label
AI-generated from stored detector signals - the AI never visited the site. · 2026-10-11 · confidence 90%
Domain & Network
Whois
Registrar
GoDaddy.com, LLC
Network
IP
151.101.130.159 Fastly CDN
Country
 United States
Hosting
Fastly, Inc.
ASN
AS54113
TLS Cert
YR1
GSB category: SOCIAL_ENGINEERING
CleanPhishTank · TweetFeed · urlscan.io
Requests
Resources
Observables
Related websites
Report this phishing
 Network / ASN
Fastly, Inc.
 Brand owner
Wells Fargo
Submit to blocklists