Phishing detection: wetransfer-1.vercel.app
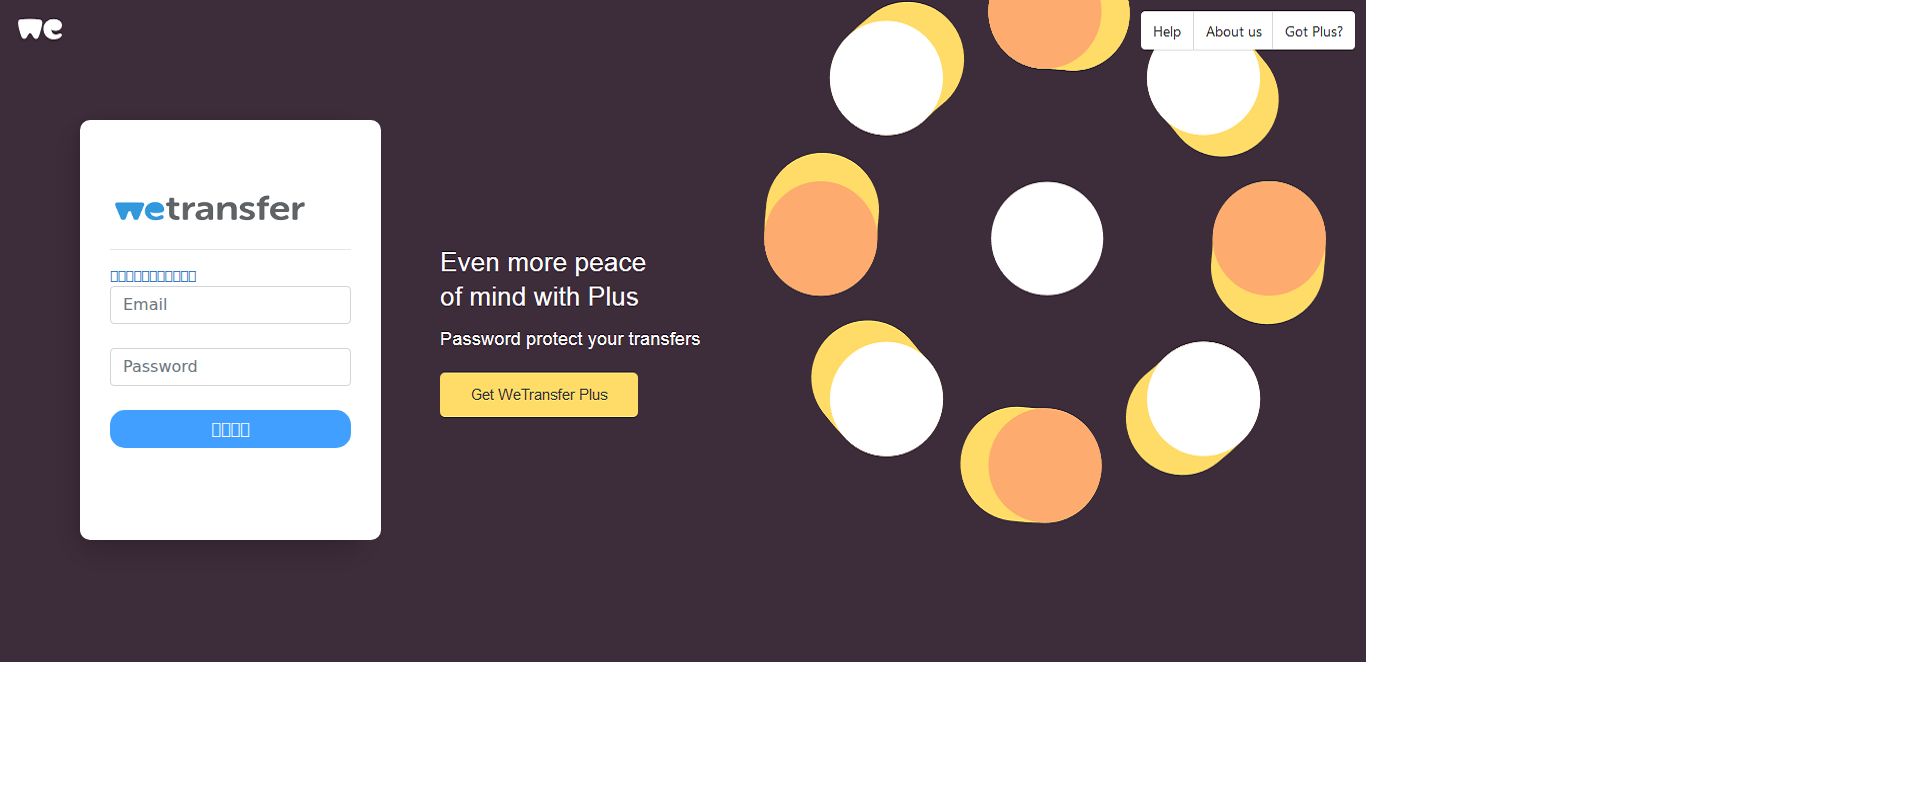
WeTransfer Screenshot
Investigate
Domain
wetransfer-1.vercel.app0 CT hosts on apex
 urlscan
 VirusTotal
 Whois
IP
216.198.79.195
 ipinfo
 Greynoise
URL
http://wetransfer-1.vercel.app
Phishunt analysis Beta
75
high suspicion likely_phishingheuristic risk score · not a probability
Why?
- +5.3 Keyword match
- +5.1 Site cluster
- +4.5 Brand in title
- +4.1 Brand in screenshot
- +3.9 Password field
- +3.7 Brand in domain label
- +3.4 Cert reuse
- +3.4 Shared IP cluster
- +3.0 OpenPhish
- +2.2 Country mismatch
- +2.0 Young domain
- +1.6 Favicon (kit)
- +1.1 ASN reputation
- +1.1 No CSP header
- +0.6 Login text in screenshot
- +0.6 Script exfil endpoint
- +0.6 Suspicious TLD
- +0.5 Long domain
- +0.3 Free CA
- +0.2 External scripts
- +0.1 Hyphens
- +0.1 Deep subdomain
- Boosted to 75: Credential exfil kit
28 signals fired · detector v3.0.0
AI analysis AIBeta
Credential harvesting
Fake WeTransfer page on a Vercel free-hosting subdomain with the brand in the hostname and title, and a password input field. Listed by OpenPhish, it appears to harvest login credentials under the guise of a file-sharing download.
Password fieldBrand in domain labelOpenPhish
AI-generated from stored detector signals - the AI never visited the site. · 2026-10-15 · confidence 88%
Domain & Network
Whois
Registrar
Tucows Domains Inc
Network
Country
 United States
Hosting
Amazon.com, Inc.
ASN
AS16509
TLS Cert
WR1
External detection
OpenPhish
CleanGoogle Safe Browsing · PhishTank · TweetFeed · urlscan.io
Requests
Resources
Observables
Related websites
Report this phishing
 Network / ASN
Amazon.com, Inc.
Submit to blocklists